Netinfo Security ›› 2026, Vol. 26 ›› Issue (7): 1028-1043.doi: 10.3969/j.issn.1671-1122.2026.07.003
Previous Articles Next Articles
Enhancing malware detection via multi-view sensitivity mining and Sens-FiLM modulation
Kou Liang( ), Tu Guoxuan, Pan Xiaochen, Zhang Jilin
College of Cyberspace ,Hangzhou Dianzi University Hangzhou 310018, China
-
Received:2026-05-14Online:2026-07-10Published:2026-09-03 -
Contact:Kou Liang E-mail:kouliang@hdu.edu.cn

CLC Number:
Cite this article
Kou Liang, Tu Guoxuan, Pan Xiaochen, Zhang Jilin. Enhancing malware detection via multi-view sensitivity mining and Sens-FiLM modulation[J]. Netinfo Security, 2026, 26(7): 1028-1043.
share this article
Add to citation manager EndNote|Ris|BibTeX
URL: http://netinfo-security.org/EN/10.3969/j.issn.1671-1122.2026.07.003
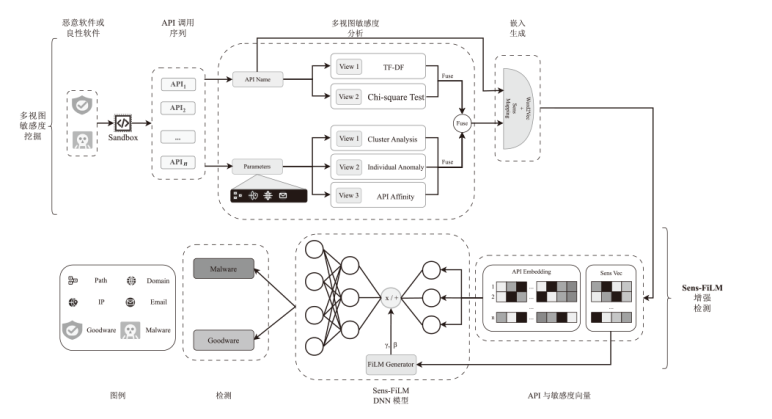
| API 调用 | 输入参数 | API表现类型 | 敏感度 |
|---|---|---|---|
| GetFileAttributes | C:\Users\Default\AppData\Roaming\malicious.dll | 查询文件属性 | 低 |
| LoadLibrary | C:\Users\Default\AppData\Roaming\malicious.dll | 加载动态链接库 | 中 |
| CreateService | C:\Users\Default\AppData\Roaming\malicious.dll | 创建自动启动服务 | 高 |
| ReadFile | C:\Windows\System32\config\SAM | 读取文件内容 | 低 |
| RegLoadKey | C:\Windows\System32\config\SAM | 加载注册表元数据文件 | 中 |
| SetFileAttributes | C:\Windows\System32\config\SAM | 修改文件属性 | 高 |
| 数据集 | 方法 | 是否使用参数 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|---|---|
| 验证集 | 文献[ | 否 | 86.63% | 85.27% | 88.81% | 86.92% |
| 文献[ | 否 | 96.40% | 96.56% | 96.21% | 96.40% | |
| 文献[ | 是 | 97.97% | 98.69% | 97.26% | 97.97% | |
| 文献[ | 是 | 98.16% | 98.66% | 97.66% | 98.16% | |
| MvSe-Mal (TextCNN) | 是 | 98.67% | 99.18% | 96.80% | 97.98% | |
| 测试集 | 文献[ | 否 | 67.11% | 61.62% | 90.70% | 73.38% |
| 文献[ | 否 | 85.54% | 94.98% | 75.04% | 83.84% | |
| 文献[ | 是 | 91.76% | 97.64% | 85.59% | 91.22% | |
| 文献[ | 是 | 98.52% | 98.63% | 98.41% | 98.52% | |
| MvSe-Mal (TextCNN) | 是 | 98.40% | 98.92% | 96.25% | 97.56% |
| 方法 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|
| Naive Bayes | 83.62% | 86.10% | 80.20% | 83.04% |
| KNN | 78.10% | 94.70% | 59.54% | 73.11% |
| Logistic | 89.27% | 91.12% | 87.03% | 89.03% |
| DT | 96.44% | 97.91% | 94.92% | 96.39% |
| TextCNN | 99.56% | 99.63% | 99.49% | 99.56% |
| BiLSTM | 97.47% | 97.97% | 96.96% | 97.46% |
| MvSe-Mal-BiLSTM | 96.26% | 94.03% | 94.79% | 94.41% |
| MvSe-Mal-TextCNN | 99.39% | 99.93% | 98.24% | 99.08% |
| 方法 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|
| Naive Bayes | 71.85% | 82.36% | 55.60% | 66.38% |
| KNN | 65.86% | 91.07% | 35.17% | 50.74% |
| Logistic | 71.69% | 84.80% | 52.85% | 65.12% |
| DT | 76.32% | 90.28% | 58.99% | 71.36% |
| TextCNN | 95.54% | 97.65% | 93.33% | 95.44% |
| BiLSTM | 84.16% | 93.36% | 73.55% | 82.28% |
| MvSe-Mal-BiLSTM | 96.48% | 94.22% | 95.30% | 94.76% |
| MvSe-Mal-TextCNN | 98.40% | 98.92% | 96.25% | 97.56% |
| 方法 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|
| 原始API序列 | 94.10% | 98.70% | 83.40% | 90.41% |
| 单视图标注的API序列 | 96.20% | 97.03% | 91.40% | 94.13% |
| 多视图标注的API序列 | 95.67% | 95.69% | 91.10% | 93.34% |
| 与Sens-FiLM相结合的 多视图标注的API序列 | 96.20% | 93.60% | 95.10% | 94.35% |
| 方法 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|
| 原始API序列 | 93.58% | 97.92% | 82.50% | 89.55% |
| 单视图标注的API序列 | 95.73% | 96.78% | 90.20% | 93.37% |
| 多视图标注的API序列 | 95.82% | 96.59% | 90.65% | 93.53% |
| 与Sens-FiLM相结合的多视图标注的API序列 | 96.48% | 94.22% | 95.30% | 94.76% |
| [1] | Michalowski M. 50+ Malware statistics for 2025[EB/OL]. (2026-01-01) [2026-04-24]. https://spacelift.io/blog/malware-statistics#malware-impact-and-costs. |
| [2] | Baghirov E. Techniques of malware detection: research review[C]//2021 IEEE 15th International Conference on Application of Information and Communication Technologies (AICT). New York: IEEE, 2021: 1-6. |
| [3] |
Meng Zhaoyi, Zhang Jiale, Guo Jiaqi, et al. Detecting android malware by visualizing APP behaviors from multiple complementary views[J]. IEEE Transactions on Information Forensics and Security, 2025, 20: 2915-2929.
doi: 10.1109/TIFS.2025.3547301 URL |
| [4] |
Ding Yuxin, Dai Wei, Yan Shengli, et al. Control flow-based opcode behavior analysis for malware detection[J]. Computers & Security, 2014, 44: 65-74.
doi: 10.1016/j.cose.2014.04.003 URL |
| [5] |
Cesare S, Xiang Yang, Zhou Wanlei. Control flow-based malware variantdetection[J]. IEEE Transactions on Dependable and Secure Computing, 2014, 11(4): 307-317.
doi: 10.1109/TDSC.2013.40 URL |
| [6] | Sharif M I, Lanzi A, Giffin J T, et al. Impeding malware analysis using conditional code obfuscation[EB/OL]. (2026-01-01) [2026-04-24]. https://air.unimi.it/handle/2434/455576. |
| [7] |
Chen Xiaohui, Hao Zhiyu, Li Lun, et al. CruParamer: learning on parameter-augmented API sequences for malware detection[J]. IEEE Transactions on Information Forensics and Security, 2022, 17: 788-803.
doi: 10.1109/TIFS.2022.3152360 URL |
| [8] |
Chen Tieming, Zeng Huan, Lyu Mingqi, et al. CTIMD: cyber threat intelligence enhanced malware detection using API call sequences with parameters[J]. Computers & Security, 2024, 136: 103518.
doi: 10.1016/j.cose.2023.103518 URL |
| [9] |
Zhang Zhaoqi, Qi Panpan, Wang Wei. Dynamic malware analysis with feature engineering and feature learning[J]. Proceedings of the AAAI Conference on Artificial Intelligence, 2020, 34(1): 1210-1217.
doi: 10.1609/aaai.v34i01.5474 URL |
| [10] |
Zhu Huijuan, Chen Xilong, Wang Liangmin, et al. A dynamic analysis-powered explanation framework for malware detection[J]. IEEE Transactions on Knowledge and Data Engineering, 2024, 36(12): 7483-7496.
doi: 10.1109/TKDE.2024.3436891 URL |
| [11] |
Li Ce, Lyu Qiujian, Li Ning, et al. A novel deep framework for dynamic malware detection based on API sequence intrinsic features[J]. Computers & Security, 2022, 116: 102686.
doi: 10.1016/j.cose.2022.102686 URL |
| [12] | Cui Lei, Cui Jiancong, Ji Yuede, et al. API2Vec: learning representations of API sequences for malware detection[C]// The 32nd ACM SIGSOFT International Symposium on Software Testing and Analysis. New York: ACM, 2023: 261-273. |
| [13] |
Wong G W, Huang Yiting, Guo Yingren, et al. Attention-based API locating for malware techniques[J]. IEEE Transactions on Information Forensics and Security, 2024, 19: 1199-1212.
doi: 10.1109/TIFS.2023.3330337 URL |
| [14] |
Babu S, Singh V. BD-MDLC: behavior description-based enhanced malware detection for windows environment using longformer classifier[J]. Computers & Security, 2024, 146: 104031.
doi: 10.1016/j.cose.2024.104031 URL |
| [15] |
Li Ce, Cheng Zijun, Zhu He, et al. DMalNet: dynamic malware analysis based on API feature engineering and graph learning[J]. Computers & Security, 2022, 122: 102872.
doi: 10.1016/j.cose.2022.102872 URL |
| [16] |
Trizna D, Demetrio L, Biggio B, et al. Nebula: self-attention for dynamic malware analysis[J]. IEEE Transactions on Information Forensics and Security, 2024, 19: 6155-6167.
doi: 10.1109/TIFS.2024.3409083 URL |
| [17] | Agrawal R, Stokes J W, Marinescu M, et al. Neural sequential malware detection with parameters[C]// 2018 IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP). New York: IEEE, 2018: 2656-2660. |
| [18] |
Kanungo T, Mount D M, Netanyahu N S, et al. An efficient K-Means clustering algorithm: analysis and implementation[J]. IEEE Transactions on Pattern Analysis and Machine Intelligence, 2002, 24(7): 881-892.
doi: 10.1109/TPAMI.2002.1017616 URL |
| [19] |
Zhao Ying, Karypis G, Fayyad U. Hierarchical clustering algorithms for document datasets[J]. Data Mining and Knowledge Discovery, 2005, 10(2): 141-168.
doi: 10.1007/s10618-005-0361-3 URL |
| [20] | Schubert E, Sander J, Ester M, et al. DBSCAN revisited, revisited: why and how you should (still) use DBSCAN[J]. ACM Transactions on Database Systems, 2017, 42(3): 1-21. |
| [21] | Ng A, Jordan M, Weiss Y. On spectral clustering: analysis and an algorithm[EB/OL]. [2026-04-24]. https://proceedings.neurips.cc/paper_files/paper/2001/file/801272ee79cfde7fa5960571fee36b9b-Paper.pdf. |
| [22] | Liu F T, Ting Kaiming, Zhou Zhihua. Isolation forest[C]// 2008 Eighth IEEE International Conference on Data Mining. New York: IEEE, 2008: 413-422. |
| [23] | Perez E, Strub F, De V H, et al. FiLM: visual reasoning with a general conditioning layer[J]. Proceedings of the AAAI Conference on Artificial Intelligence, 2018, 32(1): 3942-3951. |
| [24] | Zhang Shu, Zheng Dequan, Hu Xinchen, et al. Bidirectional long short-term memory networks for relation classification[C]// The 29th Pacific Asia Conference on Language, Information and Computation. Shanghai: PACLIC, 2015: 73-78. |
| [25] | Kim Y. Convolutional neural networks for sentence classification[C]// The 2014 Conference on Empirical Methods in Natural Language Processing (EMNLP). Stroudsburg: ACL, 2014: 1746-1751. |
| [26] | Datacon 2019. Malicious-code-dataset[DS/OL]. (2019-01-01) [2026-04-24]. https://github.com/kericwy1337. |
| [27] |
Amer E, Zelinka I. A dynamic windows malware detection and prediction method based on contextual understanding of API call sequence[J]. Computers & Security, 2020, 92: 101760.
doi: 10.1016/j.cose.2020.101760 URL |
| [28] |
Ndibanje B, Kim K H, Kang Y J, et al. Cross-method-based analysis and classification of malicious behavior by API calls extraction[J]. Applied Sciences, 2019, 9(2): 239.
doi: 10.3390/app9020239 URL |
| [29] |
Cieslak M C, Castelfranco A M, Roncalli V, et al. T-distributed stochastic neighbor embedding (t-SNE): a tool for eco-physiological transcriptomic analysis[J]. Marine Genomics, 2020, 51: 100723.
doi: 10.1016/j.margen.2019.100723 URL |
| [30] |
Zhu Huijuan, Wang Liangmin, Zhong Sheng, et al. A hybrid deep network framework for android malware detection[J]. IEEE Transactions on Knowledge and Data Engineering, 2022, 34(12): 5558-5570.
doi: 10.1109/TKDE.2021.3067658 URL |
| [31] | Saxe J, Berlin K. Deep neural network based malware detection using two dimensional binary program features[C]// 2015 10th International Conference on Malicious and Unwanted Software (MALWARE). New York: IEEE, 2015: 11-20. |
| [32] | Hansen S S, Larsen T M T, Stevanovic M, et al. An approach for detection and family classification of malware based on behavioral analysis[C]// 2016 International Conference on Computing, Networking and Communications (ICNC). New York: IEEE, 2016: 1-5. |
| [33] | Zhang Xiaohan, Zhang Yuan, Zhong Ming, et al. Enhancing state-of-the-art classifiers with API semantics to detect evolved android malware[C]// The 2020 ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2020: 757-770. |
| [34] | Rosenberg I, Shabtai A, Rokach L, et al. Generic black-box end-to-end attack against state of the art API call based malware classifiers[C]// International Symposium on Research in Attacks, Intrusions, and Defenses. Heidelberg: Springer, 2018: 490-510. |
| [35] | Salehi Z, Ghiasi M, Sami A. A miner for malware detection based on API function calls and their arguments[C]// The 16th CSI International Symposium on Artificial Intelligence and Signal Processing (AISP 2012). New York: IEEE, 2012: 563-568. |
| [36] |
Salehi Z, Sami A, Ghiasi M. MAAR: robust features to detect malicious activity based on API calls, their arguments and return values[J]. Engineering Applications of Artificial Intelligence, 2017, 59: 93-102.
doi: 10.1016/j.engappai.2016.12.016 URL |
| [1] | Sun Haoran, Chen Jie, Liu Jun. Multi-path feature enhanced deep learning method for rectangule attack and defense [J]. Netinfo Security, 2026, 26(7): 1115-1127. |
| [2] | LI Hailong, ZHANG Yunhao, SHEN Xieyang, XING Yuhang, CUI Zhian. A Survey of Machine Learning-Based Malware Detection Methods [J]. Netinfo Security, 2026, 26(4): 521-541. |
| [3] | XU Yanwei, TU Min, ZHANG Liang. A Review on the Authenticity Verification of Deepfake Speech [J]. Netinfo Security, 2026, 26(3): 367-377. |
| [4] | QIN Zhenkai, LUO Qining, NONG Xunyi, YU Xiaochuan, CAO Xiaochun. Multi-Level Speech Emotion Recognition Model Integrating Gender and Emotional Intensity Cue Features [J]. Netinfo Security, 2026, 26(3): 420-431. |
| [5] | XU Ruzhi, WU Xiaoxin, LYU Changran. Research on Transformer-Based Super-Resolution Network Adversarial Sample Defense Method [J]. Netinfo Security, 2025, 25(9): 1367-1376. |
| [6] | CHEN Yonghao, CAI Manchun, ZHANG Yiwen, PENG Shufan, YAO Lifeng, ZHU Yi. A Multi-Scale and Multi-Level Feature Fusion Approach for Deepfake Face Detection [J]. Netinfo Security, 2025, 25(9): 1456-1464. |
| [7] | WANG Xinmeng, CHEN Junbao, YANG Yitao, LI Wenjin, GU Dujuan. Bayesian Optimized DAE-MLP Malicious Traffic Identification Model [J]. Netinfo Security, 2025, 25(9): 1465-1472. |
| [8] | JIN Zhigang, LI Zimeng, CHEN Xuyang, LIU Zepei. Review of Network Intrusion Detection System for Unbalanced Data [J]. Netinfo Security, 2025, 25(8): 1240-1253. |
| [9] | WANG Gang, GAO Yunpeng, YANG Songru, SUN Litao, LIU Naiwei. A Survey on Deep Learning-Based Encrypted Malicious Traffic Detection Methods [J]. Netinfo Security, 2025, 25(8): 1276-1301. |
| [10] | WEI Songjie, WU Qinqin, YUAN Junyi. Dynamic Detection of Ransomware Based on Enhanced API Sequences with Running Parameters [J]. Netinfo Security, 2025, 25(5): 713-721. |
| [11] | ZHANG Xinglan, TAO Kejin. Universal Perturbations Generation Method Based on High-Level Features and Important Channels [J]. Netinfo Security, 2025, 25(5): 767-777. |
| [12] | JIN Zengwang, JIANG Lingyang, DING Junyi, ZHANG Huixiang, ZHAO Bo, FANG Pengfei. A Review of Research on Industrial Control System Security [J]. Netinfo Security, 2025, 25(3): 341-363. |
| [13] | CHEN Hongsong, LIU Xinrui, TAO Zimei, WANG Zhiheng. A Survey of Anomaly Detection Model for Time Series Data Based on Deep Learning [J]. Netinfo Security, 2025, 25(3): 364-391. |
| [14] | LI Hailong, CUI Zhian, SHEN Xieyang. Overview of Anomaly Analysis and Detection Methods for Network Traffic [J]. Netinfo Security, 2025, 25(2): 194-214. |
| [15] | WU Haoying, CHEN Jie, LIU Jun. Improved Neural Network Differential Distinguisher of Simon32/64 and Simeck32/64 [J]. Netinfo Security, 2025, 25(2): 249-259. |
| Viewed | ||||||
|
Full text |
|
|||||
|
Abstract |
|
|||||