信息网络安全 ›› 2026, Vol. 26 ›› Issue (8): 1194-1208.doi: 10.3969/j.issn.1671-1122.2026.08.003
可信执行环境在隐私计算中的研究现状、关键问题与发展方向综述
史俊1,2,3, 王浩1, 李增鹏1,4, 顾益宇5( ), 马惠铃6
- 1
山东大学网络空间安全学院 青岛 266237
2山东大学国家卓越工程师学院 济南 250102
3麒麟软件有限公司 天津 300459
4密码与数字经济安全全国重点实验室 青岛 266237
5北京科技大学计算机与通信工程学院 北京 100083
6贵州省信息中心 贵阳 550001
-
收稿日期:2026-02-27出版日期:2026-08-10发布日期:2026-09-23 -
通讯作者:顾益宇 E-mail:guyy0808@163.com -
作者简介:史俊(1986—),男,上海,工程师,博士研究生,主要研究方向为可信计算、远程证明|王浩(2002—),男,陕西,硕士研究生,主要研究方向为远程证明、可信执行环境|李增鹏(1989—),男,山东,副教授,博士,CCF会员,主要研究方向为网络数据安全、密码协议、安全多方计算|顾益宇(1986—),男,浙江,博士研究生,主要研究方向为网络认证|马惠铃(1987—),女,贵州,高级工程师,硕士,主要研究方向为数据处理、网络工程 -
基金资助:国家自然科学基金(62472255);国家自然科学基金(62302271);山东省自然科学基金(ZR2026QB26);山东省自然科学基金(ZR2023MF045);山东省自然科学基金(ZR2023QF088);山东省高等学校青年创新科技支持计划(2024KJH179)
Survey on the research status, key issues, and development directions of trusted execution environment in privacy computing
Shi Jun1,2,3, Wang Hao1, Li Zengpeng1,4, Gu Yiyu5(), Ma Huiling6
- 1
School of Cyber Science and Technology ,Shandong University Qingdao 266237, China
2National Graduate School for Elite Engineers ,Shandong University Jinan 250102, China
3KylinSoft Co. ,Ltd. Tianjin 300459, China
4State Key Laboratory of Cryptography and Digital Economy Security Qingdao 266237, China
5School of Computer and Communication Engineering ,University of Science and Technology Beijing Beijing 100083, China
6Guizhou Provincial Information Center Guiyang 550001, China
-
Received:2026-02-27Online:2026-08-10Published:2026-09-23 -
Contact:Gu Yiyu E-mail:guyy0808@163.com

摘要:
随着隐私计算技术的快速发展,基于硬件安全隔离的可信执行环境已成为保护数据隐私安全的关键技术。当前,可信执行环境技术体系涵盖Intel SGX、Intel TDX、AMD SEV、ARM TrustZone、RISC-V Keystone等各类架构,并扩展至GPU/FPGA等异构计算领域。这些架构在安全性提升、性能优化和生态系统建设方面取得重大进展,广泛应用于云计算平台、移动设备和边缘计算场景。然而,可信执行环境技术在实际工程部署中仍面临诸多挑战,尤其在安全性、跨平台兼容性和标准化统一等方面。文章对当前可信执行环境技术的前沿研究成果进行系统梳理,并总结其在隐私计算场景下面临的五大核心问题。在此基础上,文章提出未来研究的关键方向,旨在为可信执行环境技术的创新与应用提供理论支持和实践指导。
中图分类号:
引用本文
史俊, 王浩, 李增鹏, 顾益宇, 马惠铃. 可信执行环境在隐私计算中的研究现状、关键问题与发展方向综述[J]. 信息网络安全, 2026, 26(8): 1194-1208.
Shi Jun, Wang Hao, Li Zengpeng, Gu Yiyu, Ma Huiling. Survey on the research status, key issues, and development directions of trusted execution environment in privacy computing[J]. Netinfo Security, 2026, 26(8): 1194-1208.
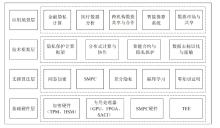
图1
隐私计算体系架构
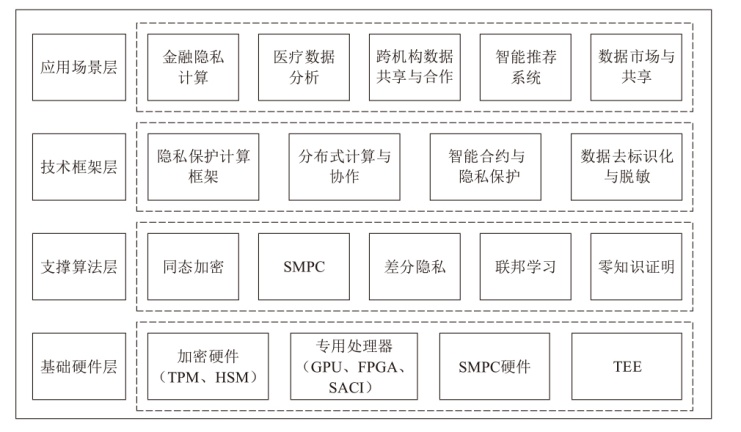
表1
TEE与其他隐私计算技术对比
| 技术 | 功能描述 | 安全特性 | 适用场景 | 性能代价 |
|---|---|---|---|---|
| TEE | 硬件级隔离和 安全执行环境 | 高安全性,远程证明和加密保护 | 金融、云计算、AI计算 | 低 |
| 同态加密[ | 加密数据计算,数据隐私保护 | 强隐私保护,加密 计算,计算性能差 | 数据共享、 计算分析 | 高 |
| SMPC[ | 多方共同计算,数据不泄露 | 高隐私性,涉及多方数据 | 多方协作计算 | 高 |
| 差分隐私[ | 噪声保护数据 隐私,数据不泄露 | 隐私保护,依赖算法的噪声强度与准确性 | 数据发布、 报告生成 | 中 |
| 零知识 证明[ | 无须泄露信息 即可证明声明的 正确性 | 高隐私性,防止计算过程中信息泄露 | 高级身份验证、合规验证 | 中 |
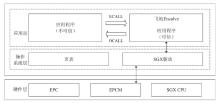
图2
Intel SGX架构
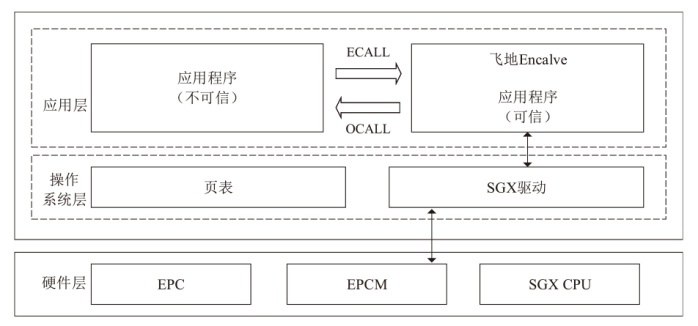
图3
AMD SEV架构
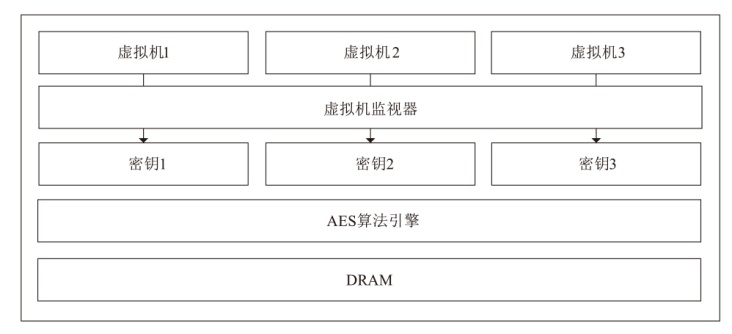
图4
ARM TrustZone架构
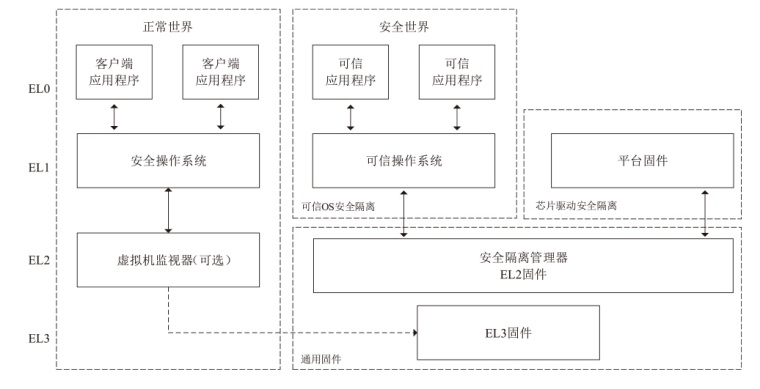
图5
RISC-V Keystone架构
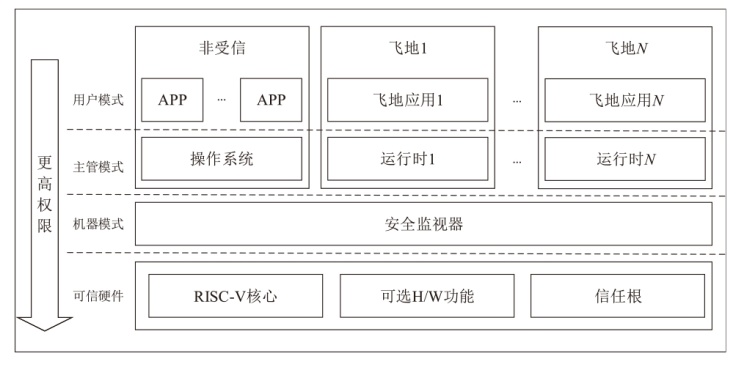
表2
主流TEE架构在安全机制方面的对比
| 主流TEE 架构 | 隔离机制 | 内存保护 | 侧信道攻击防护 | 远程证明 | 密钥管理 |
|---|---|---|---|---|---|
| Intel SGX[ | 用户态 飞地隔离 | AES+ Merkle树 | 弱,软件 辅助防护 | Intel统一认证 | CPU内置密钥 |
| Intel TDX[ | 虚拟机 隔离 | AES内存 加密 | 中,硬件 辅助防护 | Intel统一认证 | CPU动态管理 |
| AMD SEV[ | 虚拟机 隔离 | AES内存 加密 | 弱,软件 策略辅助 防护 | AMD统一认证 | PSP集中 管理 |
| ARM TrustZone[ | 安全世界隔离 | 默认无内存 加密 | 弱,额外策略辅助防护 | 缺乏统一标准 | 根密钥+TEE软件 |
| RISC-V Keystone[ | PMP隔离 | 可选AES 加密 | 弱,实验 阶段防护 | 开放自定义实现 | 设备密钥+监控器 |
| GPU/FPGA TEE[ | 异构资源隔离 | 显存/逻辑 资源加密 | 弱,定制 隔离措施 | 厂商初步阶段 | 厂商密钥 体系 |
表3
主流TEE架构在性能开销方面的对比
| 主流TEE架构 | 性能损耗 | 内存扩展能力 | 部署复杂性 |
|---|---|---|---|
| Intel SGX[ | 高 | 低 | 高 |
| Intel TDX[ | 中低 | 高 | 中 |
| AMD SEV[ | 中低 | 高 | 低 |
| ARM TrustZone[ | 较低 | 低 | 较高 |
| RISC-V Keystone[ | 低 | 中 | 中高 |
| GPU/FPGA TEE[ | 中 | 中(硬件规模) | 中(环境要求) |
表4
主流TEE架构在生态成熟度方面的对比
| 主流TEE架构 | 工具链成熟度 | 商业生态 |
|---|---|---|
| Intel SGX[ | 成熟,但开发难度大 | 成熟 |
| Intel TDX[ | 快速发展 | 快速发展 |
| AMD SEV[ | 成熟 | 广泛部署 |
| ARM TrustZone[ | 成熟,碎片化严重 | 嵌入式生态成熟 |
| RISC-V Keystone[ | 初期研究导向 | 边缘计算研究导向 |
| GPU/FPGA TEE[ | 发展阶段 | 新兴AI计算领域 |
表5
主流TEE架构在典型应用场景方面的对比
| 主流TEE架构 | 典型应用场景 |
|---|---|
| Intel SGX[ | 云端小规模应用 |
| Intel TDX[ | 云端整体迁移 |
| AMD SEV[ | 企业机密计算 |
| ARM TrustZone[ | 移动与嵌入式安全 |
| RISC-V Keystone[ | 边缘研究型应用 |
| GPU/FPGA TEE[ | AI机密高性能计算 |
表6
主流TEE在AI应用方面的对比
| 主流TEE架构 | AI场景适应性 | AI应用场景 |
|---|---|---|
| Intel SGX[ | 中 | AI模型的安全推理 |
| Intel TDX[ | 高 | 多租户AI应用 |
| AMD SEV[ | 高 | 多租户AI应用 |
| ARM TrustZone[ | 中 | 轻量级AI模型推理 |
| RISC-V Keystone[ | 中 | 可运行AI模型,但生态系统尚在发展中 |
| GPU/FPGA TEE[ | 非常高 | 大规模AI模型的安全推理 |
| [1] | Liu Bo, Ding Ming, Shaham S, et al. When machine learning meets privacy: a survey and outlook[J]. ACM Computing Surveys (CSUR), 2021, 54(2): 1-36. |
| [2] | Al-Rubaie M, Chang J M. Privacy-preserving machine learning: threats and solutions[J]. IEEE Security & Privacy, 2019, 17(2): 49-58. |
| [3] | Costan V, Devadas S. Intel SGX explained[EB/OL]. (2016-01-31)[2026-02-09]. https://eprint.iacr.org/2016/086.pdf. |
| [4] | Jang I, Tang A, Kim T, et al. Heterogeneous isolated execution for commodity GPUs[C]// The Twenty-Fourth International Conference on Architectural Support for Programming Languages and Operating Systems. New York: ACM, 2019: 455-468. |
| [5] | Tanuwidjaja H C, Choi R, Baek S, et al. Privacy-preserving deep learning on machine learning as a service-a comprehensive survey[J]. IEEE Access, 2020(8): 167425-167447. |
| [6] | GPD_SPE_009 TEE system architecture v1.3[S]. |
| [7] | Mckeen F, Alexandrovich I, Berenzon A, et al. Innovative instructions and software model for isolated execution[C]// The 2nd International Workshop on Hardware and Architectural Support for Security and Privacy. New York: ACM, 2013: 1-8. |
| [8] | Intel Corporation. Intel TDX module 1.0 specification: 344425-005US[R]. 2023: 19-46. |
| [9] | AMD. AMD memory encryption[EB/OL]. (2025-09-17)[2026-02-09]. https://cn.bing.com/search?q=AMD%20memory%20encryption&qs=n&form=QBRE&sp=-1&lq=0&pq=amd%20memory%20encryption&sc=11-21&sk=&cvid=DD77FEC37A6D4BABB4F86973ABA8825C. |
| [10] | ARM Limited. ARM security technology: building a secure system using TrustZone technology[EB/OL]. (2009-04-26)[2026-02-09]. https://support.arm.com/documentation/PRD29-GENC-009492/c/. |
| [11] | Lee D, Kohlbrenner D, Shinde S, et al. Keystone: an open framework for architecting trusted execution environments[C]// The Fifteenth European Conference on Computer Systems. New York: ACM, 2020: 1-16. |
| [12] | Volos S, Vaswani K, Bruno R. Graviton: trusted execution environments on GPUs[C]// The 13th USENIX Symposium on Operating Systems Design and Implementation (OSDI 18). Berkeley: USENIX, 2018: 681-696. |
| [13] | Acar A, Aksu H, Uluagac A S, et al. A survey on homomorphic encryption schemes: theory and implementation[J]. ACM Computing Surveys (CSUR), 2018, 51(4): 1-35. |
| [14] | Lindell Y. Secure multiparty computation[J]. Communications of the ACM, 2021, 64(1): 86-96. |
| [15] | Dwork C, Roth A. The algorithmic foundations of differential privacy[J]. Foundations and Trends® in Theoretical Computer Science, 2014, 9(3): 211-277. |
| [16] | Goldwasser S, Micali S, Rackoff C. The knowledge complexity of interactive proof-systems[C]// The Seventeenth Annual ACM Symposium on Theory of Computing. New York: ACM, 2019: 291-304. |
| [17] | Sabt M, Achemlal M, Bouabdallah A. Trusted execution environment: what it is, and what it is not[C]// 2015 IEEE Trustcom/BigDataSE/ISPA. New York: IEEE, 2015: 57-64. |
| [18] | GPD_SPE_021 TEE protection profile v1.3[S]. |
| [19] | Sinha R, Costa M, Lal A, et al. A design and verification methodology for secure isolated regions[J]. ACM SIGPLAN Notices, 2016, 51(6): 665-681. |
| [20] | Fei Shufan, Yan Zheng, Ding Wenxiu, et al. Security vulnerabilities of SGX and countermeasures: a survey[J]. ACM Computing Surveys (CSUR), 2021, 54(6): 1-36. |
| [21] | Sinha R, Rajamani S, Seshia S, et al. Moat: verifying confidentiality of enclave programs[C]// The 22nd ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2015: 1169-1184. |
| [22] | Subramanyan P, Sinha R, Lebedev I, et al. A formal foundation for secure remote execution of enclaves[C]// The 2017 ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2017: 2435-2450. |
| [23] | Baumann A, Peinado M, Hunt G. Shielding applications from an untrusted cloud with haven[J]. ACM Transactions on Computer Systems (TOCS), 2015, 33(3): 1-26. |
| [24] | Costan V, Lebedev I, Devadas S. Sanctum: minimal hardware extensions for strong software isolation[C]// The 25th USENIX Security Symposium (USENIX Security’ 16). Berkeley: USENIX, 2016: 857-874. |
| [25] | Strackx R, Piessens F. Ariadne: a minimal approach to state continuity[C]// The 25th USENIX Security Symposium (USENIX Security’ 16). Berkeley: USENIX, 2016: 875-892. |
| [26] | Parno B, Lorch J R, Douceur J R, et al. Memoir: practical state continuity for protected modules[C]// 2011 IEEE Symposium on Security and Privacy. New York: IEEE, 2011: 379-394. |
| [27] | Matetic S, Ahmed M, Kostiainen K, et al. ROTE: rollback protection for trusted execution[C]// The 26th USENIX Security Symposium (USENIX Security’ 17). Berkeley: USENIX, 2017: 1289-1306. |
| [28] | Angel S, Basu A, Cui Weidong, et al. Nimble: rollback protection for confidential cloud services[C]// The 17th USENIX Symposium on Operating Systems Design and Implementation (OSDI 23). Berkeley: USENIX, 2023: 193-208. |
| [29] | Coker G, Guttman J, Loscocco P, et al. Principles of remote attestation[J]. International Journal of Information Security, 2011, 10(2): 63-81. |
| [30] | Sailer R, Zhang Xiaolan, Jaeger T, et al. Design and implementation of a TCG-based integrity measurement architecture[C]// USENIX Security Symposium. Berkeley: USENIX, 2004: 223-238. |
| [31] | GP_REQ_025 Root of trust definitions and requirements v1.1.1[S]. |
| [32] | Chen Guoxing, Zhang Yinqian, Lai T H. Opera: open remote attestation for intel’s secure enclaves[C]// The 2019 ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2019: 2317-2331. |
| [33] | Hu Jilin, Zhao Yongwang, Pan Shuangquan, et al. Tacco: a framework for ensuring the security of real-world TEEs via formal verification[J]. IEEE Transactions on Dependable and Secure Computing, 2025, 22(6): 6983-6997. |
| [34] | Gueron S. A memory encryption engine suitable for general purpose processors[EB/OL]. (2016-02-25)[2026-02-09]. https://eprint.iacr.org/2016/204. |
| [35] | Sardar M U, Faqeh R, Fetzer C. Formal foundations for intel SGX data center attestation primitives[C]// International Conference on Formal Engineering Methods. Heidelberg: Springer, 2020: 268-283. |
| [36] | Sinha R, Rajamani S, Seshia S A. A compiler and verifier for page access oblivious computation[C]//2017 11th Joint Meeting on Foundations of Software Engineering. New York: ACM, 2017: 649-660. |
| [37] | Brandenburger M, Cachin C, Lorenz M, et al. Rollback and forking detection for trusted execution environments using lightweight collective memory[C]// 2017 47th Annual IEEE/IFIP International Conference on Dependable Systems and Networks (DSN). New York: IEEE, 2017: 157-168. |
| [38] | Ferraiuolo A, Baumann A, Hawblitzel C, et al. Komodo: using verification to disentangle secure-enclave hardware from software[C]// The 26th Symposium on Operating Systems Principles. New York: ACM, 2017: 287-305. |
| [39] | Noorman J, Agten P, Daniels W, et al. Sancus: low-cost trustworthy extensible networked devices with a zero-software trusted computing base[C]// The 22nd USENIX Security Symposium (USENIX Security’ 13). Berkeley: USENIX, 2013: 479-498. |
| [40] | Schuster F, Costa M, Fournet C, et al. VC3: trustworthy data analytics in the cloud using SGX[C]// 2015 IEEE Symposium on Security and Privacy. New York: IEEE, 2015: 38-54. |
| [41] | Gueron S. Memory encryption for general-purpose processors[J]. IEEE Security & Privacy, 2016, 14(6): 54-62. |
| [42] | Datta A, Franklin J, Garg D, et al. A logic of secure systems and its application to trusted computing[C]// 2009 30th IEEE Symposium on Security and Privacy. New York: IEEE, 2009: 221-236. |
| [43] | Lind J, Priebe C, Muthukumaran D, et al. Glamdring: automatic application partitioning for intel SGX[C]// 2017 USENIX Annual Technical Conference (USENIX ATC’ 17). Berkeley: USENIX, 2017: 285-298. |
| [44] | Van B J, Minkin M, Weisse O, et al. Foreshadow: extracting the keys to the intel SGX kingdom with transient out-of-order execution[C]// The 27th USENIX Security Symposium (USENIX Security’ 18). Berkeley: USENIX, 2018: 991-1008. |
| [45] | ARM Limited. TrustZone for cortex-a product support[EB/OL]. (2015-11-10)[2026-02-09]. https://developer.arm.com/dev2/compute-ip/trustzone-for-cortex-a. |
| [46] | Moghimi A, Irazoqui G, Eisenbarth T. Cachezoom: how SGX amplifies the power of cache attacks[C]// International Conference on Cryptographic Hardware and Embedded Systems. Heidelberg: Springer, 2017: 69-90. |
| [47] | Borrello P, Kogler A, Schwarzl M, et al. ÆPIC leak: architecturally leaking uninitialized data from the microarchitecture[C]// The 31st USENIX Security Symposium (USENIX Security’ 22). Berkeley: USENIX, 2022: 3917-3934. |
| [48] | Shih M W, Lee S, Kim T, et al. T-SGX: eradicating controlled-channel attacks against enclave programs[C]//NDSS Symposium 2017. Reston: Internet Society, 2017: 16-43. |
| [49] | Oleksenko O, Trach B, Krahn R, et al. Varys: protecting SGX enclaves from practical side-channel attacks[C]// 2018 USENIX Annual Technical Conference (USENIX ATC’ 18). Berkeley: USENIX, 2018: 227-240. |
| [50] | Seo J, Lee B, Kim S M, et al. SGX-shield: enabling address space layout randomization for SGX programs[C]//NDSS Symposium 2017. Reston: Internet Society, 2017: 1-15. |
| [51] | Dessouky G, Frassetto T, Sadeghi A R. HybCache: hybrid side-channel-resilient caches for trusted execution environments[C]// The 29th USENIX Security Symposium (USENIX Security’ 20). Berkeley: USENIX, 2020: 451-468. |
| [52] | Van S S, Seto A, Yurek T, et al. SoK:SGX. fail: how stuff gets eXposed[C]// 2024 IEEE Symposium on Security and Privacy (SP). New York: IEEE, 2024: 4143-4162. |
| [53] | Scarlata V, Johnson S, Beaney J, et al. Supporting third party attestation for intel SGX with intel data center attestation primitives[EB/OL]. (2019-04-19)[2026-02-09]. https://www.intel.com/content/www/us/en/content-details/671314/supporting-third-party-attestation-for-intel-software-guard-extensions-data-center-attestation-primitives.html. |
| [54] | GPD_SPE_010 TEE internal core API specification v1.1.2[S]. |
| [55] | Intel Corporation. Intel software guard extensions (intel SGX): key management reference application (KMRA) on intel Xeon scalable processors user guide[EB/OL]. (2023-10-30)[2026-02-09]. https://www.intel.com/content/www/us/en/content-details/635272/intel-software-guard-extensions-intel-sgx-key-management-reference-application-kmra-on-intel-xeon-scalable-processors.html. |
| [56] | FIPS 203 Module-lattice-based key-encapsulation mechanism standard[S]. |
| [57] | Version 0.22 Secure encrypted virtualization API[S]. |
| [58] | Pinto S, Santos N. Demystifying ARM TrustZone: a comprehensive survey[J]. ACM Computing Surveys (CSUR), 2019, 51(6): 1-36. |
| [59] | 中国信息通信研究院. 隐私计算应用研究报告(2023年)[EB/OL]. (2023-08-19)[2026-02-09]. https://dsj.guizhou.gov.cn/xwzx/gnyw/202308/t20230819_86427334.html. |
| [60] | 亿欧智库. 2022中国隐私计算产业研究报告[EB/OL]. (2022-06-02)[2026-02-09]. https://www.yunbaogao.cn/index/partFile/1/iresearch/2022-03/1_39729.pdf. |
| [61] | 北京金融科技产业联盟. 隐私计算技术金融应用研究报告[EB/OL]. (2022-03-10)[2026-02-09]. https://mp.weixin.qq.com/s/Tu8OX-gKXf2DUo3TLt9OZw. |
| [62] | Bahmani R, Barbosa M, Brasser F, et al. Secure multiparty computation from SGX[C]// International Conference on Financial Cryptography and Data Security. Heidelberg: Springer, 2017: 477-497. |
| [63] | Karanjai R, Collier R, Gao Zhimin, et al. Decentralized translator of trust: supporting heterogeneous TEE for critical infrastructure protection[C]// The 5th ACM International Symposium on Blockchain and Secure Critical Infrastructure. New York: ACM, 2023: 85-94. |
| [64] | Wang Huibo, Wang Pei, Ding Yu, et al. Towards memory safe enclave programming with rust-SGX[C]// 2019 ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2019: 2333-2350. |
| [65] | Xu Tianxing, Zhu Konglin, Andrzejak A, et al. Distributed learning in trusted execution environment: a case study of federated learning in SGX[C]// 2021 7th IEEE International Conference on Network Intelligence and Digital Content (IC-NIDC). New York: IEEE, 2021: 450-454. |
| [66] | Raisaro J L, Troncoso-Pastoriza J R, Misbach M, et al. MedCo: enabling secure and privacy-preserving exploration of distributed clinical and genomic data[J]. IEEE/ACM Transactions on Computational Biology and Bioinformatics, 2018, 16(4): 1328-1341. |
| [67] | Li Yi, Xu Wei. PrivPy: general and scalable privacy-preserving data mining[C]// The 25th ACM SIGKDD International Conference on Knowledge Discovery & Data Mining. New York: ACM, 2019: 1299-1307. |
| [68] | Messaoud A A, Mokhtar S B, Simonet-Boulogne A. TEE-based key-value stores: a survey[J]. The VLDB Journal, 2025, 34(1): 1-10. |
| [69] | Zheng Wenting, Dave A, Beekman J G, et al. Opaque: an oblivious and encrypted distributed analytics platform[C]// The 14th USENIX Symposium on Networked Systems Design and Implementation (NSDI 17). Berkeley: USENIX, 2017: 283-298. |
| [70] | Lee T, Lin Zhiqi, Pushp S, et al. Occlumency: privacy-preserving remote deep-learning inference using SGX[C]// The 25th Annual International Conference on Mobile Computing and Networking. New York: ACM, 2019: 1-17. |
| [71] | Ohrimenko O, Schuster F, Fournet C, et al. Oblivious multi-party machine learning on trusted processors[C]// The 25th USENIX Security Symposium (USENIX Security’ 16). Berkeley: USENIX, 2016: 619-636. |
| [72] | Tramer F, Boneh D. Slalom: fast, verifiable and private execution of neural networks in trusted hardware[EB/OL]. (2019-02-27)[2026-02-09]. https://arxiv.org/abs/1806.03287. |
| [73] | Fan Shulin, Hua Zhichao, Xia Yubin, et al. XpuTEE: a high-performance and practical heterogeneous trusted execution environment for GPUs[J]. ACM Transactions on Computer Systems, 2025, 43(2): 1-27. |
| [74] | Kato F, Cao Yang, Yoshikawa M. Olive: oblivious federated learning on trusted execution environment against the risk of sparsification[J]. Proceedings of the VLDB Endowment, 2023, 16(10): 2404-2417. |
| [75] | Liu Yang, Fan Tao, Chen Tianjian, et al. FATE: an industrial grade platform for collaborative learning with data protection[J]. Journal of Machine Learning Research, 2021, 22(1): 1-6. |
| [76] | Mo F, Shamsabadi A S, Katevas K, et al. DarkneTZ: towards model privacy at the edge using trusted execution environments[C]// The 18th International Conference on Mobile Systems, Applications, and Services. New York: ACM, 2020: 161-174. |
| [77] | Cerdeira D, Santos N, Fonseca P, et al. SoK: understanding the prevailing security vulnerabilities in trustzone-assisted TEE systems[C]// 2020 IEEE Symposium on Security and Privacy (SP). New York: IEEE, 2020: 1416-1432. |
| [78] | Apple Incorporation. The secure enclave[EB/OL]. (2024-12-19)[2026-02-09]. https://support.apple.com/guide/security/sec59b0b31ff/web. |
| [79] | Samsung Electronics. Knox platform for enterprise[EB/OL]. (2023-12-22)[2026-02-09]. https://docs.samsungknox.com/admin/knox-platform-for-enterprise/. |
| [80] | Munoz A, Rios R, Roman R, et al. A survey on the (in) security of trusted execution environments[EB/OL]. (2023-06-01)[2026-02-09]. https://www.sciencedirect.com/science/article/pii/S0167404823000901. |
| [81] | Boyens J, Smith A, Bartol N, et al. Cybersecurity supply chain risk management practices for systems and organizations[EB/OL]. (2022-05-05)[2026-02-09]. https://doi.org/10.6028/NIST.SP.800-161r1. |
| [82] | Fiolhais L, Sousa L. QR TPM in programmable low-power devices[EB/OL]. (2023-09-29)[2026-02-09]. https://arxiv.org/abs/2309.17414. |
| [83] | 中山市人民政府新闻办公室. “黑科技”齐亮相,2024中山市网络安全科普体验展持续至本月底[EB/OL]. (2024-09-10)[2026-02-09]. https://zsxwfbt.zs.gov.cn/news/index/view/cateid/1193/id/716496.html. |
| [84] | RFC 9334 Remote attestation procedures architecture[S]. |
| [85] | Zou Yu, Li Yiran, Wang Sheng, et al. Salus: a practical trusted execution environment for CPU-FPGA heterogeneous cloud platforms[C]// The 29th ACM International Conference on Architectural Support for Programming Languages and Operating Systems. New York: ACM, 2024: 252-266. |
| [86] | Hunt T, Jia Zhipeng, Miller V, et al. Telekine: secure computing with cloud GPUs[C]// The 17th USENIX Symposium on Networked Systems Design and Implementation (NSDI 20). Berkeley: USENIX, 2020: 817-833. |
| [87] | Yudha A W B, Meyer J, Yuan Shougang, et al. LITE: a low-cost practical inter-operable GPU TEE[C]// The 36th ACM International Conference on Supercomputing. New York: ACM, 2022: 1-13. |
| [88] | Zhu Jianping, Hou Rui, Wang Xiaofeng, et al. Enabling rack-scale confidential computing using heterogeneous trusted execution environment[C]// 2020 IEEE Symposium on Security and Privacy (SP). New York: IEEE, 2020: 1450-1465. |
| [89] | Han Husheng, Zheng Xinyao, Wen Yuanbo, et al. TensorTEE: unifying heterogeneous TEE granularity for efficient secure collaborative tensor computing[C]// The 29th ACM International Conference on Architectural Support for Programming Languages and Operating Systems. New York: ACM, 2024: 282-297. |
| [90] | Koga Y, Kourai K. SSdetector: secure and manageable host-based IDS with SGX and SMM[C]// 2023 IEEE 22nd International Conference on Trust, Security and Privacy in Computing and Communications (TrustCom). New York: IEEE, 2023: 539-548. |
| [91] | Arnautov S, Trach B, Gregor F, et al. SCONE: secure Linux containers with intel {SGX}[C]// The 12th USENIX Symposium on Operating Systems Design and Implementation (OSDI 16). Berkeley: USENIX, 2016: 689-703. |
| [92] | Shinde S, Le T D, Tople S, et al. Panoply: low-TCB Linux applications with SGX enclaves[C]//NDSS Symposium 2017. Reston: Internet Society, 2017: 56-77. |
| [93] | Tian Hongliang, Zhang Qiong, Yan Shoumeng, et al. Switchless calls made practical in intel SGX[C]// The 3rd Workshop on System Software for Trusted Execution. New York: ACM, 2018: 22-27. |
| [94] | Mckeen F, Alexandrovich I, Anati I, et al. Intel® software guard extensions (Intel® SGX) support for dynamic memory management inside an enclave[C]//The Hardware and Architectural Support for Security and Privacy 2016. New York: ACM, 2016: 1-9. |
| [95] | AMD. AMD SEV-SNP: strengthening VM isolation with integrity protection and more[EB/OL]. (2020-01-01)[2026-02-09]. https://docs.amd.com/v/u/en-US/SEV-SNP-strengthening-vm-isolation-with-integrity-protection-and-more. |
| [96] | Tsai C C, Porter D E, Vij M. Graphene-SGX: a practical library OS for unmodified applications on SGX[C]// 2017 USENIX Annual Technical Conference (USENIX ATC’ 17). Berkeley: USENIX, 2017: 645-658. |
| [97] | Open Enclave SDK. Open enclave SDK documentation[EB/OL]. (2023-04-29)[2026-02-09]. https://openenclave.io/. |
| [98] | Google LLC. Asylo: an open and flexible framework for enclave applications[EB/OL]. (2021-06-03)[2026-02-09]. https://github.com/google/asylo. |
| [99] | RFC 9711 The entity attestation token (EAT)[S]. |
| [100] | Confidential Computing Consortium. Confidential computing: hardware-based trusted execution for applications and data[EB/OL]. (2022-11-01)[2026-02-09]. https://confidentialcomputing.io/resources/white-papers-reports/. |
| [101] | Bennett C H, Brassard G. Quantum cryptography: public key distribution and coin tossing[J]. Theoretical Computer Science, 2014(560): 7-11. |
| [1] | 李子豪, 张锋巍. 基于可信执行环境的联邦学习平台[J]. 信息网络安全, 2026, 26(5): 788-808. |
| [2] | 崔津华, 董亮, 杨新. 大语言模型推理隐私保护技术综述[J]. 信息网络安全, 2026, 26(4): 503-520. |
| [3] | 林甜甜, 王奕天, 王小航, 竺婷, 任奎. CCASim:Arm机密计算架构性能仿真器研究[J]. 信息网络安全, 2026, 26(2): 189-210. |
| [4] | 赵佳, 王妍淳, 马洪亮, 李琪. 基于可信执行环境的层次角色基分级加密方案[J]. 信息网络安全, 2026, 26(2): 315-324. |
| [5] | 拾以娟, 周丹平, 范磊, 刘茵. 基于可信执行环境的安全多方计算协议[J]. 信息网络安全, 2025, 25(9): 1439-1446. |
| [6] | 郝萌, 李佳勇, 杨洪伟, 张伟哲. 异构CPU-GPU系统机密计算综述[J]. 信息网络安全, 2025, 25(11): 1658-1672. |
| [7] | 关志, 胡建斌, 李悦, 陈钟. 基于可信执行环境的区块链技术与应用综述[J]. 信息网络安全, 2025, 25(11): 1673-1690. |
| [8] | 薛开平, 张淳一, 柳枫, 王峰. 基于可信执行环境的加密数据库索引安全增强方案[J]. 信息网络安全, 2025, 25(11): 1718-1731. |
| [9] | 赵波, 吕佳敏, 王一琁. 一种面向容器生命周期的多维安全度量架构[J]. 信息网络安全, 2025, 25(11): 1745-1761. |
| [10] | 王亚杰, 陆锦标, 李宇航, 范青, 张子剑, 祝烈煌. 基于可信执行环境的联邦学习分层动态防护算法[J]. 信息网络安全, 2025, 25(11): 1762-1773. |
| [11] | 卢笛, 刘玉佳, 吕超越, 孙梦娜, 张清文, 杨力. 一种云原生TEE服务共享机制[J]. 信息网络安全, 2025, 25(11): 1774-1791. |
| [12] | 金娃, 秦宇, 刘菁润, 尚科彤, 贾梦涵, 林江南. 基于机密计算平台的TEE和TPM硬件可信信道构建方案[J]. 信息网络安全, 2025, 25(11): 1792-1810. |
| [13] | 胡宇义, 蔡炜, 陈竞凡, 刘莫寒, 王鹃, 何运. 面向机密容器的统一远程证明机制研究[J]. 信息网络安全, 2025, 25(11): 1811-1823. |
| [14] | 余发江, 王朝州. TrustZone半虚拟化与容器化实现机制[J]. 信息网络安全, 2025, 25(10): 1523-1536. |
| [15] | 问闻, 刘钦菊, 邝琳, 任雪静. 隐私保护体系下网络威胁情报共享的研究现状和方案设计[J]. 信息网络安全, 2024, 24(7): 1129-1137. |
| 阅读次数 | ||||||
|
全文 |
|
|||||
|
摘要 |
|
|||||