Netinfo Security ›› 2026, Vol. 26 ›› Issue (9): 1383-1390.doi: 10.3969/j.issn.1671-1122.2026.09.005
Previous Articles Next Articles
Research of malware detection method based on hardware performance counter
Zhang Jian1,2( ), Cai Hong1, Wang Botao2,3
- 1
College of Cryptology and Cyber Science ,Nankai University Tianjin 300350, China
2Tianjin Key Laboratory of Network and Data Security Technology Tianjin 300350, China
3College of Computer Science ,Nankai University Tianjin 300350, China
-
Received:2026-05-30Online:2026-09-10Published:2026-09-30 -
Contact:Zhang Jian E-mail:zhang.jian@nankai.edu.cn

CLC Number:
Cite this article
Zhang Jian, Cai Hong, Wang Botao. Research of malware detection method based on hardware performance counter[J]. Netinfo Security, 2026, 26(9): 1383-1390.
share this article
Add to citation manager EndNote|Ris|BibTeX
URL: http://netinfo-security.org/EN/10.3969/j.issn.1671-1122.2026.09.005
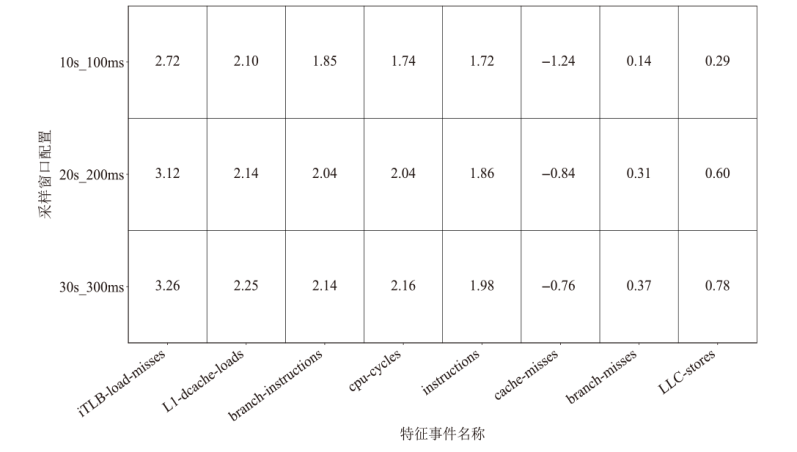
| 序号 | 事件名称 | 含义 |
|---|---|---|
| 1 | instructions | 执行指令总数 |
| 2 | cpu-cycles | CPU运行周期数 |
| 3 | cache-misses | 末级缓存未命中次数 |
| 4 | L1-dcache-loads | L1数据缓存加载次数 |
| 5 | branch-misses | 分支预测失败次数 |
| 6 | branch-instructions | 分支指令执行次数 |
| 7 | iTLB-load-misses | 指令TLB加载未命中次数 |
| 8 | LLC-stores | 末级缓存存储次数 |
| 数据集 | 样本总数/个 | 恶意样本数/个 | 正常样本数/个 |
|---|---|---|---|
| 训练集 | 711 | 361 | 350 |
| 验证集 | 152 | 77 | 75 |
| 测试集 | 153 | 78 | 75 |
| 合计 | 1016 | 516 | 500 |
| 采样窗口配置 | 模型 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|---|
| 10 s_100 ms | RF | 95.42% | 91.76% | 100% | 0.9571 |
| XGB | 94.12% | 89.66% | 100% | 0.9455 | |
| DT | 92.81% | 88.51% | 98.72% | 0.9333 | |
| SVM | 81.05% | 72.90% | 100% | 0.8432 | |
| 20 s_200 ms | RF | 94.77% | 92.68% | 97.44% | 0.9500 |
| XGB | 95.42% | 92.77% | 98.72% | 0.9565 | |
| DT | 94.77% | 91.67% | 98.72% | 0.9506 | |
| SVM | 82.35% | 74.29% | 100% | 0.8525 | |
| 30 s_300 ms | RF | 92.81% | 91.36% | 94.87% | 0.9308 |
| XGB | 94.77% | 94.87% | 94.87% | 0.9487 | |
| DT | 94.12% | 93.67% | 94.87% | 0.9427 | |
| SVM | 88.89% | 82.80% | 98.72% | 0.9006 |
| 采样配置 | 模型 | 准确率 | 精确率 | 召回率 | F1分数 |
|---|---|---|---|---|---|
| 10 s_100 ms | LSTM | 92.16% | 87.50% | 98.72% | 0.9277 |
| BiLSTM | 93.46% | 91.46% | 96.15% | 0.9375 | |
| BiLSTM_Attn | 91.50% | 86.52% | 98.72% | 0.9222 | |
| TCN | 92.81% | 87.64% | 100% | 0.9341 | |
| Transformer | 92.81% | 90.36% | 96.15% | 0.9317 | |
| 20 s_200 ms | LSTM | 92.81% | 87.64% | 100% | 0.9341 |
| BiLSTM | 93.46% | 88.64% | 100% | 0.9398 | |
| BiLSTM_Attn | 94.12% | 89.66% | 100% | 0.9455 | |
| TCN | 92.81% | 87.64% | 100% | 0.9341 | |
| Transformer | 94.77% | 93.75% | 96.15% | 0.9494 | |
| 30 s_300 ms | LSTM | 94.12% | 89.66% | 100% | 0.9455 |
| BiLSTM | 91.50% | 85.71% | 100% | 0.9231 | |
| BiLSTM_Attn | 94.77% | 92.68% | 97.44% | 0.9500 | |
| TCN | 93.46% | 88.64% | 100% | 0.9398 | |
| Transformer | 95.10% | 92.77% | 98.72% | 0.9530 |
| 方法 | 10 s_100 ms | 20 s_200 ms | 30 s_300 ms | 平均值 | ||||
|---|---|---|---|---|---|---|---|---|
| 准确率 | F1分数 | 准确率 | F1分数 | 准确率 | F1分数 | 准确率 | F1分数 | |
| 文献[ | 92.16% | 0.9125 | 92.81% | 0.9183 | 93.46% | 0.9210 | 92.81% | 0.9173 |
| 文献[ | 93.46% | 0.9289 | 94.12% | 0.9367 | 94.77% | 0.9412 | 94.12% | 0.9356 |
| 文献[ | 94.77% | 0.9458 | 94.77% | 0.9462 | 94.12% | 0.9437 | 94.55% | 0.9452 |
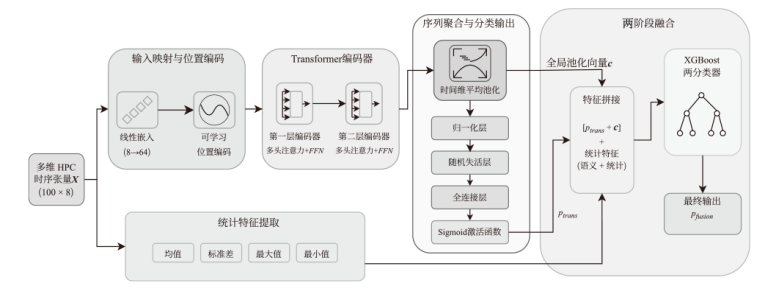
| 本文方法 | 95.98% | 0.9612 | 95.72% | 0.9581 | 95.37% | 0.9533 | 95.69% | 0.9575 |
| 采样窗口配置 | 完整模型 | 移除XGBoost | 移除Transformer |
|---|---|---|---|
| 10 s_100 ms | 0.9612 | 0.9280 (-0.0332) | 0.9400 (-0.0212) |
| 20 s_200 ms | 0.9581 | 0.9450 (-0.0131) | 0.9520 (-0.0061) |
| 30 s_300 ms | 0.9533 | 0.9500 (-0.0033) | 0.9440 (-0.0093) |
| [1] | Skoudis E, Zeltser L. Malware: fighting malicious code[M]. Upper Saddle River: Prentice Hall Professional, 2004. |
| [2] | Sikorski M, Honig A. Practical malware analysis: the hands-on guide to dissecting malicious software[M]. San Francisco: No Starch Press, 2012. |
| [3] | Chandran S, Syam S R, Sankaran S, et al. From static to AI-driven detection: a comprehensive review of obfuscated malware techniques[J]. IEEE Access, 2025(13): 74335-74358. |
| [4] | Malone C, Zahran M, Karri R. Are hardware performance counters a cost effective way for integrity checking of programs[C]// The 6th ACM Workshop on Scalable Trusted Computing. New York: ACM, 2011: 71-76. |
| [5] | Raff E, Barker J, Sylvester J, et al. Malware detection by eating a whole EXE[C]// The Workshops of the 32nd AAAI Conference on Artificial Intelligence. Menlo Park: AAAI, 2018: 268-276. |
| [6] | Jeong Y S, Woo J, Kang A R. Malware detection on byte streams of PDF files using convolutional neural networks[EB/OL]. (2019-04-03)[2026-03-13]. https://onlinelibrary.wiley.com/doi/epdf/10.1155/2019/8485365. |
| [7] | Ling Xiang, Wu Lingfei, Deng Wei, et al. MalGraph: hierarchical graph neural networks for robust windows malware detection[C]// IEEE INFOCOM 2022-IEEE Conference on Computer Communications. New York: IEEE, 2022: 1998-2007. |
| [8] | Kolosnjaji B, Zarras A, Webster G, et al. Deep learning for classification of malware system call sequences[C]// The 29th Australasian Joint Conference on Artificial Intelligence (AI 2016). Heidelberg: Springer, 2016: 137-149. |
| [9] |
Gibert D, Mateu C, Planes J, et al. Using convolutional neural networks for classification of malware represented as images[J]. Journal of Computer Virology and Hacking Techniques, 2019, 15(1): 15-28.
doi: 10.1007/s11416-018-0323-0 |
| [10] | Wong G W, Huang Yiting, Guo Yingren, et al. Attention-based API locating for malware techniques[J]. IEEE Transactions on Information Forensics and Security, 2024(19): 1199-1212. |
| [11] | Demme J, Maycock M, Schmitz J, et al. On the feasibility of online malware detection with performance counters[C]// The 40th Annual International Symposium on Computer Architecture (ISCA). New York: ACM, 2013: 559-570. |
| [12] | Tang A, Sethumadhavan S, Stolfo S J. Unsupervised anomaly-based malware detection using hardware features[C]// International Workshop on Recent Advances in Intrusion Detection (RAID 2014). Heidelberg: Springer, 2014: 109-129. |
| [13] | Ozsoy M, Donovick C, Gorelik I, et al. Malware-aware processors: a framework for efficient online malware detection[C]// 2015 IEEE 21st International Symposium on High Performance Computer Architecture (HPCA). New York: IEEE, 2015: 651-661. |
| [14] | 严飞, 彭慧容, 何凡, 等. HBROP: 基于硬件性能计数器的函数级ROP检测[J]. 武汉大学学报(理学版), 2017, 63(2): 109-116. |
| [15] | 邢凌凯, 张健. 基于HPC的虚拟化平台异常检测技术研究与实现[J]. 信息网络安全, 2023, 23(10): 64-69. |
| [16] |
Wang Xueyang, Karri R. Reusing hardware performance counters to detect and identify kernel control-flow modifying rootkits[J]. IEEE Transactions on Computer-Aided Design of Integrated Circuits and Systems, 2016, 35(3): 485-498.
doi: 10.1109/TCAD.2015.2474374 URL |
| [17] | Sayadi H, Makrani H M, Pudukotai D S M, et al. 2SMaRT: a two-stage machine learning-based approach for run-time specialized hardware-assisted malware detection[C]// 2019 Design, Automation & Test in Europe Conference & Exhibition (DATE). New York: IEEE, 2019: 728-733. |
| [18] |
Elnaggar R, Servadei L, Mathur S, et al. Accurate and robust malware detection: running XGBoost on runtime data from performance counters[J]. IEEE Transactions on Computer-Aided Design of Integrated Circuits and Systems, 2022, 41(7): 2066-2079.
doi: 10.1109/TCAD.2021.3102007 URL |
| [19] |
Kuruvila A P, Meng Xingyu, Kundu S, et al. Explainable machine learning for intrusion detection via hardware performance counters[J]. IEEE Transactions on Computer-Aided Design of Integrated Circuits and Systems, 2022, 41(11): 4952-4964.
doi: 10.1109/TCAD.2022.3149745 URL |
| [20] | He Zhangying, Miari T, Makrani H M, et al. When machine learning meets hardware cybersecurity: delving into accurate zero-day malware detection[C]// 2021 22nd International Symposium on Quality Electronic Design (ISQED). New York: IEEE, 2021: 85-90. |
| [21] | Zhou Boyou, Gupta A, Jahanshahi R, et al. Hardware performance counters can detect malware: myth or fact?[C]// The 2018 on Asia Conference on Computer and Communications Security. New York: ACM, 2018: 457-468. |
| [22] | Weaver V M. Self-monitoring overhead of the Linux perf_event performance counter interface[C]// 2015 IEEE International Symposium on Performance Analysis of Systems and Software (ISPASS). New York: IEEE, 2015: 102-111. |
| [1] | Huang Jiaxin, Liu Ruiyuan, Duan Rongcheng, Tian Ye, Sun Jianguo. Ethereum fraud detection method based on transaction sequences and graph structures [J]. Netinfo Security, 2026, 26(9): 1481-1492. |
| [2] | Zhang Hongtao, Wang Qingtao, Zhang Liancheng, Wang Jichang. Argus6: an IPv6 DDoS threat detection model [J]. Netinfo Security, 2026, 26(8): 1264-1276. |
| [3] | Kou Liang, Tu Guoxuan, Pan Xiaochen, Zhang Jilin. Enhancing malware detection via multi-view sensitivity mining and Sens-FiLM modulation [J]. Netinfo Security, 2026, 26(7): 1028-1043. |
| [4] | Zheng Tianming, Liu Shangdong, Li Haitian, Li Hua. Interactive convolution and Transformer based anomaly detection algorithm [J]. Netinfo Security, 2026, 26(7): 1077-1086. |
| [5] | LI Hailong, ZHANG Yunhao, SHEN Xieyang, XING Yuhang, CUI Zhian. A Survey of Machine Learning-Based Malware Detection Methods [J]. Netinfo Security, 2026, 26(4): 521-541. |
| [6] | CHEN Yuqi, QIAN Hanwei, XIA Lingling, WANG Qun. FEViT: A Frequency Domain Enhanced ViT for Deepfake Detection [J]. Netinfo Security, 2026, 26(3): 432-441. |
| [7] | ZHAO Wenyu, DANG Chenxi, DU Zhenhua, ZHANG Jian. Research and Implementation of Ransomware Detection Technology Based on Hardware Performance Counters [J]. Netinfo Security, 2025, 25(9): 1397-1406. |
| [8] | SUN Jianwen, ZHANG Bin, SI Nianwen, FAN Ying. Lightweight Malicious Traffic Detection Method Based on Knowledge Distillation [J]. Netinfo Security, 2025, 25(6): 859-871. |
| [9] | WEI Songjie, WU Qinqin, YUAN Junyi. Dynamic Detection of Ransomware Based on Enhanced API Sequences with Running Parameters [J]. Netinfo Security, 2025, 25(5): 713-721. |
| [10] | WEI Chaoren, XIA Wanxu, QU Gang, BAI Wanrong, YANG Liqun. Research on the Optimization Technology of Open Source Fuzzing Framework for Intelligent Systems [J]. Netinfo Security, 2025, 25(4): 587-597. |
| [11] | ZHANG Xinyou, GAO Zhichao, FENG Li, XING Huanlai. FFT-iTransformer-Based Cybersecurity Situation Awareness Feature Imputation and Prediction [J]. Netinfo Security, 2025, 25(2): 228-239. |
| [12] | LIU Qiang, WANG Jian, WANG Yanan, WANG Shan. A Dynamic Malware Detection Method Based on Ensemble Learning [J]. Netinfo Security, 2025, 25(1): 159-172. |
| [13] | XU Ruzhi, ZHANG Ning, LI Min, LI Zixuan. Research on a High Robust Detection Model for Malicious Software [J]. Netinfo Security, 2024, 24(8): 1184-1195. |
| [14] | LI Yixuan, JIA Peng, FAN Ximing, CHEN Chen. Control Flow Transformation Based Adversarial Example Generation for Attacking Malware Detection GNN Model [J]. Netinfo Security, 2024, 24(12): 1896-1910. |
| [15] | WANG Yu, LYU Liangshuang, XIA Chunhe. A Windows Malware Detection Method Based on Semantic Analysis [J]. Netinfo Security, 2023, 23(10): 58-63. |
| Viewed | ||||||
|
Full text |
|
|||||
|
Abstract |
|
|||||