信息网络安全 ›› 2026, Vol. 26 ›› Issue (8): 1308-1326.doi: 10.3969/j.issn.1671-1122.2026.08.011
抗隐式攻击的基于ASCON的轻量级工业物联网认证方案
刘哲凡1, 郭亚军1( ), 郭奕旻2, 赵素芬1
- 1
华中师范大学计算机学院 武汉 430079
2中南财经政法大学信息工程学院 武汉 430073
-
收稿日期:2026-02-02出版日期:2026-08-10发布日期:2026-09-23 -
通讯作者:郭亚军 E-mail:yj.guo@ccnu.edu.cn -
作者简介:刘哲凡(1997—),男,辽宁,硕士研究生,主要研究方向为信息安全|郭亚军(1965—),男,湖北,教授,博士,CCF高级会员,主要研究方向为信息安全|郭奕旻(1992—),女,湖北,副教授,博士,主要研究方向为信息安全|赵素芬(1981—),女,湖北,讲师,博士,主要研究方向为信息安全、社交网络、数据挖掘 -
基金资助:国家自然科学基金(62102453);湖北省自然科学基金(2025AFC108)
ASCON-based lightweight industrial IoT authentication scheme resistant to implicit attacks
Liu Zhefan1, Guo Yajun1(), Guo Yimin2, Zhao Sufen1
- 1
School of Computer Science ,Central China Normal University Wuhan 430079, China
2School of Information Engineering ,Zhongnan University of Economics and Law Wuhan, 430073, China
-
Received:2026-02-02Online:2026-08-10Published:2026-09-23 -
Contact:Guo Yajun E-mail:yj.guo@ccnu.edu.cn

摘要:
工业5.0以人机协同、绿色高效、韧性制造为核心特征,其底层工业物联网需满足高实时性、轻量化、分布式协作的核心需求,然而面临设备资源受限、人机交互链路易被攻击、集中式认证架构单点故障等安全问题,且现有协议难以适配工业5.0雾边云协同的计算架构和绿色低耗的设计要求,也无法有效抵御复杂场景下的隐式攻击。针对工业5.0的场景化需求与技术特性,文章提出一种定制化的轻量级认证协议,深度融合物理不可克隆函数(PUF)、NIST标准轻量级加密算法ASCON、联盟链及三因素身份验证技术,将雾节点的边缘计算能力、区块链的分布式可信特性、ASCON的低耗加解密优势与工业5.0人机协同场景深度结合,构建适配工业5.0雾边云架构的网络模型。基于DY和CK威胁模型定义攻击类型,结合最强隐式攻击模型验证安全属性,通过ROR模型形式化证明与非形式化分析,证实方案在多类隐式攻击下满足双向认证、匿名性、前向保密性等关键安全需求。经性能对比与场景实测验证,该方案在完备安全防护基础上,可满足工业5.0低算力开销、低通信时延、绿色低功耗的核心需求,为人机协同场景下的设备交互、远程控制提供高可靠的安全通信支持。
中图分类号:
引用本文
刘哲凡, 郭亚军, 郭奕旻, 赵素芬. 抗隐式攻击的基于ASCON的轻量级工业物联网认证方案[J]. 信息网络安全, 2026, 26(8): 1308-1326.
Liu Zhefan, Guo Yajun, Guo Yimin, Zhao Sufen. ASCON-based lightweight industrial IoT authentication scheme resistant to implicit attacks[J]. Netinfo Security, 2026, 26(8): 1308-1326.

图1
网络模型
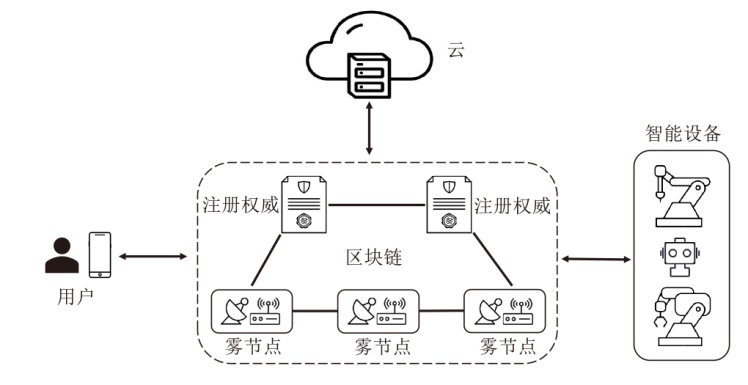
表1
单一攻击
| 条目 | 单一攻击 |
|---|---|
| SA1 | 敌手具有控制信道的能力,其中包括窃听、拦截、修改、重放和伪造消息的能力 |
| SA2 | 敌手可以获取特定于会话的临时秘密(如随机数) |
| SA3 | 敌手可以获取到长期秘密(如预共享的对称密钥和私钥) |
| SA4 | 敌手可以捕获用户设备,提取其中的信息 |
| SA5 | 敌手可以捕获物联网设备,提取其中的信息 |
| SA6 | 敌手可以获取注册阶段用户提交的信息 |
| SA7 | 敌手可以发起离线密码猜测攻击 |
表2
安全属性与隐式攻击
| 条目 | 安全属性 | 形式化 攻击标识 | 隐式攻击 |
|---|---|---|---|
| SP1 | 双向认证与密钥协商:参与实体能够相互认证身份,并生成用于用户和智能设备间安全通信的会话密钥 | Att1/Att2 | [SA1, SA2, SA6, SA7]or [SA1, SA3, SA6, SA7] |
| SP2 | 抗重放攻击:协议能够检测并拒绝被重播的 消息 | Att1/Att2 | [SA1, SA2, SA6, SA7]or [SA1, SA3, SA6, SA7] |
| SP3 | 抗中间人攻击:攻击者无法通过修改截获的消息,且让接收者相信攻击者是真实的发送者 | Att1/Att2 | [SA1, SA2, SA6, SA7]or [SA1, SA3, SA6, SA7] |
| SP4 | 抗冒充攻击:攻击者无法假冒任何一方,与合法的另一方进行通信 | Att3/Att4/Att5 | [SA1, SA2, SA4/SA5/SA6-2, SA7]or[SA1, SA3/SA4/SA5, SA7]or [SA1, SA3/SA6, SA7] |
| SP5 | 抗离线密码猜测攻击:敌手可以发起离线密码猜测攻击,但不能验证猜测的密码是否正确 | Att6 | [SA1, SA4, SA6, SA7] |
| SP6 | 会话密钥安全性:敌手无法计算出通信实体间建立的会话密钥 | Att3/Att4/Att5 | [SA1, SA2, SA4/SA5/SA6-2, SA7]or [SA1, SA3/SA4/SA5, SA7]or [SA1, SA3/SA6, SA7] |
| SP7 | 完美前向保密:即使敌手获取了会话密钥,也无法推断出先前建立的会话密钥 | Att7 | [SA1, SA3] |
| SP8 | 匿名性:攻击者无法获得用户的真实的身份且无法将两个信息关联至同一个实体 | Att1/Att2 | [SA1, SA2, SA6, SA7]or [SA1, SA3, SA6, SA7] |
| SP9 | 抗去同步化攻击:协议可有效防止攻击者通过干扰认证状态或会话同步,导致通信双方失去同步并中断正常通信的能力 | Att1/Att2 | [SA1, SA2, SA6, SA7]or [SA1, SA3, SA6, SA7] |
表3
符号及其定义
| 符号 | 定义 |
|---|---|
| Ui, FNu, SDj | 第i个用户,第u个雾节点和第j个智能设备 |
| MDi | 第i个用户的移动设备 |
| BIOi, PWi | 用户Ui的指纹和密码 |
| IDi, IDj | 用户Ui和智能设备SDj的身份 |
| TIDi, PIDi, PIDj | 用户Ui的临时身份,伪身份和智能设备SDj的伪身份 |
| X | RA之间的共享密钥 |
| Xi | Ui和FNu之间共享的长期秘密 |
| Xj | SDj和FNu之间共享的长期秘密 |
| Gen(·) | 模糊抽取器的生成函数 |
| Rep(·) | 模糊提取器的再现函数 |
| σi | Ui的生物特征密钥 |
| τi | Ui的公共再生参数 |
| ti,∆ti | 时间戳和最大传输延迟 |
| ai,bi, ni | 随机数 |
| RTi, RTj | Ui和SDj的注册时间戳 |
| SK | 会话密钥 |
| h(·) | 密码哈希函数 |
| ||,⊕ | 连接符和异或运算 |
| PUF(·) | 物理不可克隆函数 |
| C, R | PUF的输入挑战和输出响应 |
| CT | 通过ASCON计算出的密文 |
| PT | 通过ASCON计算出的明文 |
| MAC | 通过ASCON计算出的消息认证码 |
图2
用户注册过程
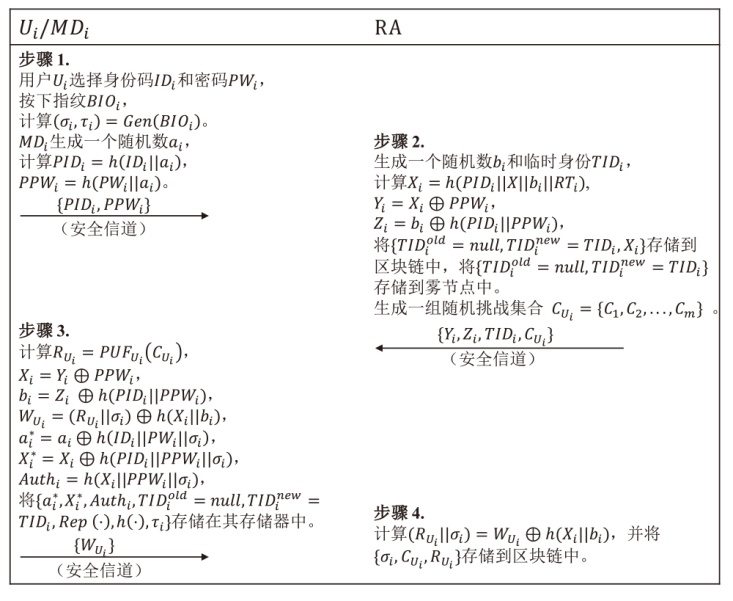
图3
智能设备注册过程
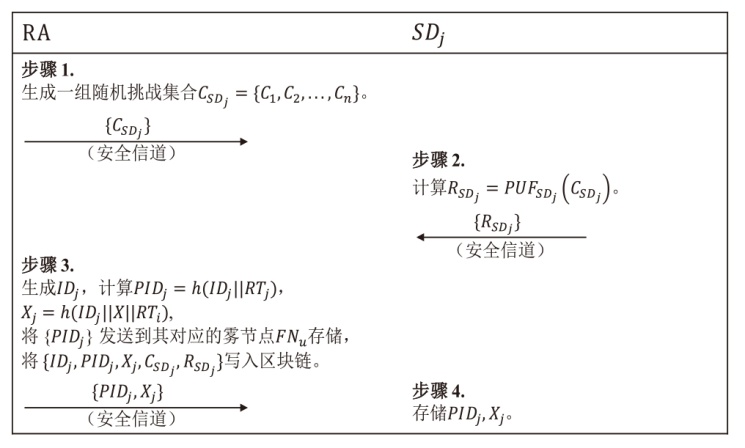
图4
认证与密钥协商过程
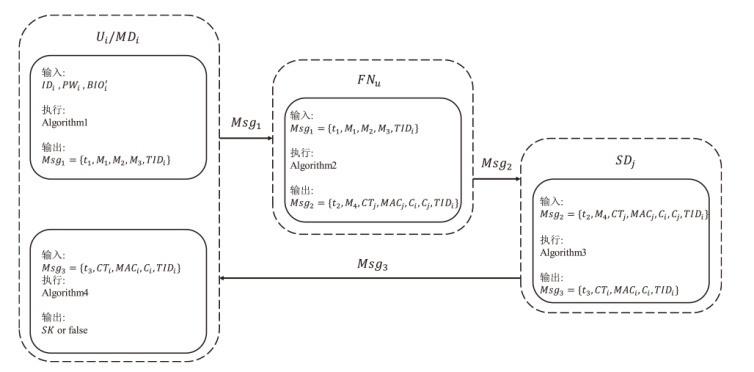
表4
敌手能够执行的查询
| 查询 | 具有的能力 |
|---|---|
| 敌手A拥有窃听实例之间交换的所有消息的能力 | |
| 当敌手A向实例发送一个消息时,该实例也会对敌手A发送响应消息 | |
| 敌手A可以获取到实例间的会话密钥 | |
| 当用户的移动设备被捕获时,敌手A可以提取出存储在移动设备中的信息 | |
| 当智能设备被捕获时,敌手A可以提取出储存在智能设备中的信息 | |
| 当雾节点被捕获时,敌手A可以获取到储存在雾节点中的信息 | |
| 在实验开始时投掷一个均匀的硬币b。当b=1时, | |
| 敌手A可发起 |
表5
安全属性对比
| 安全属性 | 文献[ 方案 | 文献[ 方案 | 文献[ 方案 | 文献[ 方案 | 本文方案 |
|---|---|---|---|---|---|
| SP1 | √ | √ | √ | √ | √ |
| SP2 | √ | √ | √ | √ | √ |
| SP3 | × | × | × | √ | √ |
| SP4 | × | × | × | √ | √ |
| SP5 | × | √ | 不适用 | √ | √ |
| SP6 | × | × | × | × | √ |
| SP7 | √ | √ | √ | √ | √ |
| SP8 | √ | √ | √ | × | √ |
| SP9 | √ | × | √ | √ | √ |
| SP10 | × | × | × | × | √ |
| SP11 | × | × | × | × | √ |
表6
通信代价对比
| 方案 | 总消息数/条 | 总通信开销/bit |
|---|---|---|
| 文献[ | 5 | 3200 |
| 文献[ | 3 | 2336 |
| 文献[ | 4 | 2528 |
| 文献[ | 3 | 2112 |
| 本文方案 | 3 | 3296 |
表7
密码原语近似执行时间
| 设备 | Ta/ms | Th/ms | Tem/ms | Tfe/ms | Tpuf/ms | Tsed/ms |
|---|---|---|---|---|---|---|
| Ui/SDj | 0.3700 | 0.3450 | 2.8500 | 2.8500 | 0.0040 | 0.3910 |
| FNu | 0.0351 | 0.0390 | 0.7800 | 0.7800 | 不适用 | 0.0200 |
表8
计算代价对比
| 方案 | MDi | FNu | SDj | 总开销/ms |
|---|---|---|---|---|
| 文献[ | 14Th | 14Th | 8Th | 8.1160 |
| 文献[ | 11Th+Tsed+Tfe | 6Th+Tsed | 6Th+2Tsed | 10.1420 |
| 文献[ | 8Th+Tem | 12Th+4Tem | 7Th+Tem+Tpuf | 14.6670 |
| 文献[ | 6Th+Tfe+2Tem+2Tpuf | 6Th+2Tem | 5Th+2Tem+2Tpuf | 16.8310 |
| 本文方案 | 9Th+Tfe+Ta+Tpuf | 5Th+2Ta | 3Th+Tpuf+2Ta | 8.1932 |
| [1] | Cuevas-lopez-de-baro C, Mira-solves I, Verdú-jover A. Assessment model for industry 5.0: a holistic approach to readiness and integration[J]. Journal of Industrial Information Integration, 2025, 46: 100855. |
| [2] | Golovianko M, Terziyan V, Branytskyi V, et al. Industry 4.0 vs. industry 5.0: co-existence, transition, or a hybrid[J]. Procedia Computer Science, 2023, 217: 102-113. |
| [3] | Barata J, Kayser I. Industry 5.0-past, present, and near future[J]. Procedia Computer Science, 2023, 219: 778-788. |
| [4] | Xu Xun, Lu Yuqian, Vogel-heuser B, et al. Industry 4.0 and industry 5.0—Inception, conception and perception[J]. Journal of Manufacturing Systems, 2021, 61: 530-535. |
| [5] | Barata J, Kayser I. How will the digital twin shape the future of industry 5.0?[J]. Technovation, 2024, 134: 103025. |
| [6] | Bongomin O, Mwape M C, Mpofu N S, et al. Digital twin technology advancing industry 4.0 and industry 5.0 across sectors[J]. Results in Engineering, 2025, 83(3): 3675-3712. |
| [7] | Chaudhuri A, Behera R K, Bala P K. Factors impacting cybersecurity transformation: an industry 5.0 perspective[J]. Computers & Security, 2025, 150: 104267. |
| [8] | Akundi A, Euresti D, Luna S, et al. State of industry 5.0—analysis and identification of current research trends[J]. Applied System Innovation, 2022, 5(1): 27. |
| [9] | Möller D P F, Vakilzadian H, Haas R E. From industry 4.0 towards industry 5.0[C]// 2022 IEEE International Conference on Electro Information Technology (eIT). New York: IEEE, 2022: 61-68. |
| [10] | Dehshiri S J H. An integrated decision-making framework for evaluating industry 5.0 and circular economy in supply chain management using Z-numbers[J]. Applied Soft Computing, 2025,181: 113504. |
| [11] | Guo Junlang, Leng Jiewu, Zhao J L, et al. Industrial metaverse towards industry 5.0: connotation, architecture, enablers, and challenges[J]. Journal of Manufacturing Systems, 2024, 76: 25-42. |
| [12] | Sverko M, Grbac T G, Mikuc M. Scada systems with focus on continuous manufacturing and steel industry: a survey on architectures, standards, challenges and industry 5.0[J]. IEEE Access, 2022, 10: 109395-109430. |
| [13] | Mulongo N Y. Industry 5.0 a novel technological concept[C]// 2024 International Conference on Smart Applications, Communications and Networking (SmartNets). New York: IEEE, 2024: 1-6. |
| [14] | Verma P, O’shea D, Newe T, et al. WebShield 5.0: harnessing AI and NLP to combat Web threats in industry 5.0[J]. Alexandria Engineering Journal, 2025, 127: 677-689. |
| [15] | Singh K A, Patra F, Ghosh T, et al. Advancing food systems with industry 5.0: a systematic review of smart technologies, sustainability, and resource optimization[J]. Sustainable Futures, 2025, 9: 100694. |
| [16] | Matha R, Mukherjee S, Panigrahi R R, et al. A bibliometric analysis of industry 5.0 and healthcare supply chain research: emerging opportunities and future challenges[J]. Supply Chain Analytics, 2025, 10: 100125. |
| [17] | Rame R, Purwanto P, Sudarno S. Industry 5.0 and sustainability: an overview of emerging trends and challenges for a green future[J]. Innovation and Green Development, 2024, 3(4): 100173. |
| [18] | Zafar M H, Langås E F, Sanfilippo F. Exploring the synergies between collaborative robotics, digital twins, augmentation, and industry 5.0 for smart manufacturing: a state-of-the-art review[J]. Robotics and Computer-Integrated Manufacturing, 2024, 89: 102769. |
| [19] | Wang Baicun, Zhou Huiying, Li Xingyu, et al. Human digital twin in the context of industry 5.0[J]. Robotics and Computer-Integrated Manufacturing, 2024, 85: 102626. |
| [20] | Guo Yimin, Guo Yajun, Xiong Ping, et al. A provably secure and practical end-to-end authentication scheme for tactile industrial internet of things[J]. Pervasive and Mobile Computing, 2024, 98: 101877. |
| [21] | Guo Yimin, Zhang Zhenfeng, Guo Yajun. Anonymous authenticated key agreement and group proof protocol for wearable computing[J]. IEEE Transactions on Mobile Computing, 2021, 21(8): 2718-2731. |
| [22] | Guo Yimin, Zhang Zhenfeng, Guo Yajun. Fog-centric authenticated key agreement scheme without trusted parties[J]. IEEE Systems Journal, 2020, 15(4): 5057-5066. |
| [23] | Xu Xianbin, Guo Yajun, Guo Yimin. Fog-enabled private blockchain-based identity authentication scheme for smart home[J]. Computer Communications, 2023, 205: 58-68. |
| [24] | Guo Yimin, Guo Yajun. FogHA: an efficient handover authentication for mobile devices in fog computing[J]. Computers & Security, 2021, 108: 102358. |
| [25] | Alojaiman B. Technological modernizations in the industry 5.0 era: a descriptive analysis and future research directions[J]. Processes, 2023, 11(5): 1318. |
| [26] | Coelho P, Bessa C, Landeck J, et al. Industry 5.0: the arising of a concept[J]. Procedia Computer Science, 2023, 217: 1137-1144. |
| [27] | Zineb B, Benabdelouahab A, Boutracheh H, et al. Exploratory literature review of maturity models in industry 4.0 and 5.0[C]// 2024 4th International Conference on Innovative Research in Applied Science, Engineering and Technology (IRASET). New York: IEEE, 2024: 1-8. |
| [28] | Mathur A, Dabas A, Sharma N. Evolution from industry 1.0 to industry 5.0[C]// 2022 4th International Conference on Advances in Computing, Communication Control and Networking (ICAC3N). New York: IEEE, 2022: 1390-1394. |
| [29] | Zalozhnev A Y, Ginz V N. Industry 4.0:underlying technologies. industry 5.0: human-computer interaction as a tech bridge from industry 4.0 to industry 5.0[C]// 2023 9th International Conference on Web Research (ICWR). New York: IEEE, 2023: 232-236. |
| [30] | Kans M, Campos J. Digital capabilities driving industry 4.0 and 5.0 transformation: insights from an interview study in the maintenance domain[J]. Journal of Open Innovation: Technology, Market, and Complexity, 2024, 10(4): 100384. |
| [31] | Yang Jialu, Liu Ying, Morgan P L. Human-machine interaction towards industry 5.0: human-centric smart manufacturing[J]. Digital Engineering, 2024, 2: 100013. |
| [32] | Gao Yimeng, Zhou Tianqi, Zheng Wenying, et al. High-availability authentication and key agreement for internet of things-based devices in industry 5.0[J]. IEEE Transactions on Industrial Informatics, 2024: 13571-13579. |
| [33] | Nandanwar H, Katarya R. Securing industry 5.0: an explainable deep learning model for intrusion detection in cyber-physical systems[J]. Computers and Electrical Engineering, 2025, 123: 110161. |
| [34] | Vinoth R, Deborah L J, Vijayakumar P, et al. Secure multifactor authenticated key agreement scheme for industrial IoT[J]. IEEE Internet of Things Journal, 2020, 8(5): 3801-3811. |
| [35] | Hu Huanhuan, Liao Longxia, Zhao Junhui. Secure authentication and key agreement protocol for cloud-assisted industrial internet of things[J]. Electronics, 2022, 11(10): 1652. |
| [36] | Han Yiran, Guo Hua, Liu Jianwei, et al. An enhanced multifactor authentication and key agreement protocol in industrial internet of things[J]. IEEE Internet of Things Journal, 2024, 11(9): 16243-16254. |
| [37] | Hasan M K, Weichen Z, Safie N, et al. A survey on key agreement and authentication protocol for internet of things application[J]. IEEE Access, 2024, 12: 61642-61666. |
| [38] | Zhang Yunru, He Debiao, Vijayakumar P, et al. SAPFS: an efficient symmetric-key authentication key agreement scheme with perfect forward secrecy for industrial internet of things[J]. IEEE Internet of Things Journal, 2023, 10(11): 9716-9726. |
| [39] | Zhang Tao, Shen Jian, Yang Huijie, et al. Sustainable authentication and key agreement protocol using chaotic maps for industry 5.0[J]. IEEE Transactions on Consumer Electronics, 2023, 70(1): 1580-1589. |
| [40] | Chaudhry S A, Irshad A, Yahya K, et al. Rotating behind privacy: an improved lightweight authentication scheme for cloud-based IoT environment[J]. ACM Transactions on Internet Technology (TOIT), 2021, 21(3): 1-19. |
| [41] | Xiang Xinyin, Cao Jin, Fan Weiguo. Lightweight privacy-preserving authentication mechanism in 5G-enabled industrial cyber physical systems[J]. Information Sciences, 2024, 666: 120391. |
| [42] | Mahmood K, Ghaffar Z, Farooq M, et al. A security enhanced chaotic-map-based authentication protocol for internet of drones[J]. IEEE Internet of Things Journal, 2024, 11(12): 22301-22309. |
| [43] | Sharma J, Mehra P S. HCFAIUN: a novel hyperelliptic curve and fuzzy extractor-based authentication for secure data transmission in IoT-based UAV networks[J]. Vehicular Communications, 2024, 49: 100834. |
| [44] | Bagga P, Das A K, Rodrigues J J P C. Bilinear pairing-based access control and key agreement scheme for smart transportation[J]. Cyber Security and Applications, 2023, 1: 100001. |
| [45] | Awais S M, Yucheng W, Mahmood K, et al. Provably secure fog-based authentication protocol for VANETs[J]. Computer Networks, 2024, 246: 110391. |
| [46] | Fotouhi M, Bayat M, Das A K, et al. A lightweight and secure two-factor authentication scheme for wireless body area networks in health-care IoT[J]. Computer Networks, 2020, 177: 107333. |
| [47] | Chen C, Li Zhen, Chaudhry S A, et al. Attacks and solutions for a two-factor authentication protocol for wireless body area networks[J]. Security and Communication Networks, 2021(1): 3116593. |
| [48] | Lee S C, Kim S H, Yu S J, et al. Provably secure PUF-based lightweight mutual authentication scheme for wireless body area networks[J]. Electronics, 2022, 11(23): 3868. |
| [49] | Bahache A N, Chikouche N, Akleylek S. Securing cloud-based healthcare applications with a quantum-resistant authentication and key agreement framework[J]. Internet of Things, 2024, 26: 101200. |
| [50] | Guo Ping, Liang Wenfeng, Xu Shuilong. A privacy preserving four-factor authentication protocol for internet of medical things[J]. Computers & Security, 2024, 137: 103632. |
| [51] | Chen C, Chen Zhaoting, Kumari S, et al. LAP-IoHT: a lightweight authentication protocol for the internet of health things[J]. Sensors, 2022, 22(14): 5401. |
| [52] | Kousalya R, Kumar G A S. Relaka: robust ecc based privacy preserving lightweight authenticated key agreement protocol for healthcare applications[J]. Engineering Science and Technology, an International Journal, 2024, 59: 101887. |
| [53] | Duan Xinrui, Guo Yajun, Guo Yimin. Design of anonymous authentication scheme for vehicle fog services using blockchain[J]. Wireless Networks, 2024, 30(1): 193-207. |
| [54] | Wu Anmulin, Guo Yajun, Guo Yimin. A decentralized lightweight blockchain-based authentication mechanism for internet of vehicles[J]. Peer-to-Peer Networking and Applications, 2023, 16(3): 1340-1353. |
| [55] | Guo Yimin, Zhang Zhenfeng, Guo Yajun, et al. BSRA: blockchain-based secure remote authentication scheme for fog-enabled internet of things[J]. IEEE Internet of Things Journal, 2023, 11(2): 3348-3361. |
| [56] | Yang Huan, Guo Yajun, Guo Yimin. Blockchain-based cloud-fog collaborative smart home authentication scheme[J]. Computer Networks, 2024, 242: 110240. |
| [57] | Shao Xiaowei, Guo Yajun, Guo Yimin. A PUF-based anonymous authentication protocol for wireless medical sensor networks[J]. Wireless Networks, 2022, 28(8): 3753-3770. |
| [58] | Yang Huan, Guo Yajun, Guo Yimin. A PUF-based three-party authentication key establishment scheme for fog-enabled smart home[J]. Pervasive and Mobile Computing, 2023, 95: 101843. |
| [59] | Nguyen K D, Dang T K, Kieu-do-nguyen B, et al. ASIC implementation of ASCON lightweight cryptography for IoT applications[J]. IEEE Transactions on Circuits and Systems II: Express Briefs, 2025, 72(1): 278-282. |
| [60] | Jaques S, Naehrig M, Roetteler M, et al. Implementing grover oracles for quantum key search on AES and LowMC[C]// Annual International Conference on the Theory and Applications of Cryptographic Techniques. Heidelberg: Springer, 2020: 280-310. |
| [61] | Zheng Yuanmeng, Luo Qingbin, Li Qiang, et al. Quantum circuit implementations of lightweight authenticated encryption ASCON[J]. The Journal of Supercomputing, 2024, 80(8): 11322-11337. |
| [62] | Tu Shanshan, Badshah A, Alasmary H, et al. EAKE-WC: efficient and anonymous authenticated key exchange scheme for wearable computing[J]. IEEE Transactions on Mobile Computing, 2023, 23(5): 4752-4763. |
| [63] | Guo Yimin, Guo Yajun. CS-LAKA: a lightweight authenticated key agreement protocol with critical security properties for IoT environments[J]. IEEE Transactions on Services Computing, 2023, 16(6): 4102-4114. |
| [64] | Guo Yimin, Zhang Zhenfeng, Guo Yajun. SecFHome: secure remote authentication in fog-enabled smart home environment[J]. Computer Networks, 2022, 207: 108818. |
| [65] | Guo Yimin, Guo Yajun, Xiong Ping, et al. Deeper insight into why authentication schemes in IoT environments fail to achieve the desired security[J]. IEEE Transactions on Information Forensics and Security, 2024, 19: 4615-4627. |
| [66] | Yang Hanlin, Guo Yajun, Guo Yimin. Fault-tolerant security-efficiency combined authentication scheme for manned-unmanned teaming[J]. Computers & Security, 2024, 146: 104052. |
| [67] | Gao Yimeng, Zhou Tianqi, Zheng Wenying, et al. High-availability authentication and key agreement for internet of things-based devices in industry 5.0[J]. IEEE Transactions on Industrial Informatics, 2024, 20(12): 13571-13579. |
| [68] | Zhang Qingyang, Zhou Xiaolong, Zhong Hong, et al. Device-side lightweight mutual authentication and key agreement scheme based on chameleon hashing for industrial internet of things[J]. IEEE Transactions on Information Forensics and Security, 2024, 19: 7895-7907. |
| [69] | Su Xing, Xie Yong, Wang Hui, et al. Blockchain-based privacy-preserving authentication key agreement protocol for industrial wireless sensor networks[C]// 2022 IEEE 28th International Conference on Parallel and Distributed Systems (ICPADS). New York: IEEE, 2023: 234-241. |
| [70] | Tanveer M, Alkhayyat A, Chaudhry S A, et al. REAS-TMIS: resource-efficient authentication scheme for telecare medical information system[J]. IEEE Access, 2022(10): 23008-23021. |
| [71] | Alladi T, Bansal G, Chamola V, et al. SecAuthUAV: a novel authentication scheme for UAV-ground station and UAV-UAV communication[J]. IEEE Transactions on Vehicular Technology, 2020, 69(12): 15068-15077. |
| [1] | 史俊, 王浩, 李增鹏, 顾益宇, 马惠铃. 可信执行环境在隐私计算中的研究现状、关键问题与发展方向综述[J]. 信息网络安全, 2026, 26(8): 1194-1208. |
| [2] | 付章杰, 刘天怿, 宋甫元, 姜琴. 一个支持区块链分片的可验证跨链查询方案[J]. 信息网络安全, 2026, 26(8): 1209-1223. |
| [3] | 韩妍妍, 杜雨芃, 余卓洲, 刘昂, 刘雯. 基于半量子网络的安全区块链[J]. 信息网络安全, 2026, 26(8): 1237-1249. |
| [4] | 刘光华, 王晨龙, 王连坤. 弱网的安全框架研究与实现[J]. 信息网络安全, 2026, 26(5): 667-683. |
| [5] | 李锦凯, 王靖雯, 董立波, 姚文翰, 刘成杰, 文伟平. 基于时序图注意力网络的区块链异常交易检测方法[J]. 信息网络安全, 2026, 26(4): 579-590. |
| [6] | 罗文华, 许世龙, 吕涛, 张宁. 融合布谷鸟过滤与时序B+树的区块链数据溯源机制[J]. 信息网络安全, 2026, 26(3): 442-451. |
| [7] | 梁广俊, 裘宇辰, 司宏韬, 王群, 马卓, 陈宇琪. 区块链虚拟货币溯源与分析[J]. 信息网络安全, 2026, 26(3): 482-490. |
| [8] | 郭毅, 李旭青, 张子蛟, 张宏涛, 张连成, 张香丽. 基于区块链的数据安全共享研究[J]. 信息网络安全, 2026, 26(1): 1-23. |
| [9] | 董佳瑜, 高宏民, 马兆丰, 赖冠辉. 多重签名机制在区块链中的研究及实现[J]. 信息网络安全, 2026, 26(1): 125-138. |
| [10] | 杨昱坤, 肖为恩, 梁博轩, 黄鑫. 面向物联网场景的动态三因素认证密钥协商协议[J]. 信息网络安全, 2025, 25(9): 1407-1417. |
| [11] | 杨建新, 汪晓丁, 林晖. 基于HotStuff和多叉树的改进共识算法[J]. 信息网络安全, 2025, 25(9): 1447-1455. |
| [12] | 佘维, 马天祥, 冯海格, 刘炜. 基于RBF机制的无痕区块链隐蔽通信方案[J]. 信息网络安全, 2025, 25(8): 1302-1312. |
| [13] | 王梅, 杨潇然, 李增鹏. 简洁低交互的物联网设备认证协议研究[J]. 信息网络安全, 2025, 25(7): 1032-1043. |
| [14] | 高扬, 张琪, 王琛, 徐剑. 新型可组合的认证分布式数据结构模型研究[J]. 信息网络安全, 2025, 25(7): 1111-1125. |
| [15] | 刘峰, 黄灏. 一种基于智能合约预言机技术的主动式去中心化监管传感网络架构[J]. 信息网络安全, 2025, 25(6): 898-909. |
| 阅读次数 | ||||||
|
全文 |
|
|||||
|
摘要 |
|
|||||