信息网络安全 ›› 2026, Vol. 26 ›› Issue (9): 1341-1353.doi: 10.3969/j.issn.1671-1122.2026.09.002
面向大语言模型的成员推理攻击与防御技术综述
聂豪杰1,2, 孙德刚1,2, 潘兴博1,2, 万巍1,2, 龙春1,2( )
- 1
中国科学院计算机网络信息中心 北京 100083
2中国科学院大学计算机科学与技术学院 北京 101408
-
收稿日期:2026-05-06出版日期:2026-09-10发布日期:2026-09-30 -
通讯作者:龙春 E-mail:anquanip@cnic.cn -
作者简介:聂豪杰(2002—),男,河南,硕士研究生,主要研究方向为大模型安全、隐私计算|孙德刚(1970—),男,吉林,正高级工程师,博士,主要研究方向为高安全等级系统防护技术、网络空间安全|潘兴博(1990—),男,河北,副研究员,博士,主要研究方向为量子保密通信、量子同态加密、数据安全|万巍(1982—),男,湖北,高级工程师,博士,主要研究方向为网络空间安全|龙春(1979—),男,湖北,正高级工程师,博士,CCF会员,主要研究方向为人工智能、攻击检测、恶意域名检测、网络流量分析 -
基金资助:国家重点研发计划(2023YFC3304704);国家自然科学基金(62401324)
A survey of membership inference attacks and defenses for large language models
Nie Haojie1,2, Sun Degang1,2, Pan Xingbo1,2, Wan Wei1,2, Long Chun1,2()
- 1
Computer Network Information Center ,Chinese Academy of Sciences Beijing 100083, China
2School of Computer Science and Technology ,University of Chinese Academy of Sciences Beijing 101408, China
-
Received:2026-05-06Online:2026-09-10Published:2026-09-30 -
Contact:Long Chun E-mail:anquanip@cnic.cn

摘要:
为应对大语言模型带来的隐私泄露、版权争议和数据透明性问题,文章系统综述成员推理攻击与防御技术。以大模型生命周期和系统组件为双主线:首先,说明成员推理的形式化定义与威胁模型,并阐述其由过拟合向局部与条件记忆演化的理论基础,明确相较于已有通用成员推理综述的研究增量;然后,梳理预训练、微调、对齐、黑盒应用程序接口(API)、多模态和检索增强生成(RAG)等场景中的攻击,重点补充 LiRA、MoPe、ReCaLL 以及多类 RAG 攻击;进一步对 WikiMIA、MIMIR 等基准的代表性结果进行定量对照,指出时间切分造成的分布偏差会显著高估攻击能力;最后,从数据治理、正则化与差分隐私、知识蒸馏、解码过滤和机器遗忘5个层面构建纵深防御体系。分析结果表明,攻击信号已由全局统计转向逐样本校准、局部记忆峰、条件变化和系统知识覆盖,而严格同分布、低误报率评价仍是制约实用审计的核心问题。
中图分类号:
引用本文
聂豪杰, 孙德刚, 潘兴博, 万巍, 龙春. 面向大语言模型的成员推理攻击与防御技术综述[J]. 信息网络安全, 2026, 26(9): 1341-1353.
Nie Haojie, Sun Degang, Pan Xingbo, Wan Wei, Long Chun. A survey of membership inference attacks and defenses for large language models[J]. Netinfo Security, 2026, 26(9): 1341-1353.
图1
LLM生命周期、成员对象与攻击入口
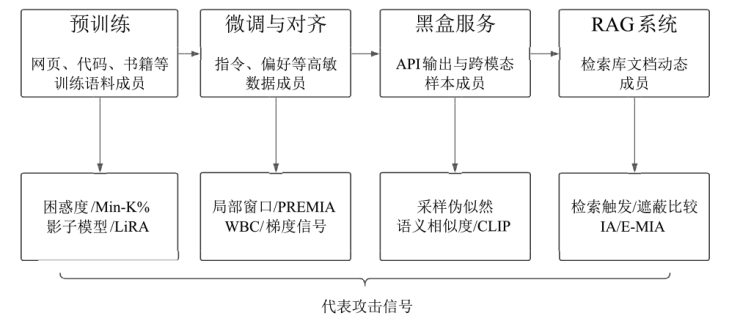
图2
数据重复与MIA关系
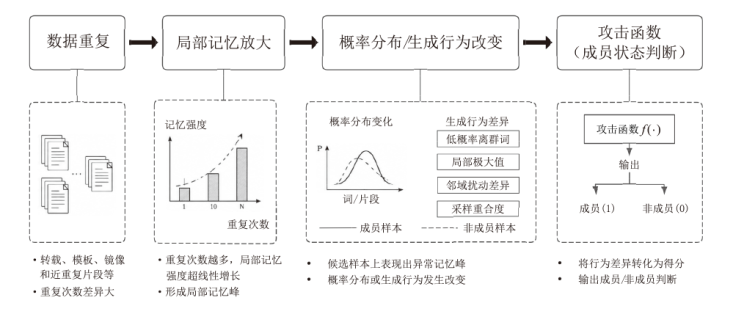
表1
本文与既有成员推理综述的范围比较
| 文献 | 主要范围 | 防御 覆盖 | 对LLM/RAG覆盖 | 本文增量 |
|---|---|---|---|---|
| 文献[ | 通用MIA;威胁 模型、攻击知识与数据类型 | 传统训练/输出防御 | 较少 | 生命周期与系统组件;统一基准批判 |
| 文献[ | 判别、生成与联邦学习MIA | 经典 策略 | 无 | LLM局部记忆、对齐、多模态、RAG |
| 文献[ | 通用攻防与应用 | 较系统 | 有限 | 给出WikiMIA/MIMIR量化对照 |
| 文献[ | MIA防御分类与 评价 | 系统 | 少量 | 扩展到解码过滤、RAG与遗忘审计 |
| 文献[ | 大规模模型MIA | 概述 | 覆盖部分新场景 | 生命周期组织、统一基准定量比较和 防御表 |
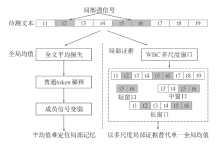
图3
多尺度滑动窗口成员推断攻击原理
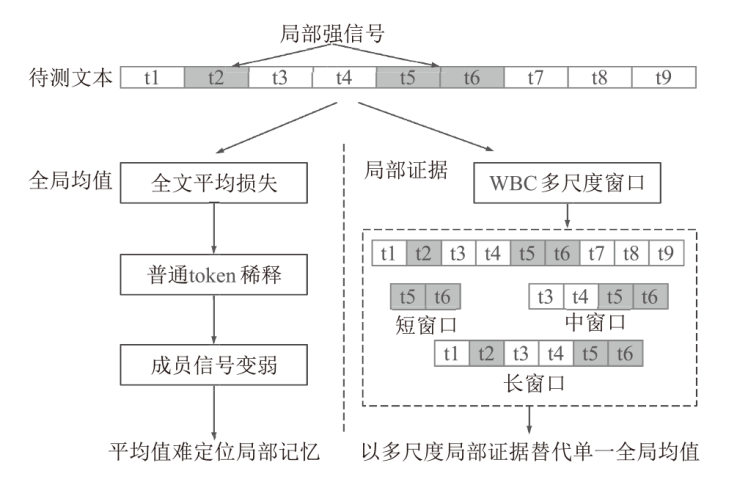
图4
RAG场景的文档成员推理链路
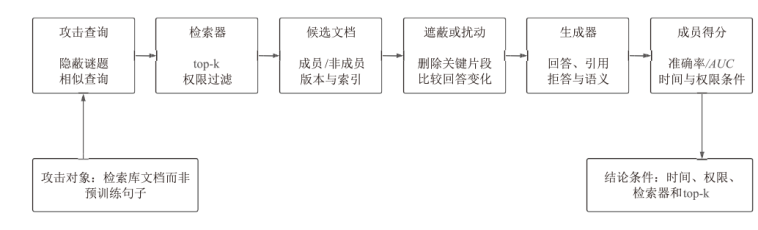
表2
LLM主流MIA方法对比
| 阶段/场景 | 代表方法 | 访问 | 核心信号 | 关键依赖与局限 |
|---|---|---|---|---|
| 预训练 | PPL/Zlib[ | 灰盒 | 全局可预测性 | 混淆样本难度 |
| 预训练 | LiRA/校准[ | 黑/灰盒 | 逐样本似然比 | 影子模型或 校准集昂贵 |
| 预训练 | Min-K%/Min-K%++[ | 灰盒 | 低概率token与局部模态 | 需要token概率 |
| 预训练 | MoPe/ReCaLL[ | 灰盒 | 参数扰动/条件似然变化 | 多次推理或 上下文敏感 |
| 数据集级 | Dataset Inference[ | 灰盒 | 多样本统计 聚合 | 要求候选集合 |
| 微调 | SPV/Neighbour/DF-MIA[ | 灰盒 | 自校准与 邻域差异 | 改写质量影响 结果 |
| 微调前沿 | WBC[ | 灰盒 | 多尺度局部 窗口 | — |
| 对齐 | PREMIA[ | 灰盒 | 偏好损失 | — |
| 黑盒API | PETAL/SaMIA[ | 黑盒 | 语义近似/采样伪似然 | 查询成本高 |
| 多模态 | CLIP/VLLM/Self-Comparison[ | 灰/黑盒 | 跨模态匹配与集合内参照 | 成员单位需明确 |
| RAG | RAG-MIA/GIB/RAG-leaks/MBA[ | 黑盒 | 检索触发、 生成依赖、 掩码恢复 | 受检索召回和常识影响 |
| RAG前沿 | Riddle/E-MIA[ | 黑盒 | 隐蔽题目/ 事实考试 | 预印本需复核 |
表3
代表性方法在WikiMIA、MIMIR及RAG基准上的定量结果
| 基准/协议 | 模型与设置 | 方法 | ROC-AUC | 低FPR结果 |
|---|---|---|---|---|
| WikiMIA,32 token | 6类模型平均 | Min-K%++[ | 0.753 | TPR@1%FPR=6.6% |
| WikiMIA,32 token | 6类模型平均 | ReCaLL[ | 0.901 | TPR@1%FPR=17.5% |
| WikiMIA,64 token | 6类模型平均 | Min-K%++[ | 0.759 | TPR@1%FPR=10.6% |
| WikiMIA,64 token | 6类模型平均 | ReCaLL[ | 0.913 | TPR@1%FPR=15.4% |
| WikiMIA,128 token | 6类模型平均 | Min-K%++[ | 0.752 | TPR@1%FPR=3.2% |
| WikiMIA,128 token | 6类模型平均 | ReCaLL[ | 0.900 | TPR@1%FPR=16.9% |
| MIMIR,13-gram, 七域宏平均 | Pythia-12B | Min-K%[ | 0.559 | TPR@1%FPR=4.0% |
| MIMIR,13-gram, 七域宏平均 | Pythia-12B | Min-K%++[ | 0.585 | TPR@1%FPR=4.3% |
| MIMIR,13-gram, 七域宏平均 | Pythia-12B | ReCaLL[ | 0.565 | TPR@1%FPR=4.4% |
| Pile,单方法设置 | Pythia-160M | MoPe[ | 0.646 | TPR@5%FPR=4.9% |
| RAG,Health-CareMagic/MS-MARCO/NQ | GPT-4o-mini+BGE | MBA[ | 0.880/ 0.860/ 0.900 | 成员为检索库文档 |
图5
WikiMIA与MIMIR统一协议内的ROC-AUC对比
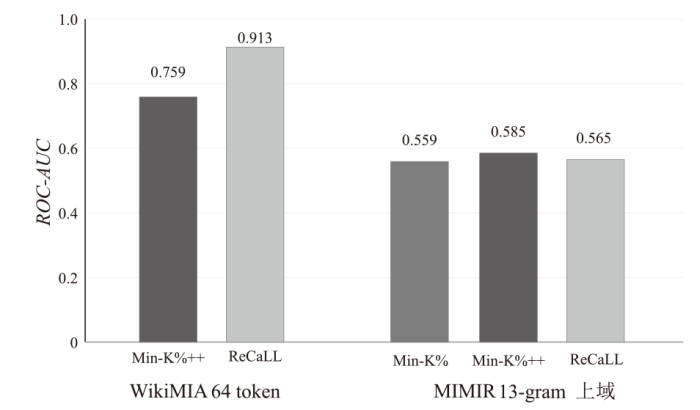
图6
面向成员推理的纵深防御体系
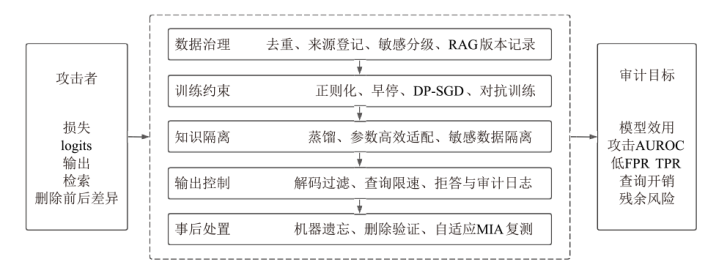
表4
大模型成员推理防御机制比较
| 防御类别 | 适用阶段 | 代表机制 | 隐私保证 | 主要代价 | 局限 |
|---|---|---|---|---|---|
| 去重与 数据治理 | 训练前 | 多粒度去重、PII清洗、数据血缘[ | 经验 | 索引与 误删 | 不消除单次罕见记忆 |
| 正则化 | 训练中 | 早停、dropout、标签平滑、对抗正则[ | 经验 | 低至中 | 依赖已知 攻击 |
| 差分隐私 | 训练/ 微调 | DP-SGD、DP-Forward[ | 形式化 | 效用与 算力 | 预算选择 困难 |
| 知识蒸馏 | 训练后 | 知识迁移、 交叉蒸馏[ | 通常经验 | 教师推理与学生 训练 | 教师输出仍可泄露 |
| 输出扰动/过滤 | 部署 | MemGuard、相似 片段过滤[ | 经验 | 延迟与 误拒 | 不移除参数记忆 |
| 查询控制/拒答 | 部署 | MIA-Tuner、速率限制、日志[ | 经验 | 可用性 | 提示改写可绕过 |
| 机器遗忘 | 退出 | 去记忆化、知识遗忘、双用途训练[ | 方法相关 | 再训练与能力损失 | 拒答不等于遗忘 |
| RAG访问控制 | 检索/ 生成 | 权限过滤、最小返回、索引审计[ | 系统 | 召回与 答案质量 | 侧信道仍 存在 |
| [1] | Hu Hongsheng, Salcic Z, Sun Lichao, et al. Membership inference attacks on machine learning: a survey[J]. ACM Computing Surveys, 2022, 54(11): 1-37. |
| [2] | 王鹏焱. 机器学习中的成员推断攻击与防御研究[J]. 信息技术与网络安全, 2021, 40(8): 65-70, 83. |
| [3] |
Niu Jun, Liu Peng, Zhu Xiaoyan, et al. A survey on membership inference attacks and defenses in machine learning[J]. Journal of Information and Intelligence, 2024, 2(5): 404-454.
doi: 10.1016/j.jiixd.2024.02.001 URL |
| [4] | Hu Li, Yan Anli, Yan Hongyang, et al. Defenses to membership inference attacks: a survey[J]. ACM Computing Surveys, 2023, 56(4): 1-34. |
| [5] | Shokri R, Stronati M, Song Congzheng, et al. Membership inference attacks against machine learning models[C]// The 38th IEEE Symposium on Security and Privacy. New York: IEEE, 2017: 3-18. |
| [6] | Yeom S, Giacomelli I, Fredrikson M, et al. Privacy risk in machine learning: analyzing the connection to overfitting[C]// The 31st IEEE Computer Security Foundations Symposium. New York: IEEE, 2018: 268-282. |
| [7] | Carlini N, Tramer F, Wallace E, et al. Extracting training data from large language models[C]// The 30th USENIX Security Symposium (USENIX Security 21). Berkeley: USENIX, 2021: 2633-2650. |
| [8] | Carlini N, Ippolito D, Jagielski M, et al. Quantifying memorization across neural language models[C]// International Conference on Learning Representations. Kigali: ICLR, 2023: 1-19. |
| [9] | Brown H, Lee K, Mireshghallah F, et al. What does it mean for a language model to preserve privacy?[C]// The 5th ACM Conference on Fairness, Accountability, and Transparency. New York: ACM, 2022: 2280-2292. |
| [10] | Pan Xudong, Zhang Mi, Ji Shouling, et al. Privacy risks of general-purpose language models[C]// The 41st IEEE Symposium on Security and Privacy. New York: IEEE, 2020: 1314-1331. |
| [11] | Mireshghallah F, Goyal K, Uniyal A, et al. Quantifying privacy risks of masked language models using membership inference attacks[C]// The 27th Conference on Empirical Methods in Natural Language Processing. Stroudsburg: ACL, 2022: 8332-8347. |
| [12] |
Hisamoto S, Post M, Duh K. Membership inference attacks on sequence-to-sequence models: is my data in your machine translation system?[J]. Transactions of the Association for Computational Linguistics, 2020, 8: 49-63.
doi: 10.1162/tacl_a_00299 |
| [13] | 杨盼盼, 张信明. 基于标签的无数据的成员推理攻击[J]. 网络安全与数据治理, 2023, 42(5): 44-49. |
| [14] | Wu Hengyu, Cao Yang. Membership inference attacks on large-scale models: a survey[EB/OL]. (2025-08-31)[2026-04-28]. https://arxiv.org/abs/2503.19338v3. |
| [15] |
Feretzakis G, Papaspyridis K, Gkoulalas-divanis A, et al. Privacy-preserving techniques in generative AI and large language models: a narrative review[J]. Information, 2024, 15(11): 1-25.
doi: 10.3390/info15010001 URL |
| [16] | Li Jiacheng, Li Ning, Ribeiro B. Membership inference attacks and defenses in classification models[C]// The 11th ACM Conference on Data and Application Security and Privacy. New York: ACM, 2021: 5-16. |
| [17] | Carlini N, Chien S, Nasr M, et al. Membership inference attacks from first principles[C]// The 43rd IEEE Symposium on Security and Privacy. New York: IEEE, 2022: 1897-1914. |
| [18] | Kandpal N, Wallace E, Raffel C. Deduplicating training data mitigates privacy risks in language models[C]// The 39th International Conference on Machine Learning. Baltimore: PMLR, 2022: 10697-10707. |
| [19] | Lee K, Ippolito D, Nystrom A, et al. Deduplicating training data makes language models better[C]// The 60th Annual Meeting of the Association for Computational Linguistics. Stroudsburg: ACL, 2022: 8424-8445. |
| [20] | Ye Jiayuan, Maddi A, Murakonda S K, et al. Enhanced membership inference attacks against machine learning models[C]// The 29th ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2022: 3093-3106. |
| [21] | Shi Weijia, Ajith A, Xia Mengzhou, et al. Detecting pretraining data from large language models[C]// International Conference on Learning Representations. Vienna: ICLR, 2024: 1-18. |
| [22] | Zhang Jingyang, Sun Jingwei, Yeats E, et al. Min-K%++: improved baseline for detecting pre-training data from large language models[C]// International Conference on Learning Representations. Singapore: ICLR, 2025: 1-18. |
| [23] | Duan M, Suri A, Mireshghallah N, et al. Do membership inference attacks work on large language models?[C]// The 1st Conference on Language Modeling. Philadelphia: COLM, 2024: 1-33. |
| [24] | Li M, Wang J, Wang J, et al. MoPe: Model perturbation based privacy attacks on language models[C]// The 28th Conference on Empirical Methods in Natural Language Processing. Stroudsburg: ACL, 2023: 13647-13660. |
| [25] | Xie R, Wang Junlin, Huang Ruomin, et al. ReCaLL: membership inference via relative conditional log-likelihoods[C]// The 29th Conference on Empirical Methods in Natural Language Processing. Stroudsburg: ACL, 2024: 8671-8689. |
| [26] | Anderson M, Amit G, Goldsteen A.Is my data in your retrieval database? membership inference attacks against retrieval-augmented generation[C]// The 11th International Conference on Information Systems Security and Privacy. Heidelberg: Springer, 2025: 474-485. |
| [27] | Li Yuying, Liu Gaoyang, Wang Chen, et al. Generating is believing: membership inference attacks against retrieval-augmented generation[C]// The 50th IEEE International Conference on Acoustics, Speech and Signal Processing. New York: IEEE, 2025: 1-5. |
| [28] | Wang Guangshuo, He Jiajun, Li Hao, et al. RAG-leaks: difficulty-calibrated membership inference attacks on retrieval-augmented generation[J]. Science China Information Sciences, 2025, 68(6): 1-18. |
| [29] | Liu Mingrui, Zhang Sixiao, Long Cheng. Mask-based membership inference attacks for retrieval-augmented generation[C]// The 34th Web Conference. New York: ACM, 2025: 2894-2907. |
| [30] | Salem A, Zhang Yang, Humbert M, et al. ML-Leaks: model and data independent membership inference attacks and defenses on machine learning models[C]// Network and Distributed System Security Symposium. Reston: NDSS, 2019: 1-15. |
| [31] | He Yu, Li Boheng, Liu Liu, et al. Towards label-only membership inference attack against pre-trained large language models[C]// The 34th USENIX Security Symposium. Berkeley: USENIX, 2025: 1609-1628. |
| [32] | Kaneko M, Ma Y, Wata Y, et al. Sampling-based pseudo-likelihood for membership inference attacks[C]// Findings of the Association for Computational Linguistics. Stroudsburg: ACL, 2025: 8894-8907. |
| [33] | Hui Bo, Yang Yuchen, Yuan Haolin, et al. Practical blind membership inference attack via differential comparisons[C]// Network and Distributed System Security Symposium. Reston: NDSS, 2021: 1-17. |
| [34] | Maini P, Jia Hengrui, Papernot N, et al. LLM dataset inference: did you train on my dataset?[C]// Advances in Neural Information Processing Systems. Red Hook: NeurIPS, 2024: 124069-124092. |
| [35] | Meeus M, Shilov I, Faysse M, et al. Copyright traps for large language models[EB/OL]. (2024-06-04)[2026-04-28]. https://arxiv.org/abs/2402.09363v2. |
| [36] | Mireshghallah F, Uniyal A, Wang Tianhao, et al. An empirical analysis of memorization in fine-tuned autoregressive language models[C]// The 27th Conference on Empirical Methods in Natural Language Processing. Stroudsburg: ACL, 2022: 1816-1826. |
| [37] | Fu Wenjie, Wang Huandong, Gao Chen, et al. Membership inference attacks against fine-tuned large language models via self-prompt calibration[C]// Advances in Neural Information Processing Systems. Red Hook: NeurIPS, 2024: 134981-135010. |
| [38] | Mattern J, Mireshghallah F, Jin Zhijing, et al. Membership inference attacks against language models via neighbourhood comparison[C]// Findings of the Association for Computational Linguistics. Stroudsburg: ACL, 2023: 11330-11343. |
| [39] | Huang Zhiheng, Liu Yannan, He Daojing, et al. DF-MIA: a distribution-free membership inference attack on fine-tuned large language models[C]// The AAAI Conference on Artificial Intelligence. Palo Alto: AAAI, 2025: 343-351. |
| [40] | Puerto H, Gubri M, Yun S, et al. Scaling up membership inference: when and how attacks succeed on large language models[C]// Findings of the Association for Computational Linguistics. Stroudsburg: ACL, 2025: 4165-4182. |
| [41] | Chen Yuetian, Du Yuntao, Zhang Kaiyuan, et al. Window-based membership inference attacks against fine-tuned large language models[C]// The 35th USENIX Security Symposium. Berkeley: USENIX, 2026: 1187-1206. |
| [42] | Meeus M, Shilov I, Jain S, et al. SoK: membership inference attacks on LLMs are rushing nowhere (and how to fix it)[C]// The 3rd IEEE Conference on Secure and Trustworthy Machine Learning (SaTML). New York: IEEE, 2025: 385-401. |
| [43] | Chen Bowen, Han N, Miyao Y. A statistical and multi-perspective revisiting of the membership inference attack in large language models[C]// The 63rd Annual Meeting of the Association for Computational Linguistics. Stroudsburg: ACL, 2025: 22854-22874. |
| [44] | Feng Qizhang, Kasa S R, Kasa S K, et al. Exposing privacy gaps: membership inference attack on preference data for LLM alignment[C]// The 28th International Conference on Artificial Intelligence and Statistics. San Diego: PMLR, 2025: 5221-5229. |
| [45] | Ko M, Jin Ming, Wang Chenguang, et al. Practical membership inference attacks against large-scale multi-modal models: a pilot study[C]// The 18th IEEE/CVF International Conference on Computer Vision. New York: IEEE, 2023: 4848-4858. |
| [46] | Li Zhan, Wu Yongtao, Chen Yihang, et al. Membership inference attacks against large vision-language models[C]// Advances in Neural Information Processing Systems. Red Hook: NeurIPS, 2024: 98645-98674. |
| [47] | Ren Jie, Chen Kangrui, Chen Chen, et al. Self-Comparison for dataset-level membership inference in large (vision-)language model[C]// The 34th Web Conference. New York: ACM, 2025: 910-920. |
| [48] | Naseh A, Peng Yuefeng, Suri A, et al. Riddle me this! stealthy membership inference for retrieval-augmented generation[C]// The 32nd ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2025: 1245-1259. |
| [49] | Guan Zelin, Zhuo Shengda, Li Zeyan, et al. E-MIA: exam-style black-box membership inference attacks against RAG systems[EB/OL]. (2026-05-01)[2026-04-28]. https://arxiv.org/abs/2605.00955v1. |
| [50] | Nasr M, Shokri R, Houmansadr A. Machine learning with membership privacy using adversarial regularization[C]// The 25th ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2018: 634-646. |
| [51] | Jayaraman B, Evans D. Evaluating differentially private machine learning in practice[C]// The 28th USENIX Security Symposium (USENIX Security 19). Berkeley: USENIX, 2019: 1895-1912. |
| [52] | Du Minxin, Yue Xiang, Chow S S M, et al. DP-Forward: fine-tuning and inference on language models with differential privacy in forward pass[C]// The 30th ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2023: 2665-2679. |
| [53] | Shejwalkar V, Houmansadr A. Membership privacy for machine learning models through knowledge transfer[C]// The AAAI Conference on Artificial Intelligence. Palo Alto: AAAI, 2021: 9549-9557. |
| [54] |
Zheng Junxiang, Cao Yongzhi, Wang Hanpin. Resisting membership inference attacks through knowledge distillation[J]. Neurocomputing, 2021, 452: 114-126.
doi: 10.1016/j.neucom.2021.04.082 URL |
| [55] | Chourasia R, Enkhtaivan B, Ito K, et al. Knowledge cross-distillation for membership privacy[J]. Proceedings on Privacy Enhancing Technologies, 2022(2): 362-377. |
| [56] | Jia Jinyuan, Salem A, Backes M, et al. Memguard: defending against black-box membership inference attacks via adversarial examples[C]// The 26th ACM SIGSAC Conference on Computer and Communications Security. New York: ACM, 2019: 259-274. |
| [57] | Fu Wenjie, Wang Huandong, Gao Chen, et al. MIA-Tuner: adapting large language models as pre-training text detector[C]// The AAAI Conference on Artificial Intelligence. Palo Alto: AAAI, 2025: 27295-27303. |
| [58] | Ippolito D, Tramer F, Nasr M, et al. Preventing generation of verbatim memorization in language models gives a false sense of privacy[C]// The 16th International Natural Language Generation Conference. Stroudsburg: ACL, 2023: 28-53. |
| [59] | Kassem A, Mahmoud O, Saad S. Preserving privacy through dememorization: an unlearning technique for mitigating memorization risks in language models[C]// The 28th Conference on Empirical Methods in Natural Language Processing. Stroudsburg: ACL, 2023: 4360-4379. |
| [60] | Jang J, Yoon D, Yang S, et al. Knowledge unlearning for mitigating privacy risks in language models[C]// The 61st Annual Meeting of the Association for Computational Linguistics. Stroudsburg: ACL, 2023: 14389-14408. |
| [61] | Yao Jin, Chien E, Du Minxin, et al. Machine unlearning of pre-trained large language models[C]// The 62nd Annual Meeting of the Association for Computational Linguistics. Stroudsburg: ACL, 2024: 8403-8419. |
| [62] |
Liu Sijia, Yao Yuanshun, Jia Jinghan, et al. Rethinking machine unlearning for large language models[J]. Nature Machine Intelligence, 2025, 7(2): 181-194.
doi: 10.1038/s42256-025-00985-0 |
| [63] | Tran T, Liu Ruixuan, Xiong Li. Tokens for learning, tokens for unlearning: mitigating membership inference attacks in large language models via dual-purpose training[C]// Findings of the Association for Computational Linguistics. Stroudsburg: ACL, 2025: 22872-22888. |
| [64] | Xu Heng, Zhu Tianqing, Zhang Lefeng, et al. Machine unlearning: a survey[J]. ACM Computing Surveys, 2024, 56(1): 1-36. |
| [1] | 马文飞, 龙春, 李婧, 杨帆, 付豫豪. 大语言模型微调阶段的后门投毒:攻击、防御与评估[J]. 信息网络安全, 2026, 26(9): 1354-1368. |
| [2] | 宋铮, 杨芮淇, 李化成. 仓库级静态漏洞检测综述:从规则驱动到大语言模型与智能体[J]. 信息网络安全, 2026, 26(9): 1369-1382. |
| [3] | 姚戊煌, 王佳鹏, 陈康冰, 郑之涵, 谭毓安. 基于指令翻译插桩的LLM辅助固件内存泄漏分析[J]. 信息网络安全, 2026, 26(7): 1087-1100. |
| [4] | 杨乔炀, 范希明, 贾鹏. 基于大语言模型的语义知晓的模糊测试驱动生成方案[J]. 信息网络安全, 2026, 26(7): 1128-1148. |
| [5] | 孙钰, 张轩瑞, 刘新宇. 高级持续性威胁检测与溯源研究进展[J]. 信息网络安全, 2026, 26(6): 833-853. |
| [6] | 苗博, 袁得嵛, 张腾, 杨懿, 黄赞. 基于思维链污染的检索增强生成后门攻击[J]. 信息网络安全, 2026, 26(6): 977-998. |
| [7] | 胡倾城, 张婉, 袁亚丽, 张静. 基于多视图知识增强的大语言模型事实型幻觉优化方法[J]. 信息网络安全, 2026, 26(5): 772-787. |
| [8] | 李子豪, 张锋巍. 基于可信执行环境的联邦学习平台[J]. 信息网络安全, 2026, 26(5): 788-808. |
| [9] | 崔津华, 董亮, 杨新. 大语言模型推理隐私保护技术综述[J]. 信息网络安全, 2026, 26(4): 503-520. |
| [10] | 易文哲, 徐枭洋, 石磊, 庄泳, 王鹃. 基于知识迁移和冻结的模型反演防御方法[J]. 信息网络安全, 2026, 26(4): 566-578. |
| [11] | 李岩, 杨文章, 薛吟兴. 基于LLM翻译与差分测试的跨语言编译器模糊测试[J]. 信息网络安全, 2026, 26(4): 591-604. |
| [12] | 胡勉宁, 李欣, 李明锋, 袁得嵛. 基于大语言模型的多策略增强中文网络威胁情报实体抽取研究[J]. 信息网络安全, 2026, 26(4): 615-625. |
| [13] | 袁明, 邹其霖, 袁文骐, 王群. 大语言模型提示词注入攻击与防御综述[J]. 信息网络安全, 2026, 26(3): 341-354. |
| [14] | 顾兆军, 李丽, 隋翯. 基于大语言模型的SQL注入漏洞检测载荷生成方法[J]. 信息网络安全, 2026, 26(2): 274-290. |
| [15] | 郭毅, 李旭青, 张子蛟, 张宏涛, 张连成, 张香丽. 基于区块链的数据安全共享研究[J]. 信息网络安全, 2026, 26(1): 1-23. |
| 阅读次数 | ||||||
|
全文 |
|
|||||
|
摘要 |
|
|||||