Netinfo Security ›› 2026, Vol. 26 ›› Issue (8): 1250-1263.doi: 10.3969/j.issn.1671-1122.2026.08.007
Previous Articles Next Articles
Review of zero trust architecture and its technical applications
Zhao Min, Qu Kangjian( )
College of Command and Control Engineering ,Army Engineering University Nanjing 210007, China
-
Received:2026-03-10Online:2026-08-10Published:2026-09-23 -
Contact:Qu Kangjian E-mail:1622038290@qq.com

CLC Number:
Cite this article
Zhao Min, Qu Kangjian. Review of zero trust architecture and its technical applications[J]. Netinfo Security, 2026, 26(8): 1250-1263.
share this article
Add to citation manager EndNote|Ris|BibTeX
URL: http://netinfo-security.org/EN/10.3969/j.issn.1671-1122.2026.08.007
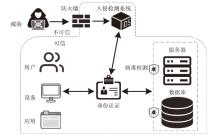
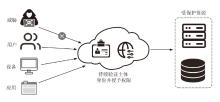
| 比较层面 | 零信任模型 | 传统模型 |
|---|---|---|
| 网络边界 | 不存在传统意义上的边界,任何位置发出的请求都需要验证 | 依赖明确的物理或逻辑边界来区分内部网络和外部网络 |
| 信任假设 | 用户、设备或网络都不应默认信任,所有访问请求都需要 严格审查 | 默认信任内部网络,外部 网络通过边界设备防护 |
| 技术架构 | 无明确边界,采用身份管理、行为分析、最小权限访问和 强认证机制等技术 | 基于防火墙、入侵检测系统、虚拟专用网络等传统边界安全技术 |
| 身份验证 | 持续身份验证 | 一次性验证 |
| 访问控制 | 基于身份、属性、风险等访问控制和最小权限原则,实现精细化控制 | 主要基于网络位置、防火墙设置,如基于IP的访问控制 |
| 方法 | 应用场景 | 内容 |
|---|---|---|
| 文献[ | 通用 | 提出一种基于图像识别的验证算法,通过结合图像和用户关系实现双因素认证 |
| 文献[ | 云计算 | 系统性综述多因素验证在云计算中的应用,提出多种增强身份验证方案 |
| 文献[ | 移动设备 | 在电子支付应用中,结合硬件和软件双因素认证提升移动端应用的安全性 |
| 文献[ | 物联网 | 结合智能卡、生物识别和令牌设备,设计了一种适用于物联网环境的多因素验证方案 |
| 方法 | 上下文信息 | 内容 |
|---|---|---|
| 文献[ | 位置 | 通过Wi-Fi和基站数据获取用户位置, 利用位置信息进行风险评估,并确定应采取的主动身份验证方式 |
| 文献[ | 用户移动模式 | 通过n-gram模型对用户的移动模式进行建模,从而识别手机设备是否可能被盗的异常实例 |
| 文献[ | 用户行为特征 | 利用设备位置、电子邮件检查时间等行为特征进行计算,并将结果与阈值进行对比,以判断是否执行隐式身份认证 |
| 文献[ | 时空信息、 操作系统、设备型号、余弦相似度 | 一种针对云服务的上下文感知用户身份验证机制,该机制通过用户的代理采集上下文信息,并将其发送至云端身份 验证系统。系统将收到的信息与用户的已有信息进行对比,从而验证身份 |
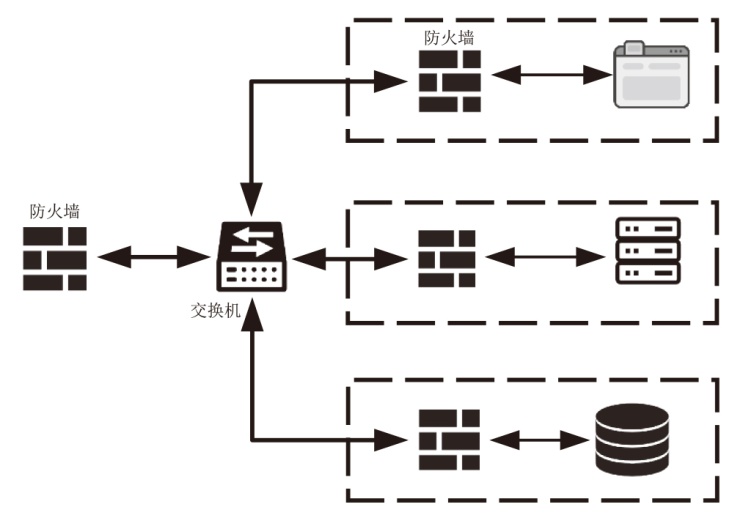
| 项目 | 部署模式 | 微隔离方法 |
|---|---|---|
| OpenZiti[ | 覆盖模型 | 采用SDP架构的基于身份的访问控制策略 |
| Cisco ACI[ | 本地模型 | 基于网络身份(如IP地址、端口)和 更高层级的可视化能力 |
| VMware NSX[ | 第三方模型 | 基于网络身份,采用第三方提供的高层级可视化产品 |
| Istio[ | 覆盖模型 | 基于API感知的访问控制,将工作流分解为更小的基于容器的服务,这些服务使用API进行通信 |
| 方法 | 应用场景 | 主要贡献 | 优缺点 |
|---|---|---|---|
| 文献[ | 5G | 提出5G零信任参考模型,利用机器学习实现基于上下文的访问控制,探讨区块链认证 | 优点:架构解耦,抗内部 攻击; 缺点:验证开销大,影响 吞吐量 |
| 文献[ | 身份联盟 | 提出零信任联盟,引入上下文属性提供者,基于UMA协议设计用户授权机制,解决依赖方上下文缺失问题 | 优点:隐私保护,去中心化; 缺点:上下文未标准化, 扩展性差 |
| 文献[ | 人工智能、无人机 | 摒弃边界防护,整合可解释人工智能技术,对所有实体进行持续认证 | 优点:提升决策透明度和识别准确性; 缺点:难以构建适应无人机动态特性的持续认证机制 |
| 文献[ | VR、元宇宙 | 联邦学习保护生物识别隐私,结合多模态数据与自适应机制提升认证能力 | 优点:多模态与自适应机制提升可用性; 缺点:算法在生物识别认证中准确率较低 |
| 文献[ | 物联网 | 基于SDP实现先认证后通信,通过多维度实时评估实现动态访问 | 优点:资源受限终端性能 消耗低; 缺点:网关至服务器段无 安全保护 |
| 文献[ | 远程访问 | 采集固件层与内核层数据,设计信任评估算法持续评估终端安全 | 优点:基于固件信息的持续采集方法; 缺点:仅限Windows设备,兼容性差 |
| 文献[ | 敏感数据 安全保护 | 基于模糊层次分析法计算多源属性信任值,引入滑动窗口更新机制 | 优点:实现基于多源属性的动态信任评估; 缺点:时延与CPU消耗高于默认算法 |
| [1] | Spina M G, De R F, Iera A. From centralized to distributed and ubiquitous in-network defense for future 6G networks[C]//2024 15th International Conference on Network of the Future (NoF). New York: IEEE, 2024: 91-95. |
| [2] | Makhdoomi A, Jan N, Pala K, et al. Conventional and next generation firewalls in network security and its applications[C]// 2022 International Conference on Computing, Communication, and Intelligent Systems (ICCCIS). New York: IEEE, 2022: 964-969. |
| [3] | Hylender D, Langlois P, Pinto A, et al. Version 2024 data breach investigations report[EB/OL]. (2024-05-23)[2026-02-16]. https://www.verizon.com/business/resources/reports/dbir/CMP=OOH_SMB_OTH_22222_MC_20200501_NA_NM20200079_00001. |
| [4] |
王群, 袁泉, 李馥娟, 等. 零信任网络及其关键技术综述[J]. 计算机应用, 2023, 43(4): 1142-1150.
doi: 10.11772/j.issn.1001-9081.2022030453 |
| [5] | Kindervag J, Balaouras S, Mak K, et al. No more chewy centers: introducing the zero trust model of information security[EB/OL]. (2016-03-23)[2026-02-16]. https://www.forrester.com/report/No-More-Chewy-Centers-The-Zero-Trust-Model-Of-Information-Security/RES56682. |
| [6] | Bertino E. Zero trust architecture: does it help[J]. IEEE Security & Privacy, 2021, 19(5): 95-96. |
| [7] | NIST. Zero trust architecture[EB/OL]. (2020-08-10)[2026-02-16]. https://www.nist.gov/publications/zero-trust-architecture. |
| [8] | 中国通信标准化协会. 零信任安全技术参考框架[EB/OL]. (2024- 04-01)[2026-02-16]. https://openstd.samr.gov.cn/bzgk/std/newGbInfo?hcno=C166002FE253A840E56BEBF13B4945E7. |
| [9] |
吴倩琳, 孔松. 零信任发展与应用研究[J]. 信息通信技术与政策, 2025, 51(1): 46-51.
doi: 10.12267/j.issn.2096-5931.2025.01.007 |
| [10] | 刘凌旗, 谢佳琦. 美国零信任发展及其国防领域布局研究[J]. 战术导弹技术, 2025(1): 26-32. |
| [11] | Moubayed A, Refaey A, Shami A. Software-defined perimeter (SDP): state of the art secure solution for modern networks[J]. IEEE Network, 2019, 33(5): 226-233. |
| [12] | 刘远, 孙晨, 张嫣玲. 基于Overlay技术的零信任网络研究[J]. 信息网络安全, 2020, 20(10): 83-91. |
| [13] | 蔡东赟. 腾讯iOA零信任安全技术实践[J]. 信息安全与通信保密, 2020(S1): 98-102. |
| [14] | Bonneau J, Herley C, Van O P C, et al. The quest to replace passwords: a framework for comparative evaluation of web authentication schemes[C]// 2012 IEEE Symposium on Security and Privacy. New York: IEEE, 2012: 553-567. |
| [15] | Mahmoud M, Kasem M S, Kang H S. A comprehensive survey of masked faces: recognition, detection, and unmasking[J]. Applied Sciences, 2024, 14(19): 8781-8818. |
| [16] | Carrillo-Torres D, Perez-Diaz J A, Cantoral-Ceballos J A, et al. A novel multi-factor authentication algorithm based on image recognition and user established relations[J]. Applied Sciences, 2023, 13(3): 1374-1389. |
| [17] | Otta S P, Panda S, Gupta M, et al. A systematic survey of multi-factor authentication for cloud infrastructure[J]. Future Internet, 2023, 15(4): 146-166. |
| [18] | Bissada A, Olmsted A. Mobile multi-factor authentication[C]// 2017 12th International Conference for Internet Technology and Secured Transactions (ICITST). New York: IEEE, 2017: 210-211. |
| [19] | Aldarwish A J Y, Yassin A A, Rashid A M, et al. Multi-factor authentication for an administrator’s devices in an IoT environment[C]// International Conference on Advances in Cyber Security (ACeS 2020). Heidelberg: Springer, 2021: 27-47. |
| [20] | Hayashi E, Das S, Amini S, et al. CASA: context-aware scalable authentication[EB/OL]. (2013-07-24)[2026-02-16]. https://m.booksci.cn/literature/123151081.htm. |
| [21] | Buthpitiya S, Zhang Ying, Dey A K, et al. N-gram geo-trace modeling[C]// The 9th International Conference on Pervasive Computing. Heidelberg: Springer, 2011: 97-114. |
| [22] | Jakobsson M, Shi E, Golle P, et al. Implicit authentication for mobile devices[EB/OL]. (2009-02-25)[2026-02-16]. https://www.usenix.org/legacy/event/hotsec09/tech/full_papers/jakobsson.pdf. |
| [23] | Benzekki K, El F A, Elbelrhiti E A. A context-aware authentication system for mobile cloud computing[J]. Procedia Computer Science, 2018(127): 379-387. |
| [24] | Frank M, Biedert R, Ma E, et al. Touchalytics: on the applicability of touchscreen input as a behavioral biometric for continuous authentication[J]. IEEE Transactions on Information Forensics and Security, 2013, 8(1): 136-148. |
| [25] | Nickel C, Busch C, Rangarajan S, et al. Using hidden markov models for accelerometer-based biometric gait recognition[C]// 2011 IEEE 7th International Colloquium on Signal Processing and its Applications. New York: IEEE, 2011: 58-63. |
| [26] | Saevanee H, Clarke N, Furnell S, et al. Continuous user authentication using multi-modal biometrics[J]. Computers & Security, 2015(53): 234-246. |
| [27] | Roth J, Liu Xiaoming, Metaxas D. On continuous user authentication via typing behavior[J]. IEEE Transactions on Image Processing, 2014, 23(10): 4611-4624. |
| [28] | Syed N F, Shah S W, Shaghaghi A, et al. Zero trust architecture (ZTA): a comprehensive survey[J]. IEEE Access, 2022(10): 57143-57179. |
| [29] | Bijon K Z, Krishnan R, Sandhu R. A framework for risk-aware role based access control[C]// 2013 IEEE Conference on Communications and Network Security (CNS). New York: IEEE, 2013: 462-469. |
| [30] | Premkamal P K, Pasupuleti S K, Singh A K, et al. Enhanced attribute based access control with secure deduplication for big data storage in cloud[J]. Peer-to-Peer Networking and Applications, 2021, 14(1): 102-120. |
| [31] | Wang Haichao, Ren Zhiyu, Zhang Tianpeng, et al. A distributed ABAC access control scheme based on blockchain[C]// 2022 2nd International Conference on Computer Science and Blockchain (CCSB). New York: IEEE, 2022: 19-25. |
| [32] | Rouhani S, Deters R. Blockchain based access control systems: state of the art and challenges[C]// IEEE/WIC/ACM International Conference on Web Intelligence. New York: ACM, 2019: 423-428. |
| [33] | Albrecht M, Chase M, Chen Hao, et al. Homomorphic encryption standard[EB/OL]. (2022-01-04)[2026-02-16]. https://link.springer.com/chapter/10.1007/978-3-030-77287-1_2. |
| [34] | Zhao Chuan, Zhao Shengnan, Zhao Minghao, et al. Secure multi-party computation: theory, practice and applications[J]. Information Sciences, 2019(476): 357-372. |
| [35] | Turan M S, Mckay K A, Calik C, et al. Status report on the first round of the NIST lightweight cryptography standardization process[EB/OL]. (2019-10-07)[2026-02-16]. https://csrc.nist.rip/publications/detail/nistir/8268/final. |
| [36] | Lo O, Buchanan W J, Carson D. Power analysis attacks on the AES-128 S-box using differential power analysis (DPA) and correlation power analysis (CPA)[J]. Journal of Cyber Security Technology, 2017, 1(2): 88-107. |
| [37] | Bogdanov A, Knudsen L R, Leander G, et al. PRESENT: an ultra-lightweight block cipher[C]// Cryptographic Hardware and Embedded Systems-CHES 2007: The 9th International Workshop. Heidelberg: Springer, 2007: 450-466. |
| [38] | Indrajati D, Ashari W M. Evaluation of the effectiveness of lightweight encryption algorithms on data performance and security on IoT devices[J]. Journal of Applied Informatics and Computing, 2025, 9(3): 642-650. |
| [39] | Buchanan W J, Li Shancang, Asif R. Lightweight cryptography methods[J]. Journal of Cyber Security Technology, 2017, 1(3): 187-201. |
| [40] | Basta N, Ikram M, Ali K M, et al. Towards a zero-trust micro-segmentation network security strategy: an evaluation framework[C]// NOMS 2022-2022 IEEE/IFIP Network Operations and Management Symposium. New York: IEEE, 2022: 1-7. |
| [41] | Liu Chunwen, Tan Ru, Wu Yang, et al. Dissecting zero trust: research landscape and its implementation in IoT[EB/OL]. (2024-05-03)[2026-02-16]. https://link.springer.com/article/10.1186/s42400-024-00212-0. |
| [42] | Vanickis R, Jacob P, Dehghanzadeh S, et al. Access control policy enforcement for zero-trust-networking[C]// 2018 29th Irish Signals and Systems Conference (ISSC). New York: IEEE, 2018: 1-6. |
| [43] | Klein D. Micro-segmentation: securing complex cloud environments[J]. Network Security, 2019(3): 6-10. |
| [44] | NetFoundry. OpenZiti documentation[EB/OL]. (2025-06-16)[2026-02-16]. https://openziti.io/docs/learn/introduction/. |
| [45] | Cisco. Application centric infrastructure[EB/OL]. (2024-04-16)[2026-02-16]. https://www.cisco.com/c/en_au/solutions/data-centervirtualization/application-centric-infrastructure/index.html. |
| [46] | VMware. VMware NSX[EB/OL]. (2025-03-13)[2026-02-16]. https://www.vmware.com/products/cloud-infrastructure/nsx. |
| [47] | Pace M. Zero trust networks with istio[D]. Torino: Politecnico di Torino, 2021. |
| [48] | Kovacevic I, Stojkov M, Simic M. Authentication and identity management based on zero trust security model in micro-cloud environment[C]//International Conference on Intelligent Science and Technology 2023. Heidelberg: Springer, 2024: 481-489. |
| [49] | Arora S, Hastings J. Microsegmented cloud network architecture using open-source tools for a zero trust foundation[C]//2024 17th International Conference on Security of Information and Networks (SIN). New York: IEEE, 2024: 1-8. |
| [50] | Shakya S, Abbas R, Maric S. A novel zero-touch, zero-trust, AI/ML enablement framework for IoT network security[EB/OL]. (2025-02-05)[2026-02-16]. https://papers.cool/arxiv/2502.03614. |
| [51] | 吴克河, 程瑞, 姜啸晨, 等. 基于SDP的电力物联网安全防护方案[J]. 信息网络安全, 2022, 22(2):32-38. |
| [52] | Huang Wenhua, Xie Xuemin, Wang Ziying, et al. ZT-access: a combining zero trust access control with attribute-based encryption scheme against compromised devices in power IoT environments[EB/OL]. (2023-06-01)[2026-02-16]. https://doi.org/10.1016/j.adhoc.2023.103161. |
| [53] | Alipour M A, Ghasemshirazi S, Shirvani G. Enabling a zero trust architecture in a 5G-enabled smart grid[EB/OL]. (2022-10-21)[2026-02-16]. https://arxiv.org/abs/2210.01739. |
| [54] | 陈岑, 屈志昊, 汪明, 等. 面向电网安全的零信任动态访问控制[J]. 重庆大学学报, 2024, 47(8): 81-89. |
| [55] | Allouzi M A, Khan J. Enabling zero trust security in IoMT edge network[EB/OL]. (2024-02-16)[2026-02-16]. https://arxiv.org/abs/2402.10389. |
| [56] | Xie Mingyue, Chang Zheng, Alfarraj O, et al. BAZAM: a blockchain-assisted zero-trust authentication in multi-UAV wireless networks[EB/OL]. (2024-06-30)[2026-02-16]. https://arxiv.org/abs/2407.00630. |
| [57] | Chang Y C, Lin Yushan, Sangaiahc A K, et al. A private blockchain system based on zero trust architecture[C]// 2024 26th International Conference on Advanced Communications Technology (ICACT). New York: IEEE, 2024: 143-146. |
| [58] | Cheng Tongtong, Chi Cheng, Zhang Yuwen, et al. The appliance of decentralized identifiers in zero trust network[C]// 2023 IEEE International Conference on Blockchain. New York: IEEE, 2023: 198-202. |
| [59] | Sun Sheng, Repeta M, Healy M, et al. Towards 5G zero trusted air interface architecture[EB/OL]. (2022-11-07)[2026-02-16]. https://arxiv.org/abs/2211.03776. |
| [60] | Hatakeyama K, Kotani D, Okabe Y. Zero trust federation: sharing context under user control towards zero trust in identity federation[C]// 2021 IEEE International Conference on Pervasive Computing and Communications Workshops and Other Affiliated Events (PerCom Workshops). New York: IEEE, 2021: 514-519. |
| [61] | Haque E, Hasan K, Ahmed I, et al. Enhancing UAV security through zero trust architecture: an advanced deep learning and explainable AI analysis[C]// 2024 International Conference on Computing, Networking and Communications (ICNC). New York: IEEE, 2024: 463-467. |
| [62] | Cheng Ruizhi, Chen Songqing, Han Bo. Toward zero-trust security for the metaverse[J]. IEEE Communications Magazine, 2024, 62(2): 156-162. |
| [63] | 张伟, 李子轩, 徐晓瑀, 等. SDP-CoAP:基于软件定义边界的安全增强CoAP通信框架设计[J]. 信息网络安全, 2023, 23(8):17-31. |
| [64] | 黄杰, 何城鋆. 基于软件定义边界的服务保护方案[J]. 信息网络安全, 2023, 23(6):1-10. |
| [65] | 郭宝霞, 王佳慧, 马利民, 等. 基于零信任的敏感数据动态访问控制模型研究[J]. 信息网络安全, 2022, 22(6):86-93. |
| [1] | LIU Qin, WANG Zhuobing, YU Chunwu, WANG Zhangyi. Efficient Attribute-Based Encryption Scheme from Lattices for Cloud Security [J]. Netinfo Security, 2023, 23(9): 25-36. |
| [2] | ZHANG Wei, LI Zixuan, XU Xiaoyu, HUANG Haiping. SDP-CoAP: Design of Security Enhanced CoAP Communication Framework Based on Software Defined Perimeter [J]. Netinfo Security, 2023, 23(8): 17-31. |
| [3] | HUANG Jie, HE Chengjun. Service Protection Scheme Based on Software Defined Perimeter [J]. Netinfo Security, 2023, 23(6): 1-10. |
| [4] | GUO Baoxia, WANG Jiahui, MA Limin, ZHANG Wei. Research on Dynamic Access Control Model of Sensitive Data Based on Zero Trust [J]. Netinfo Security, 2022, 22(6): 86-93. |
| [5] | WU Yunkun, JIANG Bo, PAN Ruixuan, LIU Yuling. A SDN Access Control Mechanism Based on Zero Trust [J]. Netinfo Security, 2020, 20(8): 37-46. |
| [6] | LIU Yuan, SUN Chen, ZHANG Yanling. A Zero Trust Network Research Based on Overlay Technology [J]. Netinfo Security, 2020, 20(10): 83-91. |
| Viewed | ||||||
|
Full text |
|
|||||
|
Abstract |
|
|||||