信息网络安全 ›› 2026, Vol. 26 ›› Issue (8): 1224-1236.doi: 10.3969/j.issn.1671-1122.2026.08.005
抗APT窃密的工业互联网跨域协同零信任模型
冯景瑜, 尹静怡( ), 张森勇, 李静慧
西安邮电大学无线网络安全技术国家工程研究中心 西安 710121
-
收稿日期:2026-01-15出版日期:2026-08-10发布日期:2026-09-23 -
通讯作者:尹静怡 E-mail:203936711@qq.com -
作者简介:冯景瑜(1984—),男,甘肃,教授,博士,CCF会员,主要研究方向为物联网安全、区块链、网络防御|尹静怡(2001—),女,甘肃,硕士研究生,主要研究方向为工业互联网安全|张森勇(2002—),男,河南,硕士研究生,主要研究方向为漏洞检测|李静慧(2002—),女,河南,硕士研究生,主要研究方向为物联网安全 -
基金资助:国家自然科学基金(62572392);陕西省重点研发计划(2024GX-YBXM-076)
Cross-domain collaborative zero-trust model for industrial Internet to counter APT data theft
Feng Jingyu, Yin Jingyi(), Zhang Senyong, Li Jinghui
National Engineering Research Center for Wireless Security ,Xi’an University of Posts and Telecommunications Xi’an 710121, China
-
Received:2026-01-15Online:2026-08-10Published:2026-09-23 -
Contact:Yin Jingyi E-mail:203936711@qq.com

摘要:
随着信息技术和工控系统的融合日益紧密,高级持续性威胁(APT)对工业互联网造成的敏感数据泄露问题愈发严重。然而,现有APT窃密防御技术主要集中在工业互联网信息技术(IT)域,忽视了突破IT域侧防护后渗透进运营技术(OT)域的APT窃密跨域威胁。针对这一挑战,文章提出一种抗APT窃密的工业互联网跨域协同零信任模型。首先,设计跨域协同的软件定义边界(SDP)零信任组件部署方案,对IT域和OT域的行为数据进行同步关注,避免因单域数据缺失导致的威胁漏判,并对行为数据进行归一化特征处理,构建差异化动态信任评估模型;然后,引入BiLSTM-MultiHead Attention模型捕捉APT跨域行为时序依赖关系,构建突变因子预测方案,实现对失陷终端行为的快速响应和信任值动态调节。在此基础上,设计跨域协同决策与失陷判别算法,对失陷终端进行判别和及时阻断。实验结果表明,文章所提模型在CMU-CERT数据集上对APT窃密跨域威胁表现出较好的协同防御性能,突变因子预测精确率达99.81%,实现对失陷终端的有效识别。
中图分类号:
引用本文
冯景瑜, 尹静怡, 张森勇, 李静慧. 抗APT窃密的工业互联网跨域协同零信任模型[J]. 信息网络安全, 2026, 26(8): 1224-1236.
Feng Jingyu, Yin Jingyi, Zhang Senyong, Li Jinghui. Cross-domain collaborative zero-trust model for industrial Internet to counter APT data theft[J]. Netinfo Security, 2026, 26(8): 1224-1236.
表1
本文模型与相关工作的对比
| 模型 | 零信任引入 | 信任评估 | 突发行为阻断 | 跨域防御 |
|---|---|---|---|---|
| 文献[ | 不支持 | 不支持 | 不支持 | 支持 |
| 文献[ | 不支持 | 动态 | 不支持 | 不支持 |
| 文献[ | 支持 | 不支持 | 不支持 | 不支持 |
| 文献[ | 支持 | 支持 | 不支持 | 不支持 |
| 文献[ | 支持 | 动态 | 及时阻断 | 不支持 |
| 本文模型 | 支持 | 动态 | 及时阻断 | 支持 |
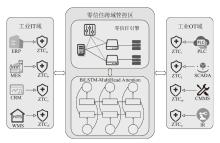
图1
跨域协同零信任模型架构
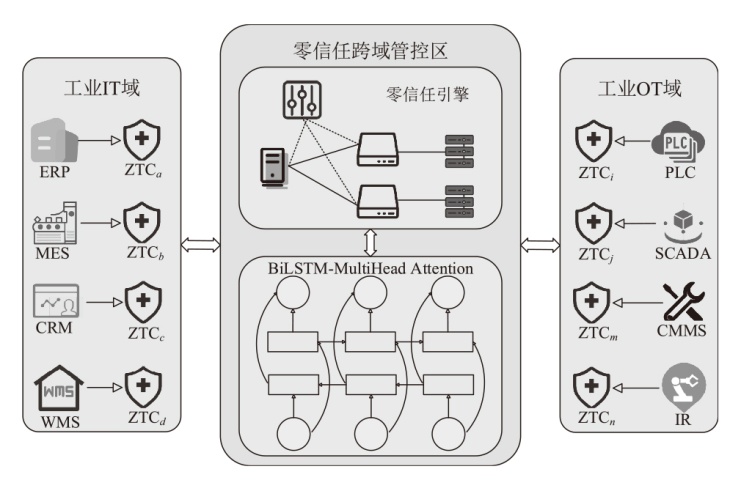
图2
抗APT窃密的跨域协同SDP零信任组件架构
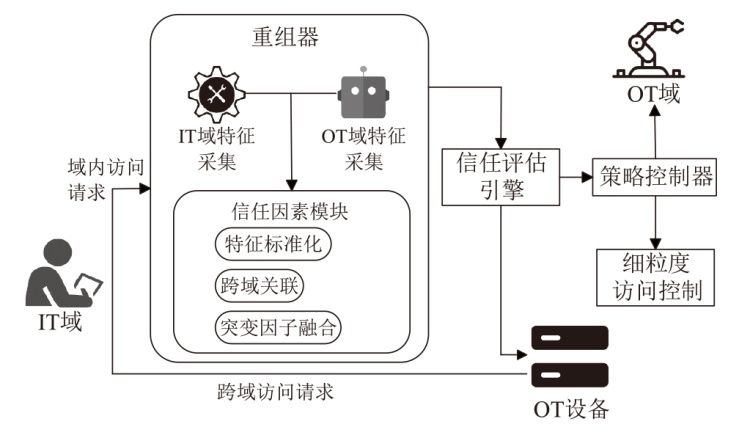
图3
BiLSTM-MultiHead Attention模型结构
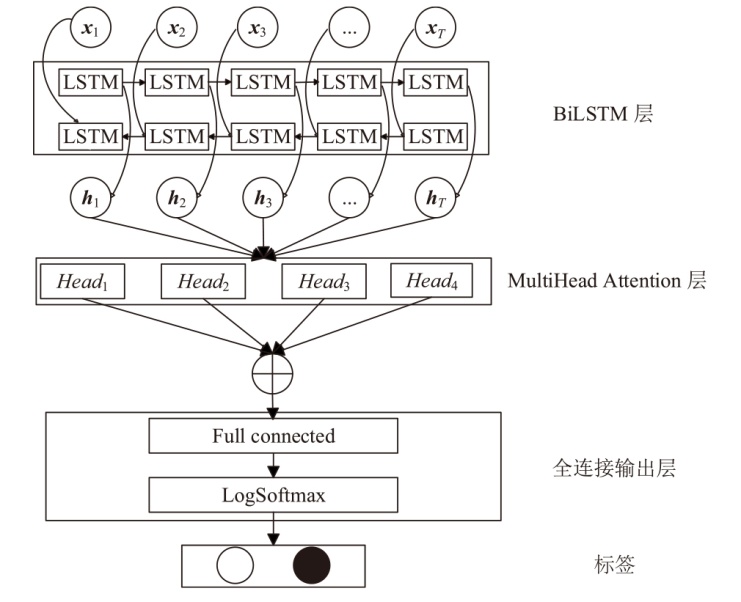
表2
实验仿真环境配置
| 实验环境 | 环境配置 |
|---|---|
| 操作系统 | Windows 10 操作系统 |
| 系统类型 | 64位操作系统 |
| CPU | Intel® Core(TM) Ultra 9 CPU @2.90 GHz |
| 内存大小 | 32.00 GB |
| 开发环境 | PyCharm |
| 深度学习框架 | PyTorch |
| 编程语言 | Python 3.9 |
| 依赖库 | numpy、matplotlib、pandas、Polars等 |
表3
实验参数设置
| 参数 | 描述 | 预设值 |
|---|---|---|
| T | 仿真轮数 | 60 |
| N | 工业互联网终端数 | 1000 |
| M | 失陷终端比例 | 30% |
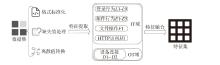
图4
数据预处理流程
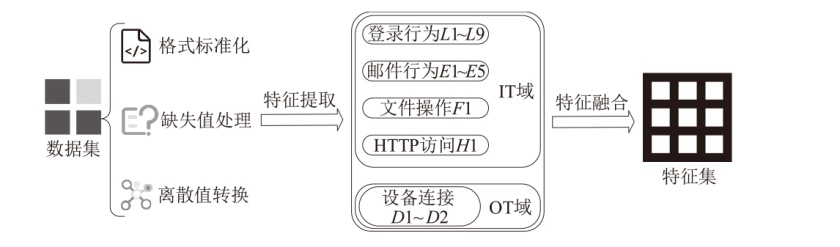
表4
18维特征集
| 特征类别 | 特征 |
|---|---|
| Logon特征 | 首次登录与工作起始时间(8:00)的差值 |
| 末次登录与工作起始时间的差值 | |
| 下班后登录时间相对8:00的平均偏移 | |
| 下班后登录时间相对19:00的平均偏移 | |
| 下班后(19:00后)登录次数 | |
| 每日访问的终端数量 | |
| 下班后访问的终端数量 | |
| 下班后会话时长总和 | |
| Email特征 | 外部收件人数量 |
| 保留占位特征 | |
| 未使用附件总数 | |
| 平均邮件大小占比 | |
| 总收件人数量 | |
| HTTP特征 | 统计访问敏感站点的次数 |
| File特征 | 每日.exe文件操作次数 |
| Device特征 | 下班后设备连接次数 |
| 每日设备总连接次数 |
表5
分类器评估分析结果
| 模型 | AUC | P | R | F1 |
|---|---|---|---|---|
| RNN | 84.29% | 88.51% | 84.29% | 84.18% |
| LSTM | 90.97% | 92.68% | 90.97% | 91.08% |
| Transformer | 96.19% | 96.55% | 96.10% | 96.18% |
| BiLSTM-MultiHead Attention | 99.79% | 99.81% | 99.79% | 99.80% |
表6
APT检测模型评估分析结果
| 模型 | AUC | P | R | F1 |
|---|---|---|---|---|
| DTITD[ | 99.72% | 100% | 90.00% | 94.74% |
| TTT-ECA-ResNet[ | 98.75% | 95.57% | 97.04% | 96.81% |
| 本文模型 | 99.79% | 99.81% | 99.79% | 99.80% |
表7
IT域惩罚因子敏感性
| IT域首次告警轮次 | 相对基线变化/轮 | 第31轮IT域信任值 | |
|---|---|---|---|
| 1.5 | 第39轮 | +2 | 0.8354 |
| 2.0 | 第38轮 | +1 | 0.8285 |
| 2.5 | 第37轮 | — | 0.8216 |
| 3.0 | 第37轮 | 0 | 0.8148 |
表8
OT域惩罚因子敏感性
| OT域首次告警轮次 | 相对基线变化/轮 | 第31轮OT域信任值 | |
|---|---|---|---|
| 1.5 | 第55轮 | — | 0.8960 |
| 2.0 | 第52轮 | -3 | 0.8986 |
| 2.5 | 第50轮 | -5 | 0.9012 |
图5
IT域威胁检测曲线
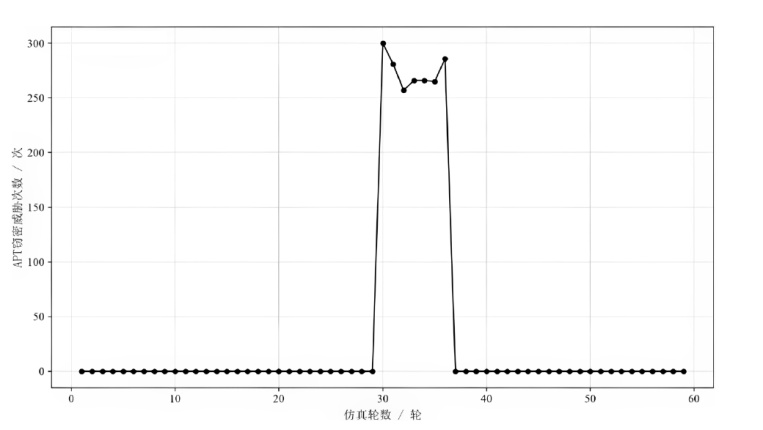
图6
OT域威胁检测曲线
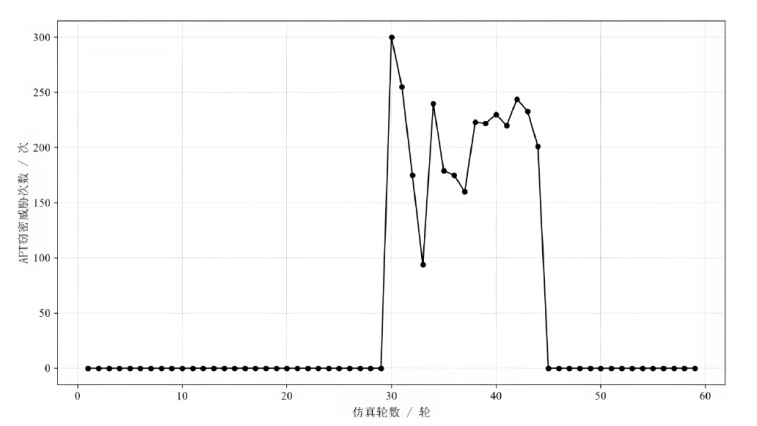
图7
综合威胁检测曲线
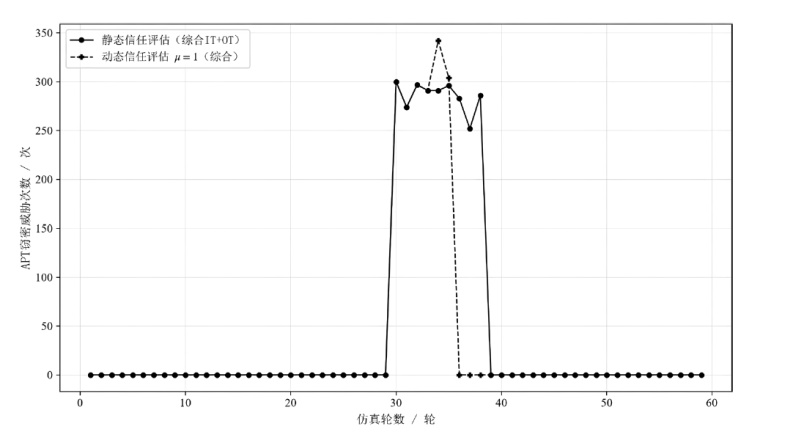
表9
跨域与单域对比分析
| 检测模式 | 配置说明 | 检测 灵敏度 | 威胁持续时间 | 误报风险 | 适用场景 |
|---|---|---|---|---|---|
| 单域 (仅IT) | 仅用IT域信任值 | 高 | 短 | 中 | 纯IT环境 |
| 单域 (仅OT) | 仅用OT域信任值 | 中 | 长 | 高 | 纯OT环境 |
| 跨域 (IT+OT) | 高且稳定 | 适中 | 低 | 工业互联网 |
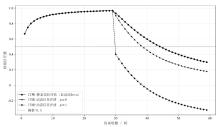
图8
IT域终端信任值变化曲线
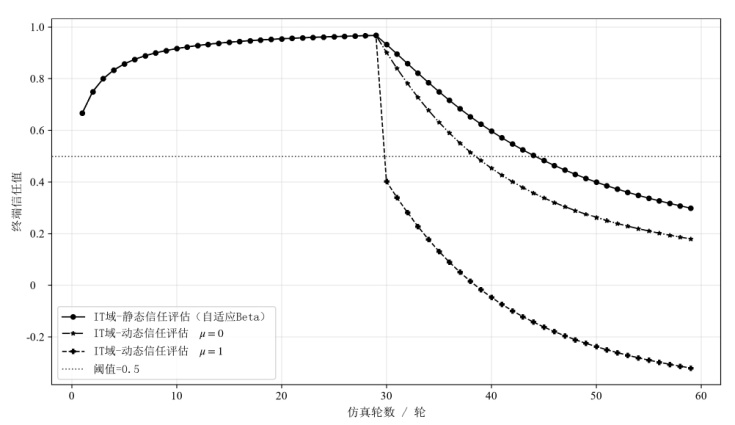
图9
OT域终端信任值变化曲线
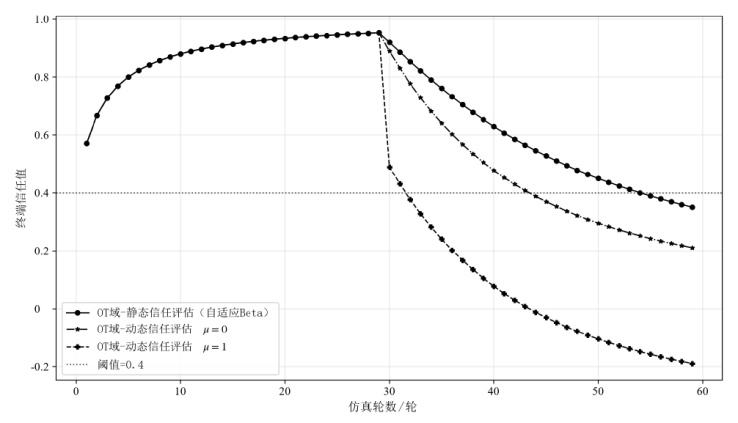
图10
IT域失陷终端检测率变化曲线
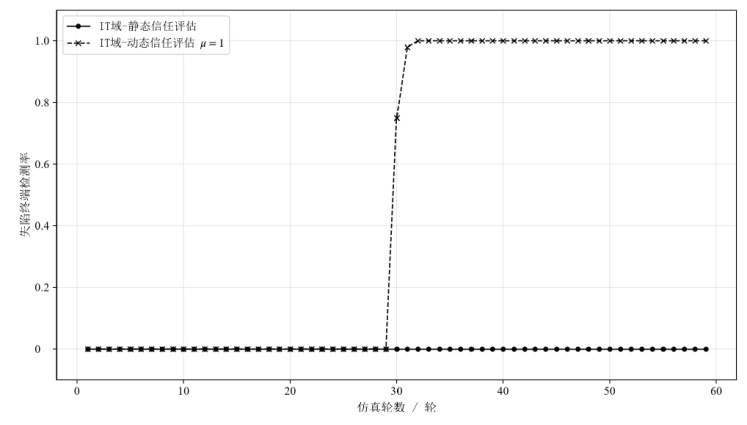
图11
OT域失陷终端检测率变化曲线
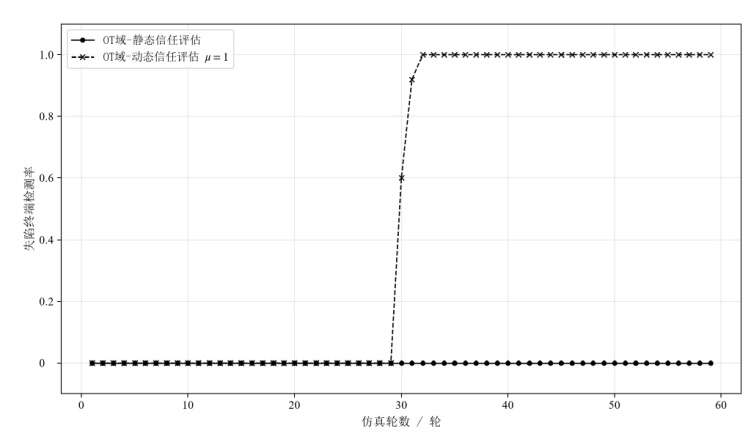
图12
综合失陷终端检测率变化曲线
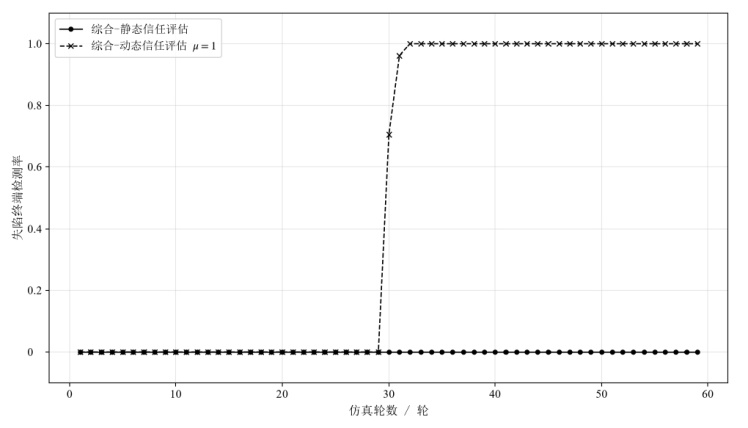
图13
IT域APT窃密阻断成功率

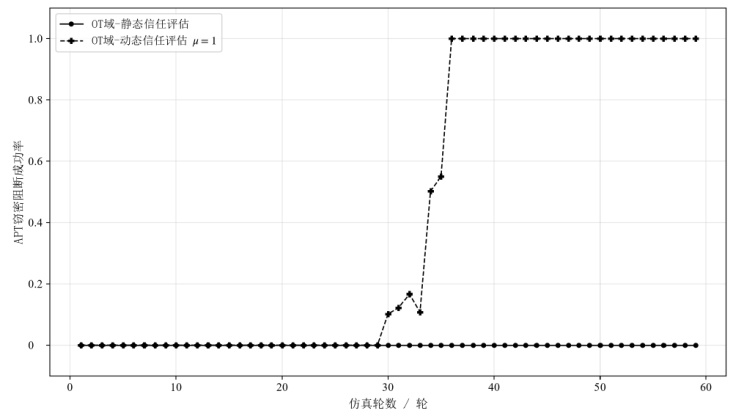
图14
OT域APT窃密阻断成功率
| [1] | 王灏楠. 工业物联网网关系统设计与实现[D]. 天津: 天津大学, 2020. |
| [2] | 祝剑, 杨珍娜, 庞龙, 等. 基于区块链的工业互联网数据溯源方案[J]. 西安邮电大学学报, 2022, 27(2):102-110. |
| [3] | Shi Yuanquan, Li Wei, Zhang Yu, et al. Survey on APT attack detection in industrial cyber-physical system[C]// 2021 International Conference on Electronic Information Technology and Smart Agriculture(ICEITSA). New York: IEEE, 2021: 296-301. |
| [4] | Brown T. The rising threat of cyberattacks on industrial systems[J]. Global Security Journal, 2022, 8(4): 120-135. |
| [5] | 赵新强, 范博, 张东举. 基于威胁发现的APT攻击防御体系研究[J]. 信息网络安全, 2024, 24(7):1122-1128. |
| [6] | Kumar A, Thing V L L. RAPTOR: advanced persistent threat detection in industrial IoT via attack stage correlation[C]// The 20th Annual International Conference on Privacy, Security and Trust (PST). New York: IEEE, 2023: 1-12. |
| [7] | Liu Han, An Baoyu, Yin Yaoyao, et al. A trust evaluation and concept drift-based approach for dynamic APT evasion detection[C]// 2024 IEEE Cyber Science and Technology Congress (CyberSciTech). New York: IEEE, 2024: 544-547. |
| [8] | 邢方圆, 董傲, 孙羽羿, 等. 面向大规模物联网的零信任管理研究综述[J]. 电子学报, 2025, 53(8):2993-3025. |
| [9] | Rose S, Borchert O, Mitchell S, et al. Zero trust architecture: NIST Special Publication 800-207[R]. 2020-08: 1-59. |
| [10] | Fernandez E B, Brazhuk A. A critical analysis of zero trust architecture (ZTA)[EB/OL]. (2024-01-09)[2026-01-04]. https://doi.org/10.1016/j.csi.2024.103832. |
| [11] | Smiliotopoulos C, Kambourakis G, Kolias C. Detecting lateral movement: a systematic survey[EB/OL]. (2024-02-15)[2026-01-04]. https://doi.org/10.1016/j.heliyon.2024.e26317. |
| [12] | Khule M, Motwani D, Chauhan D. Adaptive threat intelligence: an incremental learning approach for detecting evolving APT attacks[C]// International Conference on Advances in Modern Age Technologies for Health and Engineering Science (AMATHE). New York: IEEE, 2025: 1-6. |
| [13] | Zhang Xiaojian, Chen Liandong, FAN Jie, et al. Power IoT security protection architecture based on zero trust framework[C]// The 5th International Conference on Cryptography, Security and Privacy (CSP). New York: IEEE, 2021: 166-170. |
| [14] | 吴克河, 程瑞, 姜啸晨, 等. 基于SDP的电力物联网安全防护方案[J]. 信息网络安全, 2022, 22(2):32-38. |
| [15] | 陈长松. 零信任架构下的数据安全纵深防御体系研究[J]. 信息网络安全, 2021, 21(S1):105-108. |
| [16] | 袁忠, 王勇, 张成. 零信任SDP技术在云桌面系统中的研究与应用[J]. 网络安全技术与应用, 2025, 25(10):82-86. |
| [17] | 马宁. 工业过程控制中的PLC与SCADA系统集成优化[J]. 自动化应用, 2023, 64(21):54-56. |
| [18] | 黄杰, 何城鋆. 基于软件定义边界的服务保护方案[J]. 信息网络安全, 2023, 23(6):1-10. |
| [19] | 许盛伟, 田宇, 邓烨, 等. 基于零信任的大规模车联网安全模型研究[J]. 物联网技术, 2023, 13(10):80-82. |
| [20] | 夏凡, 马骏文, 薛虎虎, 等. 基于多模型融合深度学习算法的文本情感分析模型[J]. 西安邮电大学学报, 2025, 30(5):85-91. |
| [21] | Chen Genwen, Zhou Qingfei, Huang Jie, et al. A multidimensional trust assessment method for zero trust dynamic access control[C]// The 40th Youth Academic Annual Conference of Chinese Association of Automation (YAC). New York: IEEE, 2025: 3170-3176. |
| [22] | 冯景瑜, 王锦康, 张宝军, 等. 基于信任过滤的轻量级加密流量异常检测方案[J]. 西安邮电大学学报, 2023, 28(5):56-66. |
| [23] | Glasser J, Lindauer B. Bridging the gap: a pragmatic approach to generating insider threat data[C]// IEEE Security and Privacy Workshops. New York: IEEE, 2013: 98-104. |
| [24] | Wang Zhiqiang, El S A. DTITD: an intelligent insider threat detection framework based on digital twin and self-attention based deep learning models[J]. IEEE Access, 2023, 11: 114013-114030. |
| [25] | Tao Xiaoling, Liu Jianxiang, Yu Yuelin, et al. An insider threat detection method based on improved test-time training model[EB/OL]. (2025-01-14)[2026-01-04]. https://www.sciencedirect.com/science/article/pii/S2667295224000862. |
| [1] | 马如坡, 王群, 尹强, 高谷刚. Modbus TCP协议安全风险分析及对策研究[J]. 信息网络安全, 2024, 24(11): 1710-1720. |
| [2] | 沈也明, 李贝贝, 刘晓洁, 欧阳远凯. 基于主动学习的工业互联网入侵检测研究[J]. 信息网络安全, 2021, 21(1): 80-87. |
| [3] | 余果, 王冲华, 陈雪鸿, 李俊. 认证视角下的工业互联网标识解析安全[J]. 信息网络安全, 2020, 20(9): 77-81. |
| [4] | 王冲华, 李俊, 陈雪鸿. 工业互联网平台安全防护体系研究[J]. 信息网络安全, 2019, 19(9): 6-10. |
| 阅读次数 | ||||||
|
全文 |
|
|||||
|
摘要 |
|
|||||