信息网络安全 ›› 2026, Vol. 26 ›› Issue (9): 1408-1421.doi: 10.3969/j.issn.1671-1122.2026.09.007
一种支持策略即代码与跨部门协同的数据安全治理框架
王方圆1, 练智超1,2( ), 李千目1, 金红3
- 1
南京理工大学网络空间安全学院 南京 210094
2中国科学院大学南京学院 南京 211135
3恒安嘉新(北京)科技股份公司 北京 100086
-
收稿日期:2025-11-24出版日期:2026-09-10发布日期:2026-09-30 -
通讯作者:练智超 E-mail:newlzcts@njust.edu.cn -
作者简介:王方圆(1985—),男,江苏,高级工程师,博士研究生,主要研究方向为大模型网络安全、人工智能|练智超(1983—),男,安徽,教授,博士,CCF会员,主要研究方向为图像处理与模式识别|李千目(1979—),男,安徽,教授,博士,CCF高级会员,主要研究方向为大模型网络安全、数据安全|金红(1966—),女,北京,高级工程师,硕士,主要研究方向为通信网络安全、数据安全 -
基金资助:国家重点研发计划(2023YFB2704704);江苏省前沿技术研发计划(BF2024071);江苏省科技厅重点研发计划(BE2022081)
A data security governance framework supporting policy-as-code and cross departmental collaboration
Wang Fangyuan1, Lian Zhichao1,2(), Li Qianmu1, Jin Hong3
- 1
School of Cyber Science and Engineering ,Nanjing University of Science and Technology Nanjing 210094, China
2Nanjing College ,University of Chinese Academy of Sciences Nanjing 211135, China
3Heng’an Jiaxin (Beijing) Technology Co. ,Ltd. Beijing 100086, China
-
Received:2025-11-24Online:2026-09-10Published:2026-09-30 -
Contact:Lian Zhichao E-mail:newlzcts@njust.edu.cn

摘要:
针对现代企业数据安全治理过程中存在的资产底数不清、跨部门协同效率低、策略执行滞后等突出问题,文章提出一种数据安全风险协同治理框架CGF-DSR。该框架以数据资产为核心治理对象,构建统一的数据资产与风险视图模型,并基于策略即代码引擎,实现安全与合规策略的自动化执行与动态评估。同时,设计了跨职能协同工作流机制,对数据生命周期中的风险进行闭环管理。实验结果表明,CGF-DSR框架能够有效打通数据、业务、安全与合规部门之间的协作壁垒,显著提升数据风险的识别、处置与审计效率,增强企业在多云环境下的数据安全治理韧性与敏捷性。
中图分类号:
引用本文
王方圆, 练智超, 李千目, 金红. 一种支持策略即代码与跨部门协同的数据安全治理框架[J]. 信息网络安全, 2026, 26(9): 1408-1421.
Wang Fangyuan, Lian Zhichao, Li Qianmu, Jin Hong. A data security governance framework supporting policy-as-code and cross departmental collaboration[J]. Netinfo Security, 2026, 26(9): 1408-1421.
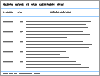
表1
数据安全治理主流方案对比
| 评估维度 | 传统治理框架 | 单点安全 工具 | 协同自动化 平台 | 理想治理框架 需求 |
|---|---|---|---|---|
| 风险识别能力 | 依赖人工 周期性评估 | 场景受限 覆盖不全 | 创建事件响应缺乏预防性 | 持续、自动化 基于内容 |
| 策略执行机制 | 手动实施预后严重 | 分散执行 难以统一 | 部分自动化 依赖集成 | 策略即代码 全自动执行 |
| 跨部门协同支持 | 人工流程高效协作效率低 | 工具期建立长期冲突 | 调度能力提升 | 角色驱动流程更优,可追溯 |
| 治理 敏感性 | 流程细化协同效率低 | 无协同机制各自为政 | 内置工作流 非数据专属 | 角色驱动流程 更优,可追溯 |
| 变更 成本 | 高 | 中 | 中 | 低 |
| 人员管理适应性 | 工周敏捷但 整体较稳定 | 调度快慢 覆盖有限 | 支持动态部署与快速迭代 | 灵活适应人员与流程变化 |
| 应用开发适应性 | 通用开发 | 通用开发 | 通用开发 | 高度适应敏捷与持续交付 |
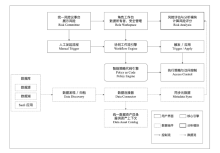
图1
CGF-DSR总体架构
表2
CGF-DSR与传统方案的差异
| 评估维度 | CGF-DSR | 传统GRC平台 | 孤立的安全工具集 |
|---|---|---|---|
| 风险识别 | 持续自动化、基于数据内容 | 周期性、依赖人工 | 场景受限、覆盖不全 |
| 策略执行 | 策略即代码,自动化程度高 | 人工解读,执行滞后 | 策略分散,难以统一管理 |
| 跨部门 协同 | 内置工作流,过程留痕 | 依赖邮件、会议, 效率低下 | 缺乏协同机制 |
| 治理 敏捷性 | 高,适应业务与法规快速变化 | 低,流程僵化,变更成本高 | 中,工具敏捷但整体联动差 |
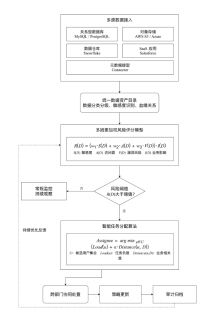
图2
核心算法逻辑与集成应用流程
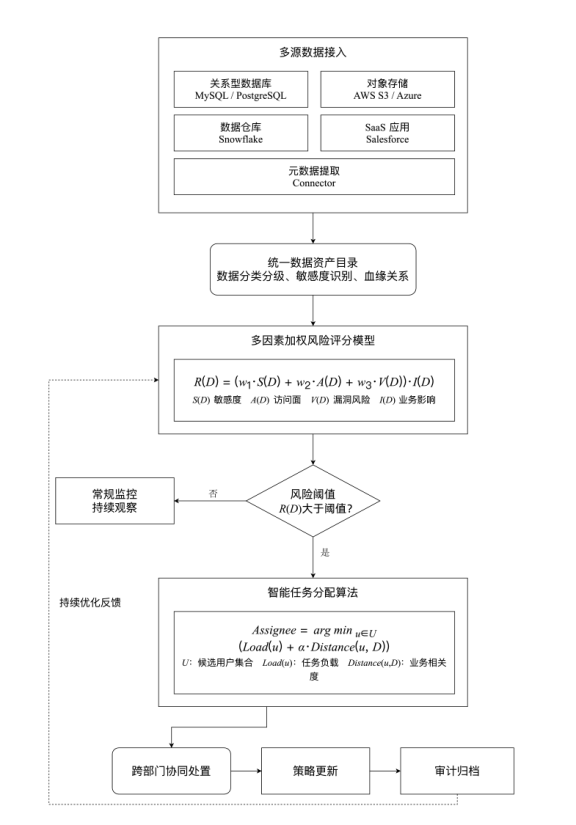
图3
算法应用策略评估与执行流程
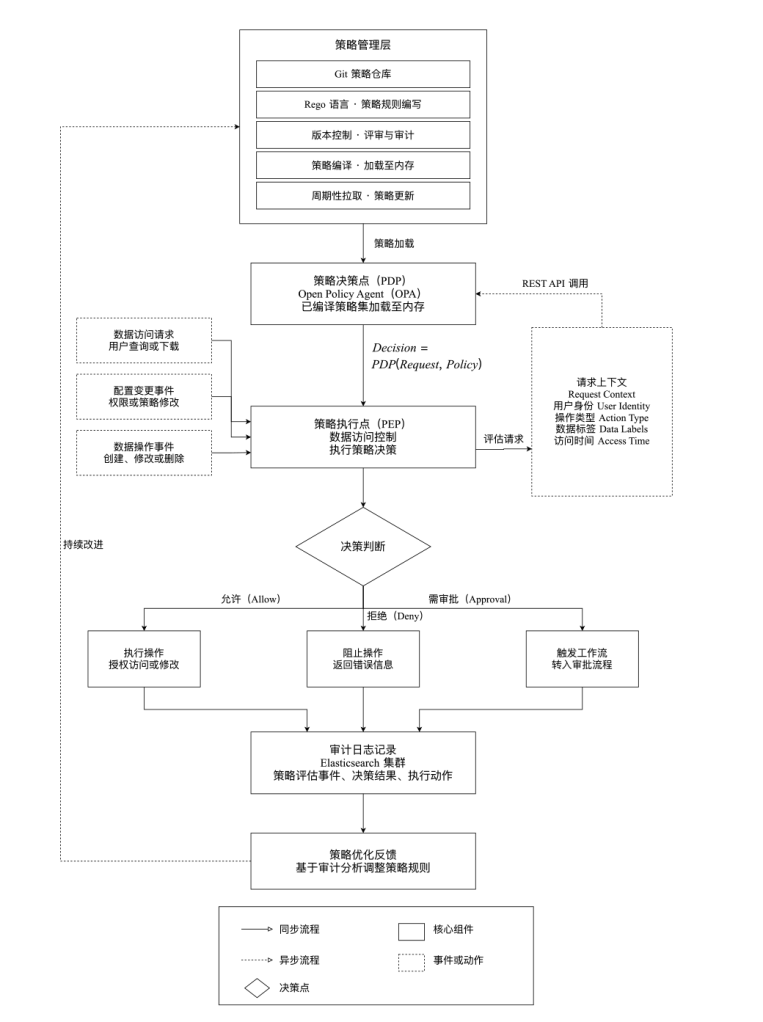
图4
数据服务上线协同审批流程
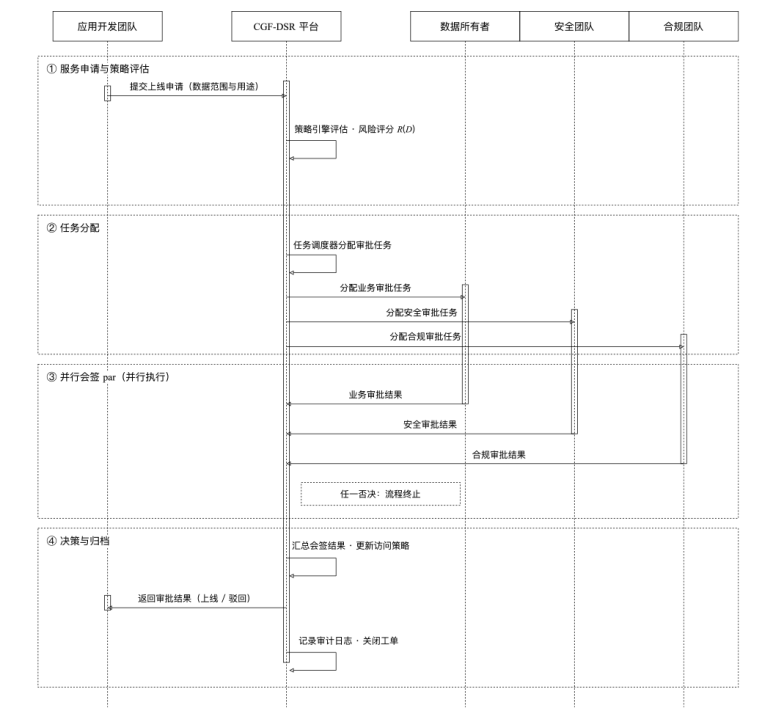
图5
CGF-DSR 系统部署架构
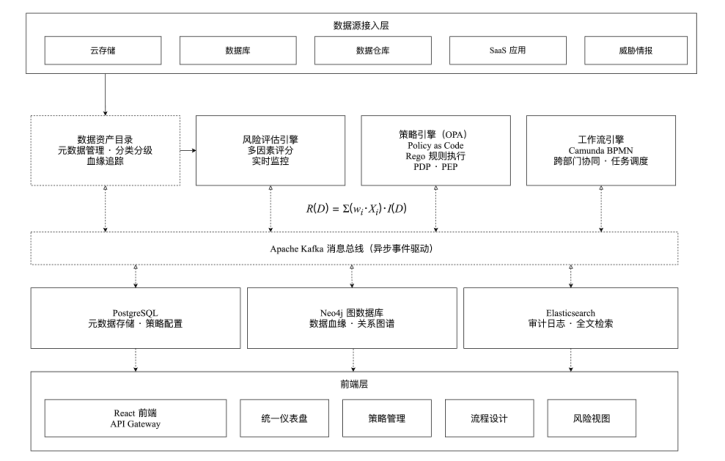
图6
策略即代码执行流程
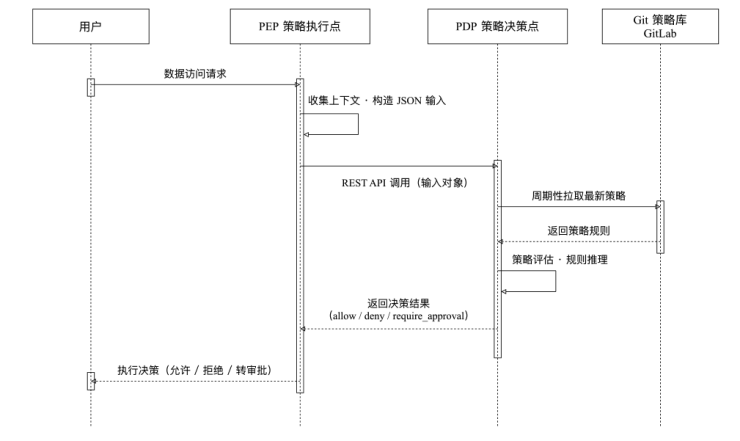
图7
敏感数据外发审批流程
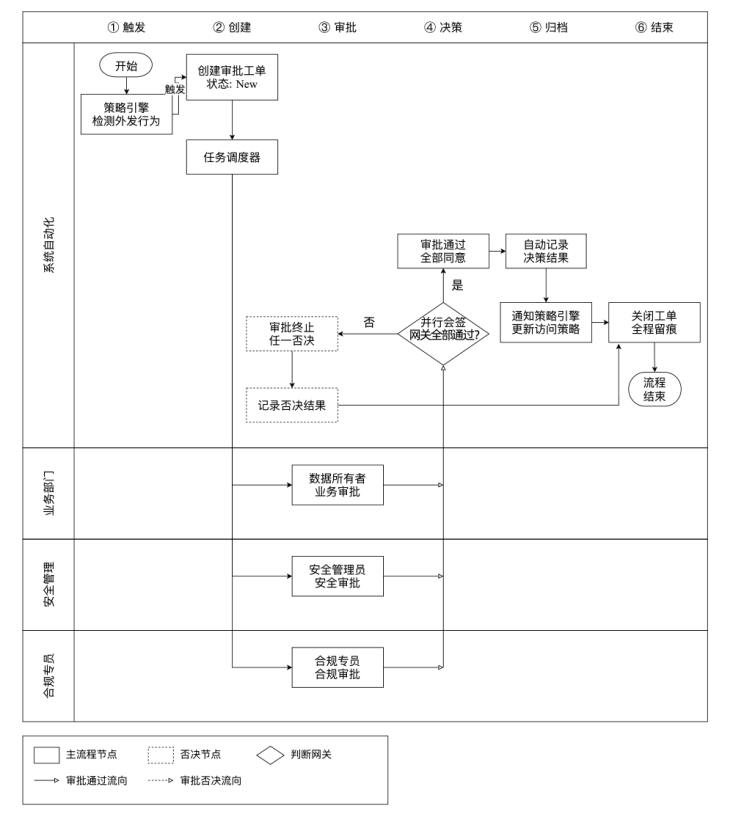
表3
实验环境配置
| 项目类别 | 配置详情 |
|---|---|
| 操作系统 | Ubuntu 22.04 LTS / CentOS 8.4 |
| 开发框架 | Spring Boot 3.0, React 18, Camunda 7.18 |
| 数据库 | PostgreSQL 14, Neo4j 5.8, Elasticsearch 8.6 |
| 消息队列 | Apache Kafka 3.4 |
| 策略引擎 | Open Policy Agent (OPA) v0.50.0 |
| 前端技术 | TypeScript, Ant Design Pro |
| 部署环境 | Kubernetes 1.26, Docker 24.0, Helm 3.12 |
| 硬件配置 | 16 vCPU, 32 GB RAM, 200 GB NVMe SSD |
| 测试工具包 | JMeter 5.5, Postman, GitLab CI/CD, Selenium |
表4
CGF-DSR关键技术指标测评结果
| 测评指标 | 测试场景 | 测试条件 | 结果 (平均值) | 备注 |
|---|---|---|---|---|
| 策略评估延迟 | 单策略规则评估 | 1000次并发 请求 | 12.3ms | 使用OPA引擎,Rego规则复杂度中等 |
| 复杂策略集评估(10条规则) | 500次并发请求 | 45.6ms | 包含多条件组合与数据上下文 | |
| 数据资产扫描 吞吐量 | 全量扫描 (10万张表) | 分布式扫描节点?4 | 85000表/h | 包含元数据提取与敏感数据识别 |
| 增量扫描 (变更数据) | 每5分钟触发 | 950表/min | 仅扫描元数据变更部分 | |
| 工作流响应时间 | 工单创建至分配 | 100工单/s 并发 | 180ms | 包含任务调度与角色匹配 |
| 审批流程完成 时间 | 三角色并行 审批 | 6.8s | 从触发到闭环 | |
| 系统资源占用 | CPU占用率(峰值) | 全量扫描+策略评估并发 | 68% | 16 vCPU环境下 |
| 内存占用 (峰值) | 同时处理1000个策略请求 | 14.2 GB | 总内存32 GB | |
| 策略执行一致性 | 策略命中率 | 模拟10000次数据访问请求 | 99.7% | 误报率小于0.1% |
| 跨云数据同步延迟 | AWS S3 → Azure Blob | 10GB数据同步 | 4.2min | 受网络带宽与加密处理影响 |
表5
风险注入关键参数配置
| 风险类型 | 具体参数 | 取值/配置 | 备注 |
|---|---|---|---|
| 敏感数据 公开暴露 | 暴露比例 | 10%(10000个存储桶/表) | 基于AWS S3 ACL=public-read |
| 异常访问 行为 | 高频阈值 | 10min内大于100条敏感 记录 | 模拟数据爬取器 |
| 异常访问 行为 | 异地IP比例 | 5%请求来自境外IP (GeoIP库标记) | 使用随机生成的境外 IP池 |
| 违规数据 外发 | 外发目标 | 未备案外部邮箱 (@unknown.com ) | 触发DLP策略 |
表6
数据安全治理效果评估指标对比
| 评估指标 | 未使用CGF-DSR(基线) | 使用CGF-DSR | 使用CGF-DSR后提升幅度 |
|---|---|---|---|
| 平均风险暴露时长/h | 18.4 | 2.3 | 下降87.5% |
| 平均审批周期 | 3.2天 | 6.8 s | 下降99.9% |
| 风险检出率 | — | 98% | — |
| 误报率 | — | 小于2% | — |
| [1] |
Qiu Yanrui, Hu Zhimin. Progress and recommendations in data ethics governance: a transnational analysis based on data ethics frameworks[J]. Humanities and Social Sciences Communications, 2025, 12(1): 1354.
doi: 10.1057/s41599-025-05664-4 |
| [2] |
Yan Yixin, Li Daomin, Liu Ziyu, et al. Technology empowerment and responsible governance: optimization path and empirical research on the tripartite game of takeaway platforms[J]. Journal of Business and Marketing, 2025, 2(1): 106-112.
doi: 10.62517/jbm.202509114 URL |
| [3] | 边曼琳, 王利明. 云环境下Docker容器隔离脆弱性分析与研究[J]. 信息网络安全, 2020, 20(7):85-95. |
| [4] | Liu Feimin, Zhu Junjie. Research on the direction and path of government digital reform: based on the “run once at most” reform and government digital transformation in Zhejiang province[J]. Journal of Sociology and Ethnology, 2022, 4(9): 1-11. |
| [5] | 陈烜垒, 邱硕涵, 丁嘉亮, 等. 人工智能产业的国际化路径研究——技术标准、产业落地与协同治理的三重协同机制[J]. 数字化转型, 2025, 2(8):55-62. |
| [6] | 赵一鸣, 李林芯, 罗琳, 等. 国家数据基础设施赋能数据要素价值释放的体制机制研究[J]. 信息资源管理学报, 2025, 3(7):1-13. |
| [7] | 谢波, 李玉菁. 生成式人工智能赋能网络安全治理的基本逻辑与范式重构——基于行动者网络理论的分析[J]. 中国人民公安大学学报(自然科学版), 2025, 31(3):95-104. |
| [8] | 李晗. AIGC背景下虚假信息数据安全风险及治理策略研究[J]. 情报探索, 2025(8):43-48. |
| [9] | 黎昀瑜, 辛世成. 区块链嵌入流域治理的法治路径研究[J]. 海河水利, 2025(9):1-6. |
| [10] |
Perron B E, Luan Hui, Victor B G, et al. Moving beyond ChatGPT: local large language models (LLMs) and the secure analysis of confidential unstructured text data in social work research[J]. Research on Social Work Practice, 2025, 35(6): 695-710.
doi: 10.1177/10497315241280686 URL |
| [11] | 许林波, 柳经纬. 标准化视野下数据安全规范体系发展的困境与突破[J]. 标准科学, 2025(2):1-10. |
| [12] |
Kuo T T, Kim H E, Ohno-machado L. Blockchain distributed ledger technologies for biomedical and health care applications[J]. Journal of the American Medical Informatics Association, 2017, 24(6): 1211-1220.
doi: 10.1093/jamia/ocx068 URL |
| [13] |
Mothukuri V, Parizi R M, Pouriyeh S, et al. A survey on security and privacy of federated learning[J]. Future Generation Computer Systems, 2021, 115: 619-640.
doi: 10.1016/j.future.2020.10.007 URL |
| [14] | 路新喜, 郭建伟, 苑立娟, 等. 基于命名空间与文件系统代理的容器安全框架研究[J]. 信息网络安全, 2025, 25(8):1196-1207. |
| [15] | 高见, 何俊鹏, 苗青青. 基于多维度特征和LightGBM-AdaBoost的WebShell检测方法[J]. 信息网络安全, 2025, 25(8):1231-1239. |
| [16] | 王雅哲, 任磊, 冯登国, 等. 面向感算控智一体化融合的工业互联网新型PLC安全增强:趋势与展望[J]. 计算机学报, 2025, 48(3):738-762. |
| [17] | Chen Yiming. International experience and China’s approach to financial data governance[J]. Modern Economics & Management Forum, 2023, 4(6): 174-176. |
| [18] | Khan M A, Quasim M T, Alghamdi N S, et al. A secure framework for authentication and encryption using improved ECC for IoT-based medical sensor data[J]. IEEE Access, 2020(8): 52018-52027. |
| [19] | Borate I, R K. Sandboxing in Linux: from smartphone to cloud[J]. International Journal of Computer Applications, 2016, 148(8): 1-8. |
| [20] | Kaiser S, Haq M S, Tosun A S, et al. Container technologies for ARM architecture: a comprehensive survey of the state-of-the-art[J]. IEEE Access, 2022(10): 84853-84881. |
| [21] | 张媛. 计算机存储数据泄露漏洞自动检测方法[J]. 数字技术与应用, 2025, 43(8):66-68. |
| [22] | Li Qianyu, Wang Ruipeng, Li Dong, et al. DynPen: automated penetration testing in dynamic network scenarios using deep reinforcement learning[J]. IEEE Transactions on Information Forensics and Security, 2024(19): 8966-8981. |
| [23] |
Li Qianyu, Hu Miao, Hao Hao, et al. INNES: an intelligent network penetration testing model based on deep reinforcement learning[J]. Applied Intelligence, 2023, 53(22): 27110-27127.
doi: 10.1007/s10489-023-04946-1 |
| [24] | 张国敏, 张少勇, 张津威. 基于PPO算法的攻击路径发现与寻优方法[J]. 信息网络安全, 2023, 23(9):47-57. |
| [25] | 王永杰. 网络动态防御技术发展概况研究[J]. 保密科学技术, 2020(6):9-14. |
| [26] | Wu Xiaoyan, Zhang Manli, Ouyang Xu, et al. Research on the derivation and inheritance model of dynamic access control policies based on data lineage[C]// 2026 6th International Conference on Artificial Intelligence and Industrial Technology Applications (AIITA). New York: IEEE, 2026: 247-254. |
| [27] | Reeves M, Tian D J, Bianchi A, et al. Towards improving container security by preventing runtime escapes[C]// 2021 IEEE Secure Development Conference (SecDev). New York: IEEE, 2021: 38-46. |
| [28] | Krimmelbein F. Policy as code for governance enforcement: emerging trends in data governance[J]. Sogeti Labs Emerging Technology Review, 2025, 12(4): 28-41. |
| [1] | 陈玮, 田波, 李顺畅, 罗光春, 秦科, 王方圆. 基于高频特征增强与关键区域保护的人脸伪造检测方法[J]. 信息网络安全, 2026, 26(8): 1169-1182. |
| 阅读次数 | ||||||
|
全文 |
|
|||||
|
摘要 |
|
|||||